
Ghostwriter Uses Geofenced PDFs to Target Ukrainian Government
Summary
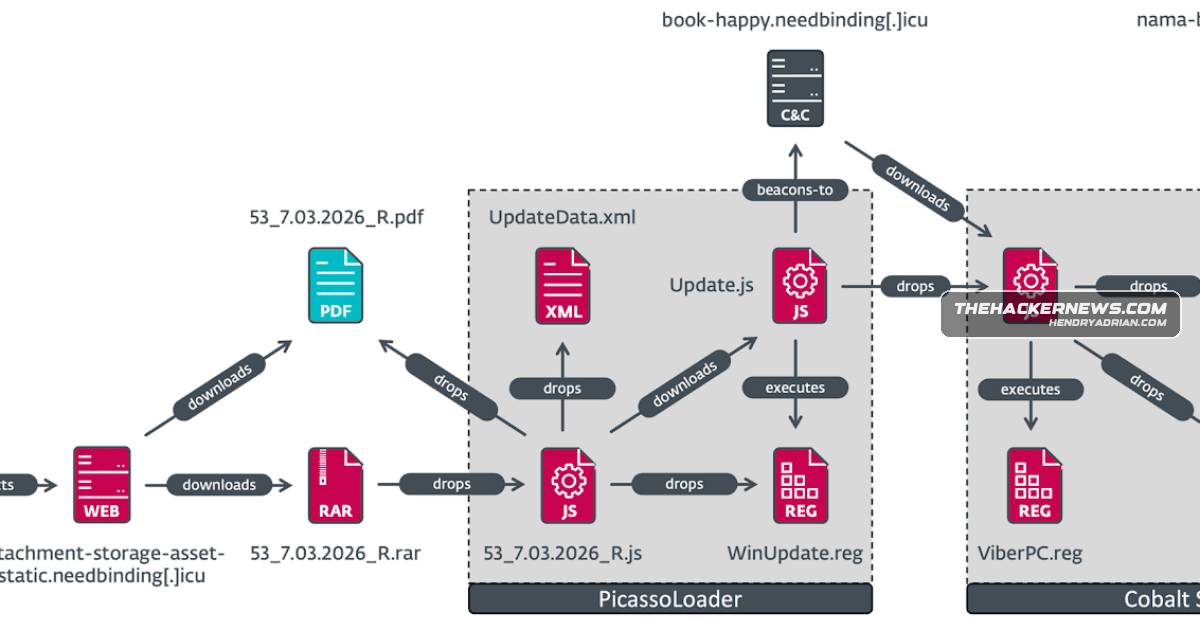
ESET reports Ghostwriter used geofenced spear-phishing PDFs impersonating Ukrtelecom to deliver PicassoLoader and Cobalt Strike to Ukrainian government targets. The article also summarizes campaigns attributed to Gamaredon, BO Team, and Hive0117.
Key points
- ESET observed Ghostwriter activity since March 2026 targeting Ukrainian government, military, and defense organizations with spear-phishing PDFs.
- The PDFs impersonate Ukrtelecom. A geofencing check serves a benign PDF to recipients whose IP address does not correspond to Ukraine.
- A linked RAR archive delivers a JavaScript PicassoLoader payload. Host fingerprinting is sent to attacker-controlled infrastructure every 10 minutes; operators may then choose to deliver a Cobalt Strike Beacon dropper.
- HarfangLab linked Gamaredon to phishing targeting Ukrainian state institutions since September 2025, using RAR archives to deliver GammaDrop and GammaLoad and exploiting CVE-2025-8088.
- Kaspersky reported possible coordination between BO Team and Head Mare based on overlapping tools and infrastructure; BO Team attacks also used the BrockenDoor backdoor and ZeroSSH.
- F6 attributed phishing against Russian enterprises to Hive0117, reporting more than 3,000 organizations targeted and over 14 million rubles stolen through fraudulent salary-like transfers.
Article Details
- Event Type
- Multi-group spear-phishing and malware deployment campaigns targeting organizations in Ukraine, Russia, and neighboring countries.
- Impact
- Ghostwriter campaigns observed since March 2026 target Ukrainian government organizations and focus primarily on military, defense, and government entities. The article also reports Gamaredon phishing Ukrainian state institutions, BO Team targeting up to 20 Russian organizations in the first quarter of 2026, and Hive0117 phishing more than 3,000 Russian organizations between February and March 2026. F6 reported that Hive0117 stole over 14 million rubles through fraudulent transfers from companies' accounts.
MITRE ATT&CK
T1059.005 · Visual BasicGamaredon reportedly used multi-stage VBScript downloaders.T1059.007 · JavaScriptGhostwriter's infection chain uses a JavaScript payload and may deliver a third-stage JavaScript dropper.T1105 · Ingress Tool TransferThe campaigns used downloaders and archives to deliver additional payloads, including PicassoLoader and Cobalt Strike.T1566.001 · Spearphishing AttachmentSpear-phishing attachments and malicious PDF lures were used in the reported campaigns.
CVE
CVE-2023-38831Rarlab · WinrarIn late 2023, the threat actor was also observed weaponizing a vulnerability in WinRAR (CVE-2023-38831, CVSS score: 7.8) to deploy PicassoLoader and Cobalt Strike.CVE-2024-42009Roundcube · Webmailend of a phishing campaign orchestrated by Ghostwriter that exploited a cross-site flaw in Roundcube (CVE-2024-42009, CVSS score: 9.3) to run malicious JavaScript responsible for capturing email login credentials.CVE-2025-8088Dtsearch · Dtsearch; Rarlab · Winrarwith an aim to deliver GammaDrop and GammaLoad downloader malware through RAR archives that exploit CVE-2025-8088.
People
Threat Actors
Black OwlIdentified in the article as an alternate name for BO Team, which was reported to conduct spear-phishing operations against Russian organizations.BO TeamThe article reports BO Team's spear-phishing operations against Russian organizations and says the group may be working with Head Mare; Kaspersky cited overlapping tools and infrastructure, while noting that coordination remains unclear.FrostyNeighborIdentified in the article as a tracking moniker for Ghostwriter; the cited ESET reporting describes ongoing cyber operations targeting Eastern Europe.GamaredonThe article says Gamaredon was linked to spear-phishing targeting Ukrainian state institutions since September 2025, using GammaDrop and GammaLoad.Head MareThe article says Head Mare may be working with BO Team in attacks against Russian organizations; Kaspersky cited overlapping tools and infrastructure but said the nature of the interaction remains unclear.Hive0117The article attributes financially motivated phishing campaigns targeting Russian enterprises and users in neighboring countries to Hive0117; F6 reported theft of over 14 million rubles through fraudulent transfers.PhantomCoreIdentified in the article as an alternate name for Head Mare, which may be working with BO Team in attacks against Russian organizations.PUSHCHAIdentified in the article as a tracking moniker for Ghostwriter, which was attributed to spear-phishing attacks against Ukrainian government organizations.RepeatingUmbraIdentified in the article as the former name associated with Umbral Bison, a tracking moniker for Ghostwriter.Storm-0257Identified in the article as a tracking moniker for Ghostwriter, which was attributed to spear-phishing attacks against Ukrainian government organizations.TA445Identified in the article as a tracking moniker for Ghostwriter, which was attributed to spear-phishing attacks against Ukrainian government organizations.UACâ0057Identified in the article as a tracking moniker for Ghostwriter, which was attributed to spear-phishing attacks against Ukrainian government organizations.UMBRAL BISONIdentified in the article as a tracking moniker for Ghostwriter; the article says this name was formerly RepeatingUmbra.UNC1151The article attributes recent spear-phishing attacks against Ukrainian government organizations to Ghostwriter, a Belarus-aligned group. The group has also been linked to cyber espionage and influence operations.White LynxIdentified in the article as a tracking moniker for Ghostwriter, which was attributed to spear-phishing attacks against Ukrainian government organizations.
Malware
BrockenDoorAttacks orchestrated by the BO Team in 2026 have employed spear-phishing to serve BrockenDoor and ZeronetKit, the latter of which is capable of also compromising Linux systems.DarkWatchman#GhostwriterGammaDrop#GhostwriterGammaLoad#GhostwriternjRATPrevious attacks mounted by the hacking crew have leveraged a malware family known as PicassoLoader, which then acts as a conduit for Cobalt Strike Beacon and njRAT.PicassoLoaderGhostwriter has launched new spear-phishing attacks against Ukrainian government organizations, using malicious PDFs, geofencing, and a JavaScript version of PicassoLoader to deploy Cobalt Strike.ZeronetKitAttacks orchestrated by the BO Team in 2026 have employed spear-phishing to serve BrockenDoor and ZeronetKit, the latter of which is capable of also compromising Linux systems.ZeroSSH#Ghostwriter
Products
Roundcube Webmailreceiving end of a phishing campaign orchestrated by Ghostwriter that exploited a cross-site flaw in Roundcube (CVE-2024-42009, CVSS score: 9.3) to run malicious JavaScript responsible for capturing email loginWinRARIn late 2023, the threat actor was also observed weaponizing a vulnerability in WinRAR (CVE-2023-38831, CVSS score: 7.8) to deploy PicassoLoader and Cobalt Strike.
Tools
Countries
BelarusThe Belarus-aligned threat group known as Ghostwriter has been attributed to a fresh set of attacks targeting governmental organizations in Ukraine.EstoniaBesides Russia, the activity has also targeted users from Lithuania, Estonia, Belarus, and Kazakhstan.KazakhstanBesides Russia, the activity has also targeted users from Lithuania, Estonia, Belarus, and Kazakhstan.Lithuaniadefense sector, and governmental organizations in Ukraine, whereas the victimology in Poland and Lithuania is much broader, targeting industrial and manufacturing, healthcare and pharmaceuticals, logistics, andPolandaround military, defense sector, and governmental organizations in Ukraine, whereas the victimology in Poland and Lithuania is much broader, targeting industrial and manufacturing, healthcare and pharmaceuticals,RussiaThe disclosure comes as the Russia-affiliated Gamaredon hacking group has been tied to a spear-phishing campaign targeting Ukrainian state institutions since September 2025, with an aim to deliver GammaDrop andUkraineThe wider report also highlights Gamaredon’s Ukraine-focused campaigns, BO Team-linked operations against Russian organizations, and Hive0117’s phishing activity for financial theft.
Industries
DefenseThe activity primarily appears to center around military, defense sector, and governmental organizations in Ukraine, whereas the victimology in Poland and Lithuania is much broader, targeting industrial andGovernmentGhostwriter has launched new spear-phishing attacks against Ukrainian government organizations, using malicious PDFs, geofencing, and a JavaScript version of PicassoLoader to deploy Cobalt Strike.Healthcarethe victimology in Poland and Lithuania is much broader, targeting industrial and manufacturing, healthcare and pharmaceuticals, logistics, and government sectors.Industrialorganizations in Ukraine, whereas the victimology in Poland and Lithuania is much broader, targeting industrial and manufacturing, healthcare and pharmaceuticals, logistics, and government sectors.logisticsand Lithuania is much broader, targeting industrial and manufacturing, healthcare and pharmaceuticals, logistics, and government sectors.Manufacturingin Ukraine, whereas the victimology in Poland and Lithuania is much broader, targeting industrial and manufacturing, healthcare and pharmaceuticals, logistics, and government sectors.MilitaryThe activity primarily appears to center around military, defense sector, and governmental organizations in Ukraine, whereas the victimology in Poland and Lithuania is much broader, targeting industrial andPharmaceuticalsin Poland and Lithuania is much broader, targeting industrial and manufacturing, healthcare and pharmaceuticals, logistics, and government sectors.