
U.S. House Committee Seeks Instructure Testimony on Canvas Attacks
Summary
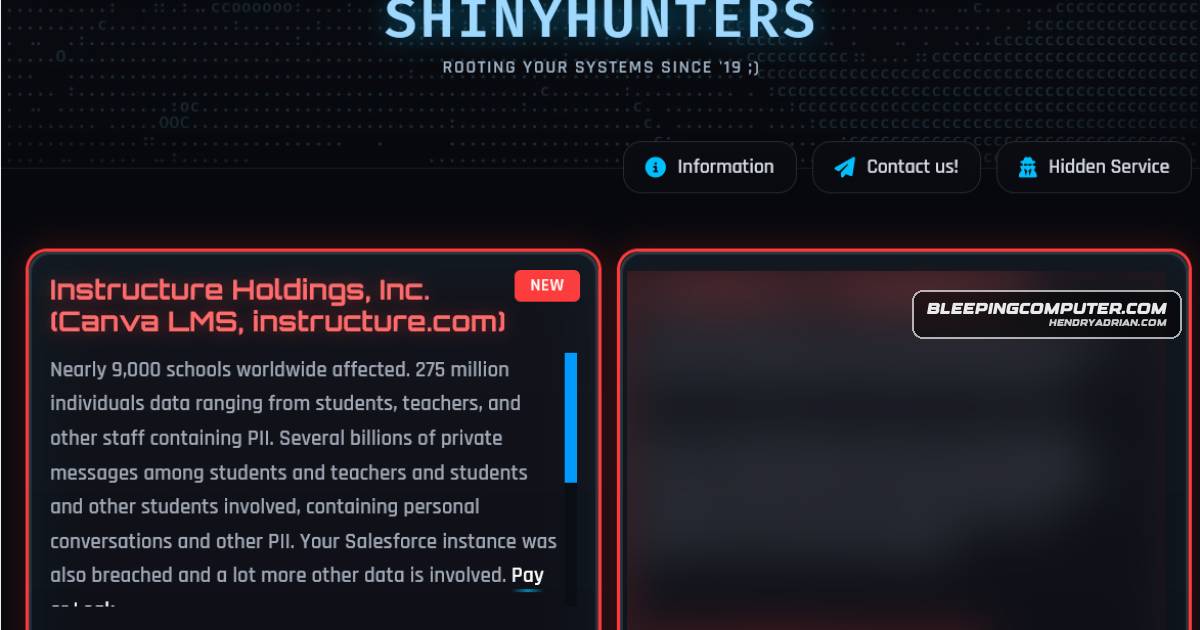
The House Homeland Security Committee seeks an Instructure briefing on two reported ShinyHunters attacks on Canvas, including a confirmed data breach and login-page defacements that disrupted exams.
Key points
- Instructure said it detected an intrusion on April 29 and disclosed the breach on May 3; exposed data included names, email addresses, student IDs, and platform messages.
- Instructure said the exposed data did not include passwords, financial information, or government identifiers.
- ShinyHunters claimed it stole 280 million records from 8,809 education organizations; this figure is the group’s claim.
- A second attack defaced Canvas login portals and disrupted exam activities at schools in multiple states; some colleges canceled exams.
- BleepingComputer reported that attackers used multiple cross-site scripting (XSS) vulnerabilities to obtain authenticated admin sessions and modify login pages.
- The House Homeland Security Committee asked Instructure or a senior representative to brief lawmakers by May 21 on both intrusions, containment, notifications, and federal coordination.
- Instructure said it reached an agreement with ShinyHunters to stop the public leak and ensure the data was deleted; the company did not confirm that it paid a ransom.
Article Details
- Event Type
- Cyberattacks, data theft, and service disruption followed by a congressional investigation.
- Impact
- The attacks exposed student and staff names, email addresses, student identification numbers, and messages exchanged on Canvas, and defaced school login portals, disrupting end-of-semester activities and causing some colleges to cancel exams. Instructure said the exposed data did not include passwords, financial information, or government identifiers. ShinyHunters claimed it stole 280 million records from 8,809 education organizations. Instructure later said it reached an agreement with the group to stop the public leak and ensure the data was deleted; the company did not confirm whether it paid a ransom.