
Microsoft Says MDASH AI System Found 16 Windows Flaws Fixed in Patch Tuesday
Summary
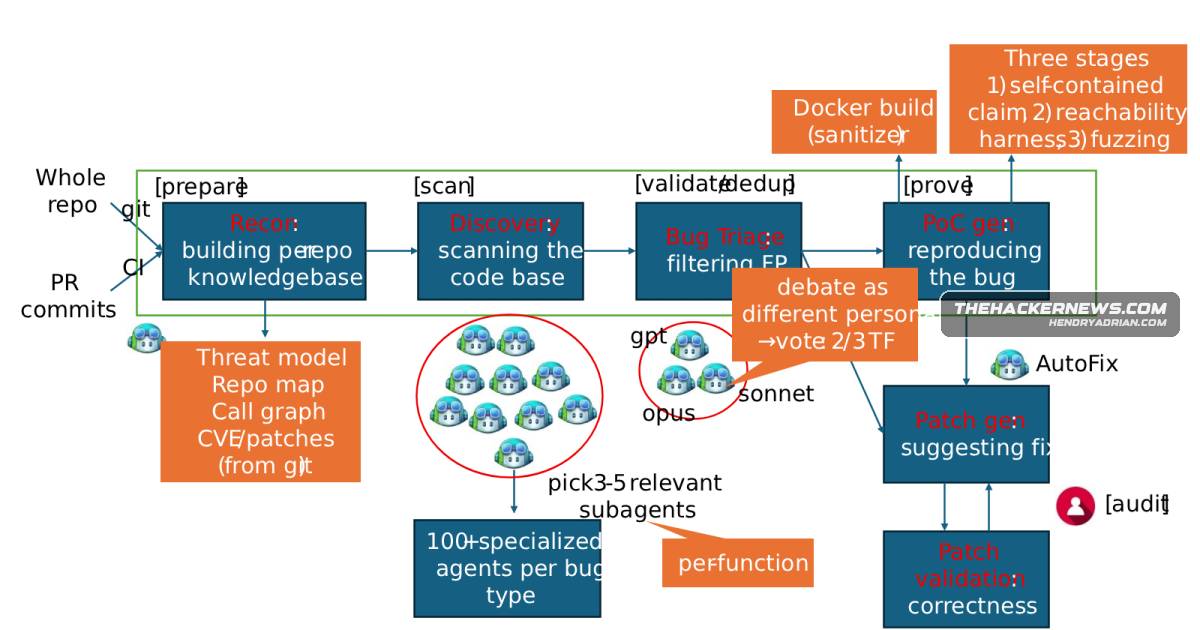
Microsoft says its MDASH system, which coordinates more than 100 specialized AI agents, found 16 Windows flaws fixed in the latest Patch Tuesday update. Two listed flaws could enable remote code execution.
Key points
- Microsoft describes MDASH as a model-agnostic system using more than 100 specialized agents to discover, validate, and prove vulnerabilities.
- Its pipeline analyzes source code and attack surfaces, reviews candidate issues with auditor and debater agents, groups similar findings, and attempts to prove vulnerabilities.
- Microsoft says MDASH helped identify 16 vulnerabilities fixed in its latest Patch Tuesday release; the system is in limited private preview with some customers.
- CVE-2026-33824 is described as a double-free in ikeext.dll that could allow remote code execution via crafted packets when IKEv2 is enabled.
- CVE-2026-33827 is described as a race condition in Windows TCP/IP that could allow remote code execution via a crafted IPv6 packet when IPSec is enabled.
- Microsoft says the vulnerabilities span Windows networking and authentication components.
Article Details
- Event Type
- Microsoft introduced MDASH, a multi-model AI system for vulnerability discovery, validation, and proof.
- Impact
- MDASH helped identify 16 vulnerabilities fixed in Microsoft’s latest Patch Tuesday release. Two critical Windows networking flaws, CVE-2026-33824 and CVE-2026-33827, could allow remote code execution under the conditions described in the article. MDASH is being tested by some customers in a limited private preview.
CVE
CVE-2026-33824Microsoft · Windows 10 Version 1607; Microsoft · Windows 10 Version 1809; +14 moreThe system has already helped uncover 16 flaws fixed in the latest Patch Tuesday release, including CVE-2026-33824 and CVE-2026-33827.CVE-2026-33827Microsoft · Windows 10 Version 1607; Microsoft · Windows 10 Version 1809; +18 moreThe system has already helped uncover 16 flaws fixed in the latest Patch Tuesday release, including CVE-2026-33824 and CVE-2026-33827.
People
Vendors
Products
Microsoft Defender for AI SecurityMicrosoft has introduced MDASH, a multi-model AI system that uses more than 100 specialized agents to discover, validate, and prove vulnerabilities in complex codebases like Windows.Microsoft WindowsMicrosoft has introduced MDASH, a multi-model AI system that uses more than 100 specialized agents to discover, validate, and prove vulnerabilities in complex codebases like Windows.