
Qilin Claims Acosol as Ransomware Victim in Spain
Ransomware.live recorded a Qilin claim targeting Acosol in Spain. The post says systems were encrypted and disrupted, but those claims are unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2808 articles
Ransomware.live recorded a Qilin claim targeting Acosol in Spain. The post says systems were encrypted and disrupted, but those claims are unconfirmed.
Ransomware.live reports that Qilin claimed Cafar, an Argentine agriculture and food production organization. The post says files were encrypted and operations disrupted, but notes that the group’s claims are unconfirmed.

Ransomware.live lists Sunway Scientific as a claimed victim of thegentlemen, which reportedly claimed access to the Taiwanese distributor’s systems. The claim is unconfirmed.
A ransomware claim by thegentlemen names Indiana-based Advantage Home Health Care. The post says in-home care operations were allegedly impacted, but the claim is unconfirmed.
Thegentlemen claims it obtained Military Sealift Command ITAR documents, personal data, cargo manifests and vessel blueprints, and threatens publication. The monitoring post says the claims are unconfirmed.
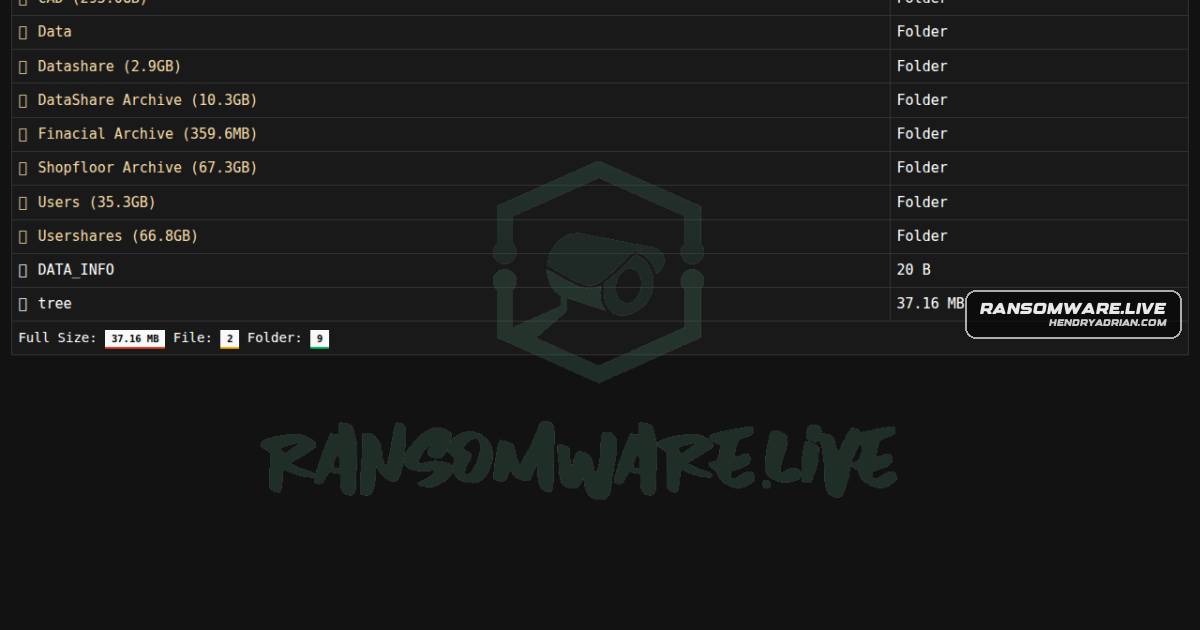
Interlock claims it exposed Paragon Store Fixtures’ internal design files, contracts, architectural plans, and client project details. The monitoring post says the allegations are unconfirmed.
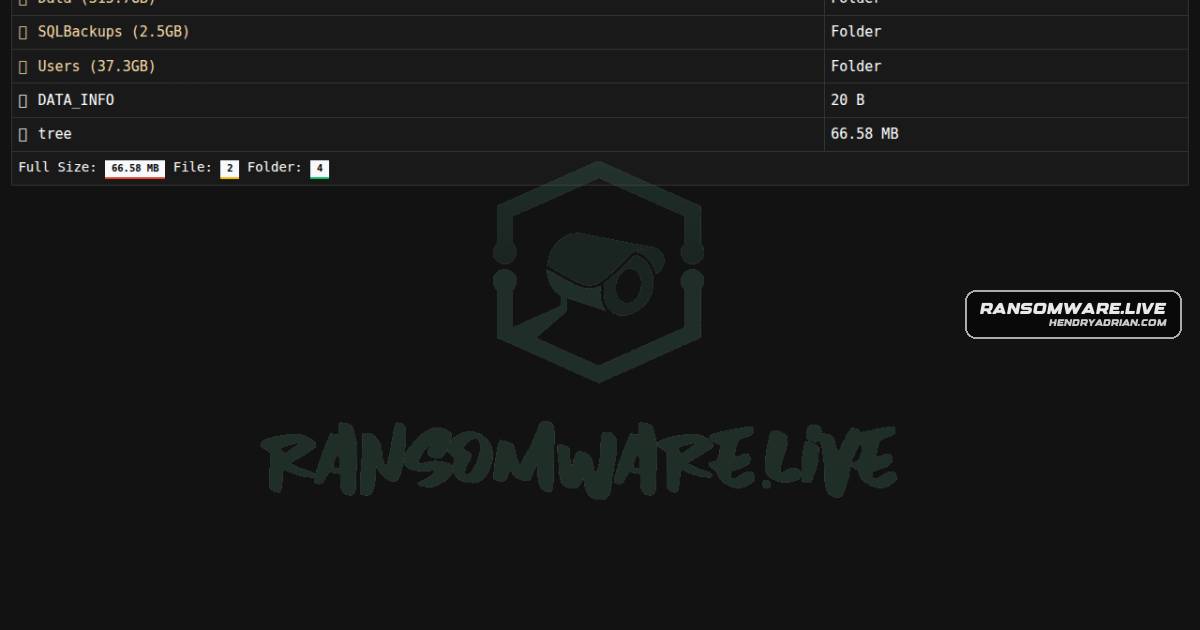
Interlock claims to have compromised Centre for Newcomers in Canada and offers 380 GB of reportedly stolen data, including immigration client records, financial information, and HR material; the report says the claim is unconfirmed.
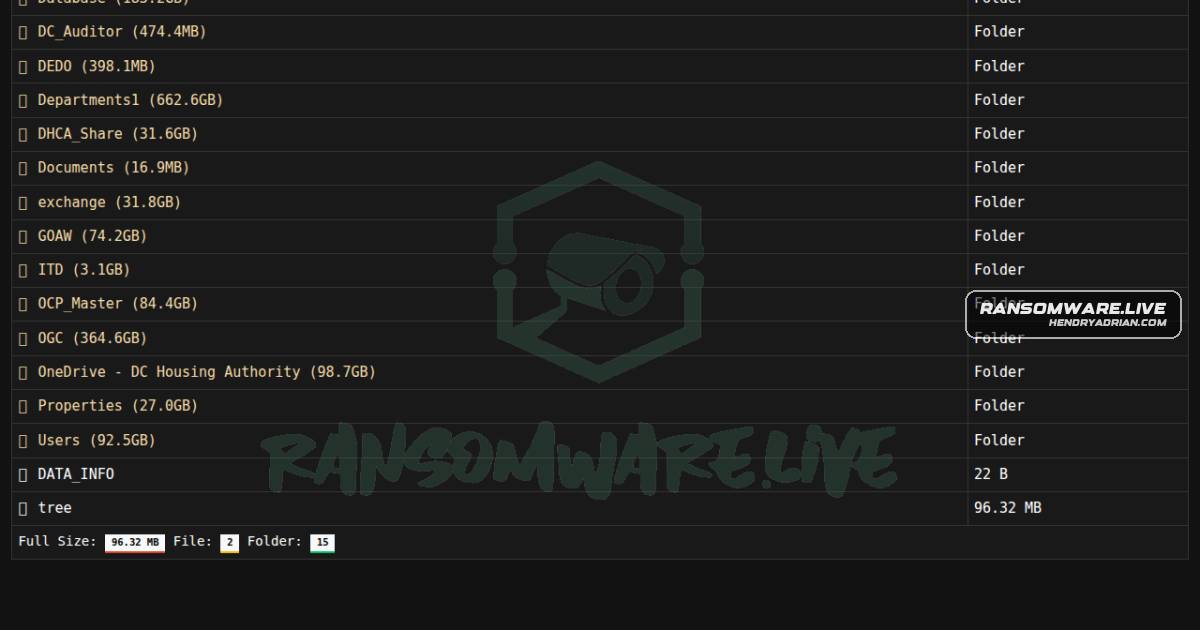
Interlock claims it stole 1.6 TB of data from the District of Columbia Housing Authority, including residents’ personal information. The claim is unconfirmed and was monitored by ransomware[.]live.

ransomware.live reports an unverified m3rx claim that Arambol LLP had 922 GB of data across 584,228 files stolen. The article says it cannot confirm the claim.

The ransomware.live listing records an unverified ransomware claim by actor m3rx against SuppCenter Global Services in South Africa. The post says it is based on public group claims and has not been independently confirmed.
Ransomware.live records a claim by krybit targeting LAGUS s.r.o., associated with www[.]lagus[.]cz. The post is based on the group's public claim; its accuracy is unconfirmed.
Krybit claimed PERKESO Rehabilitation Centre Malaysia was a ransomware victim. The claim was listed on July 17, 2026, and is unconfirmed; ransomware.live says it could not verify the information.

Nova allegedly claimed it encrypted systems and stole data from Integrated Marketing Services in Liverpool, New York. The monitoring post says Nova provided a tree and data samples; the claim is unconfirmed.

Nova reportedly targeted Digipro, a Vietnamese IT company, and claimed to have stolen data. The group allegedly shared a file tree and data samples with the company’s support department; the claim is unconfirmed.

Nova claims it targeted PHI Studio with ransomware and says purportedly stolen data samples are available. The claim is unverified; ransomware.live monitored the listing.
A ransomware.live monitoring record attributes to incransom an unconfirmed claim that it accessed and encrypted Kyokuto Kaihatsu Kogyo data and affected operations in Japan.
Ransomware.live lists Formas Universales, S.A. (formasuniversales[.]com) as a claimed victim of the Krybit ransomware actor, citing the group’s blog. The claim was published July 17, 2026, and is unconfirmed.
A ransomware.live listing attributes a ransomware claim against Eitz Chaim Schools in Israel to krybit. The post says the claim is based on the group’s public statements and that it has not been independently confirmed.
A ransomware.live monitoring record names UK-based Wring Group as a Play ransomware claim. The post alleges disruption and potential encryption demands, but the publisher says it cannot confirm the information.
A ransomware.live monitoring post attributes a ransomware claim involving Boston Electric and Telephone to the Play group. The post says unauthorized access and disruption were claimed but states the information is unconfirmed.
ransomware.live reports Gunra’s claim that Dissinger and Dissinger Law Firm was attacked, with files encrypted, a ransom demanded, and operations disrupted. The claims are unconfirmed.
Ransomware.live records an unverified Play ransomware claim targeting Andorra Life. The post says it cannot confirm the claim’s accuracy and gives conflicting locations: Andorra and the United States.
The Play ransomware group claims it targeted Netherlands-based AG Scholtes, with encryption and extortion demands reported. The claim is unconfirmed.
Thegentlemen claimed an attack on Tangram Interiors involving client personal data and approximately 400+ GB of information. The claim is unconfirmed.