
Play ransomware group claims attack on Andorra Life
Summary
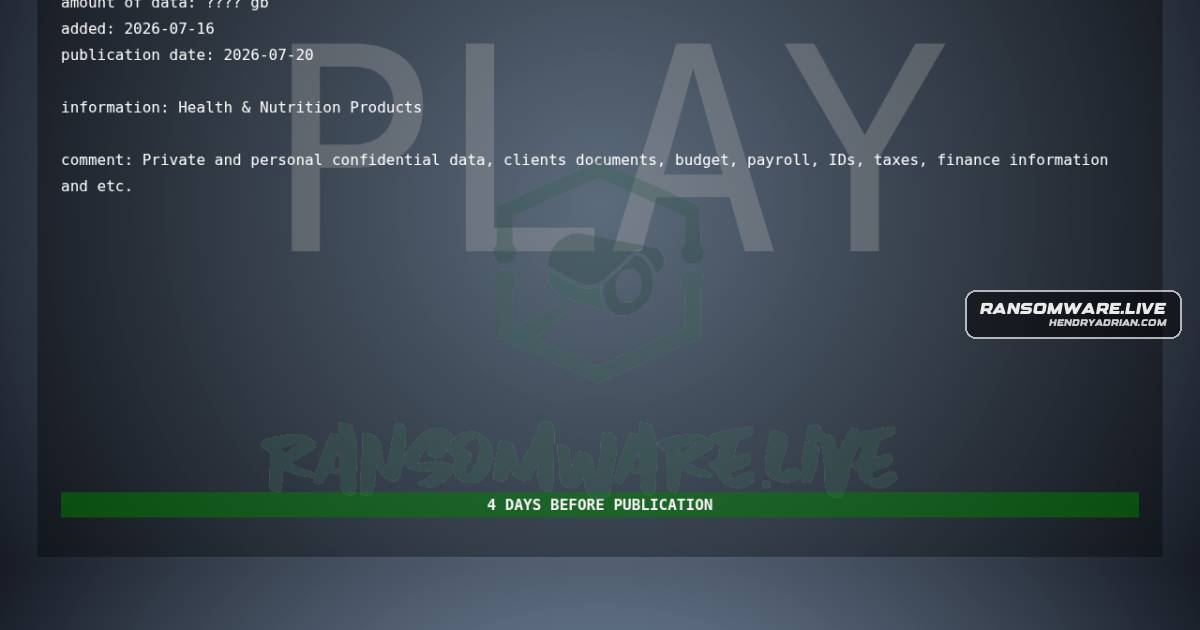
Ransomware.live records an unverified Play ransomware claim targeting Andorra Life. The post says it cannot confirm the claim’s accuracy and gives conflicting locations: Andorra and the United States.
Key points
- The record names Andorra Life as the victim and Play as the actor, and attributes the information to public claims by the ransomware group.
- The post describes an intrusion and encryption or disruption for extortion, but these details are unverified claims, not independently confirmed facts.
- The record lists a discovery date of July 16, 2026.
- The article describes the victim as being in Andorra but also says the targeting occurred in the United States. It provides no clarification.
Article Details
- Victim
- Andorra Life
- Victim Domain
- Unknown
- Encryption Status
- Unconfirmed: the source reports a public group claim that data was encrypted or disrupted.
- Exfiltration Status
- Unknown
- Ransom Demand
- Unknown
- Leak Status
- Unknown: the source reports a group claim but does not confirm publication of victim data.