
Play ransomware group claims attack on AG Scholtes
Summary
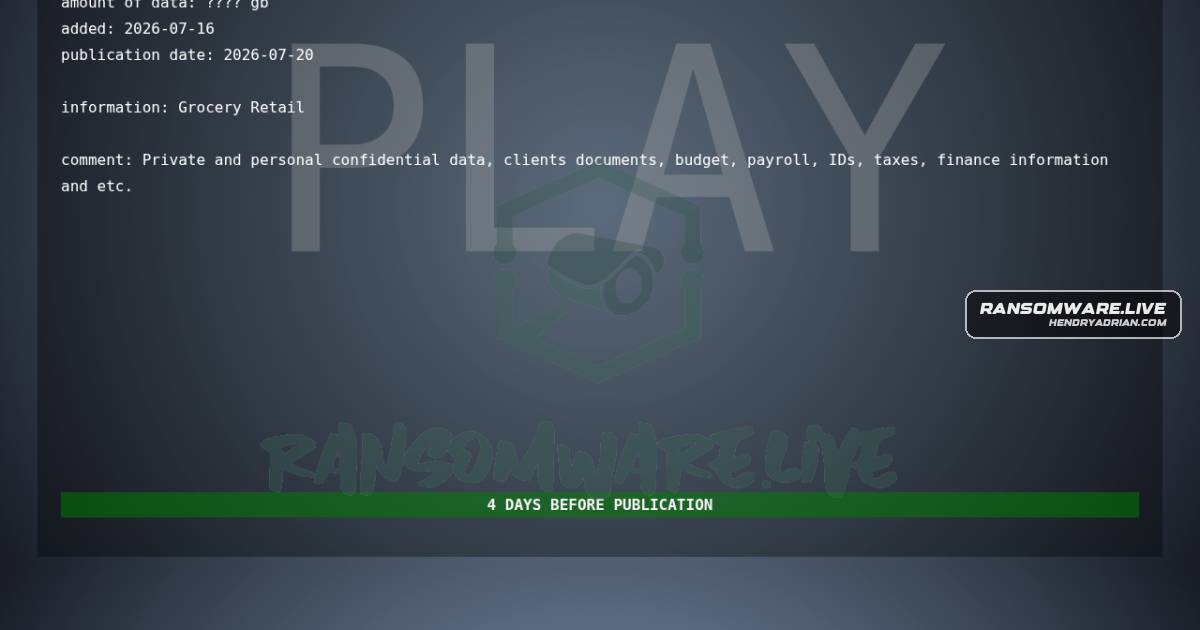
The Play ransomware group claims it targeted Netherlands-based AG Scholtes, with encryption and extortion demands reported. The claim is unconfirmed.
Key points
- AG Scholtes, a Netherlands-based manufacturing organization, is named as the alleged victim.
- The post attributes the ransomware claim to the Play group and links it to a leak-site listing.
- The post reports malicious encryption and extortion demands but provides no independent confirmation.
- The claim was discovered and published on July 16, 2026.
Article Details
- Victim
- AG Scholtes
- Claim Date
- 2026-07-16
- Encryption Status
- Reported as malicious encryption, but unconfirmed; the source says its information is based on claims by the ransomware group.
- Ransom Demand
- Extortion demands are reported, but this is unconfirmed and no amount is disclosed.
- Leak Status
- A group claim is reported; publication or authenticity of victim data is not confirmed.