
Interlock Claims Paragon Store Fixtures Files Were Exposed
Summary
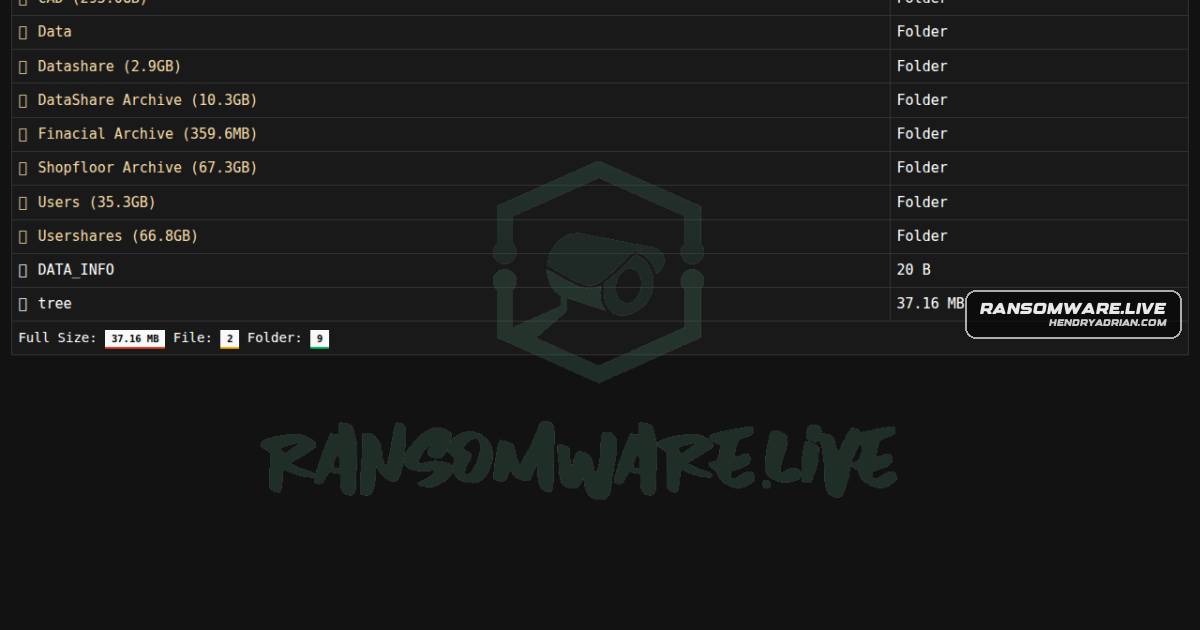
Interlock claims it exposed Paragon Store Fixtures’ internal design files, contracts, architectural plans, and client project details. The monitoring post says the allegations are unconfirmed.
Key points
- The monitoring record attributes the claim to the Interlock threat actor and names Paragon Store Fixtures as the victim.
- The group’s claim alleges exposure of internal design files, contracts, architectural plans, partnership agreements, and client and project identities.
- The post says it cannot confirm the claim’s accuracy and invites an official statement from the company.
Article Details
- Victim
- Paragon Store Fixtures
- Victim Domain
- Not disclosed
- Attack Date
- 2026-07-17
- Claim Date
- 2026-07-17
- Encryption Status
- Unknown
- Encrypted Size
- Unknown
- Exfiltration Status
- Unverified; the ransomware group's claim alleges that internal files and client information were exposed.
- Exfiltrated Data
- The claim alleges exposure of internal design files, architectural plans, contracts, partnership agreements, project details, and client and project identities.
- Exfiltrated Size
- Unknown
- Ransom Demand
- Unknown
- Leak Status
- Unverified; the group claims information was made public, but the article states it cannot confirm the claim.