
Global Secret Group Claims Mesan USA Data Exposure
A ransomware.live record attributes a claim of 184 GB of exposed Mesan USA data to Global Secret Group. The post says the claim could not be confirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2777 articles
A ransomware.live record attributes a claim of 184 GB of exposed Mesan USA data to Global Secret Group. The post says the claim could not be confirmed.
A ransomware.live post records Panzer’s claim of an attack on engineering consultancy Aqualogus, reporting operational disruption. The post says the group’s claims could not be confirmed.
A ransomware.live monitoring post records a LockBit5 claim naming Brazil’s AmorSaúde clinic network as a victim. The post cites September 9, 2026 dates and says the claim’s accuracy is unconfirmed.
Ransomware.live reports that AuditTeam claimed to target German organization mo***al with ransomware. The post says the group’s claims are unconfirmed.

The Akira ransomware group claims it will publish 30 GB of Kyodo USA data, allegedly including employee IDs, passports, Social Security numbers, financial records, and customer files. The claims are unconfirmed.
A ransomware.live monitoring post reports direwolf’s claim that it targeted RelyComply AML Platform, a Great Britain-based financial software company. The post says the claim is unconfirmed.
Incransom claimed it attacked Mediengruppe Thiel in Ludwigsfelde, Germany, and disrupted operations through data encryption. The report says the claim could not be confirmed.
Ransomware group Storm claimed an attack on Lowerys, a Canadian office supplies and printing provider. The monitoring post cites the group’s claim but says it could not confirm its accuracy.
Storm ransomware operators claimed to have targeted Flexmaster, a Canadian manufacturing company in the Novaflex Group. The post lists publication and discovery dates but says the claim could not be confirmed.
Ransomware group Storm claims it compromised Technology Dynamics and obtained SolidWorks designs and firmware source code. The claim has not been independently confirmed.
A ransomware.live record says Safepay claimed an attack on Spanish ceramics manufacturer Gayafores, with operational disruption and data-access impacts alleged. The post says the claims are unconfirmed.
SafePay claims it attacked Italian professional-services firm assiprime.it. The ransomware.live post says systems were encrypted or disrupted but notes the claim is unverified.
Safepay claimed responsibility for an attack on cannonpuntana.com in Argentina, with reported operational disruption and data unavailability. The monitoring post says the group’s claims could not be confirmed.
Ransomware.live records an unverified Safepay claim targeting reichenau.at in Austria, published and discovered on September 8, 2026. The post says it cannot confirm the claim.
A ransomware.live monitoring post records SafePay’s claim targeting Palmetto Eye Institute in the US. The post says operations were disrupted but notes the group’s claims are unverified.
GT Distributors was listed as a ransomware victim by the Play group. The monitoring post attributes the claim to the group and says it could not confirm its accuracy.
A ransomware.live monitoring post says the Play group claimed an attack on Red Star Oil involving encryption and operational disruption. The post says the claims are unverified.
A ransomware.live monitoring post attributes a public claim naming US-based Sales Boomerang to the direwolf actor. The post says the claim has not been independently confirmed.
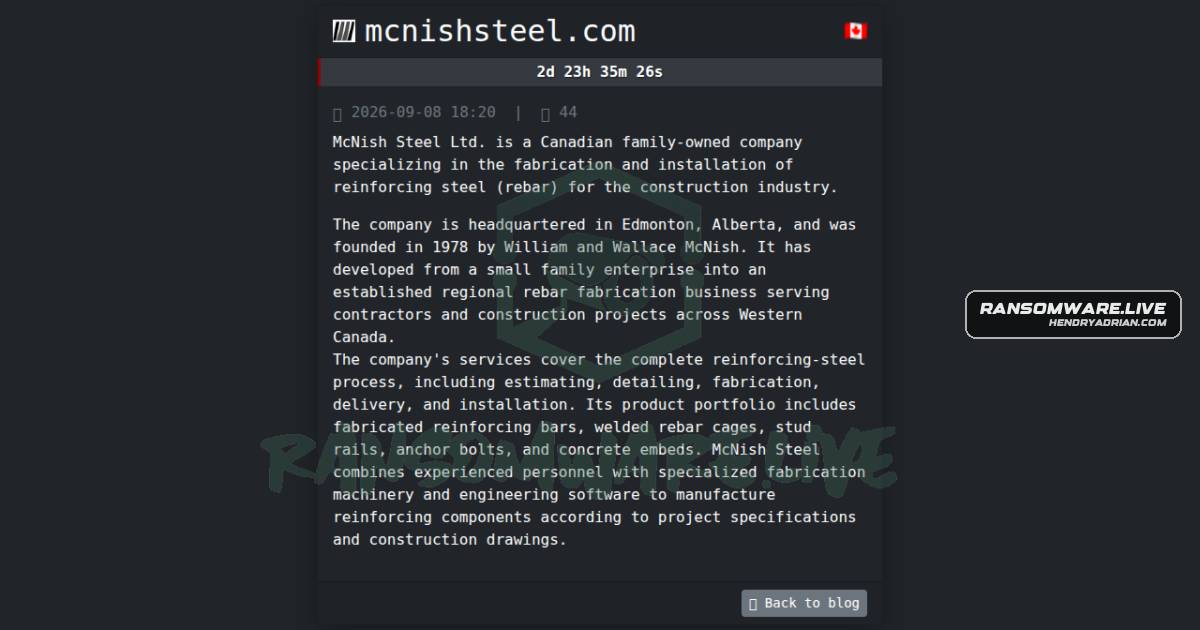
A ransomware.live monitoring post records Safepay’s claim that Canadian manufacturer mcnishsteel[.]com was targeted. The post says the claim could not be independently confirmed.
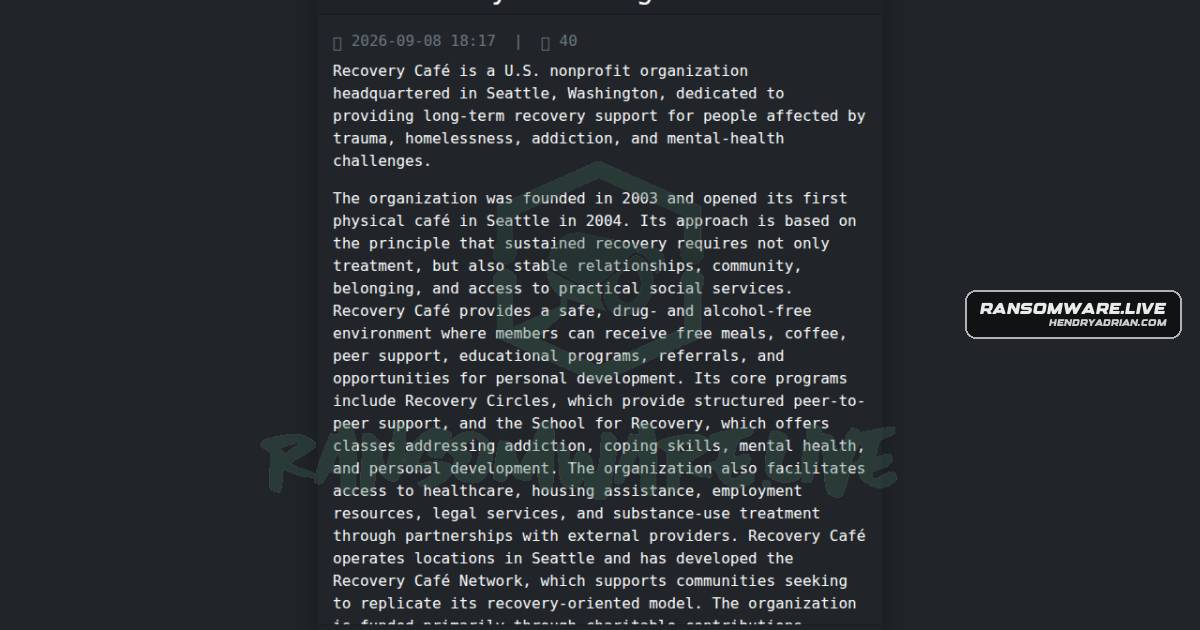
A ransomware.live monitoring post attributes a claim involving RecoveryCafe.org to SafePay, with a September 8, 2026 publication date. The post says the information comes from the group and could not be confirmed.
Akira claims it stole and encrypted CreateASoft corporate data, including employee and customer files, contacts, agreements, financial records, and project information. The post says the claims are unconfirmed.
A ransomware.live record attributes claims of threatened data exfiltration and encryption at Brentwood Country Club to Akira. The source says the claims are unconfirmed and lists potentially exposed personal and corporate data.
The ransomware group Akira claims Brent Electric, a UK electrical services company, has corporate data—including employee documents and financial and customer files—that it plans to upload. The claims are unconfirmed.
A ransomware monitoring post says AuditTeam targeted Ukrainian technology company Wi***IT, encrypting files, disrupting operations, and demanding ransom. The post says the group’s claims are unconfirmed.