
Safepay Claims Ransomware Attack on Argentine Business
Summary
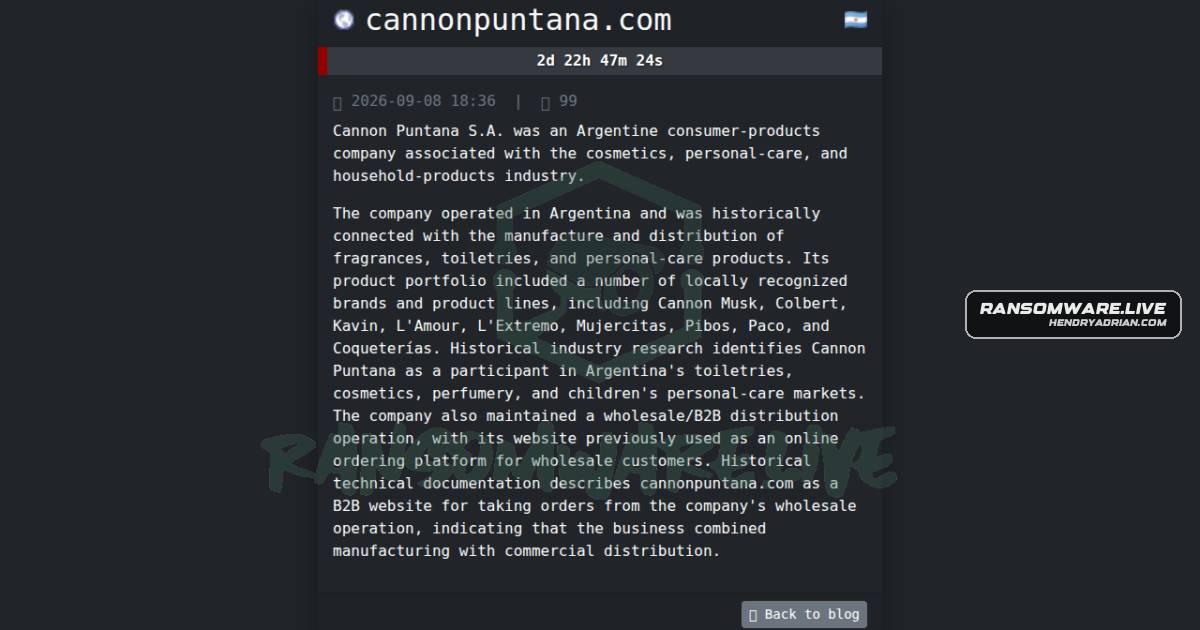
Safepay claimed responsibility for an attack on cannonpuntana.com in Argentina, with reported operational disruption and data unavailability. The monitoring post says the group’s claims could not be confirmed.
Key points
- The monitoring record identifies cannonpuntana.com in Argentina as the claimed victim.
- The claim is attributed to the Safepay ransomware group and linked to its post on an .onion site.
- The post reports operational disruption and data unavailability, but says the claims could not be confirmed.
- The claim was published and discovered on September 8, 2026.
Article Details
- Victim
- cannonpuntana.com
- Victim Domain
- cannonpuntana.com
- Claim Date
- 2026-09-08
- Encryption Status
- Unknown; the source does not confirm encryption.
- Exfiltration Status
- Unknown; the source does not confirm exfiltration.
- Ransom Demand
- Unknown; none is reported in the source.
- Leak Status
- safepay published a claim about the victim on its blog. The source says the claim is unverified; it does not confirm that data was leaked or published.