
AuditTeam Claims Ransomware Attack on Wi***IT in Ukraine
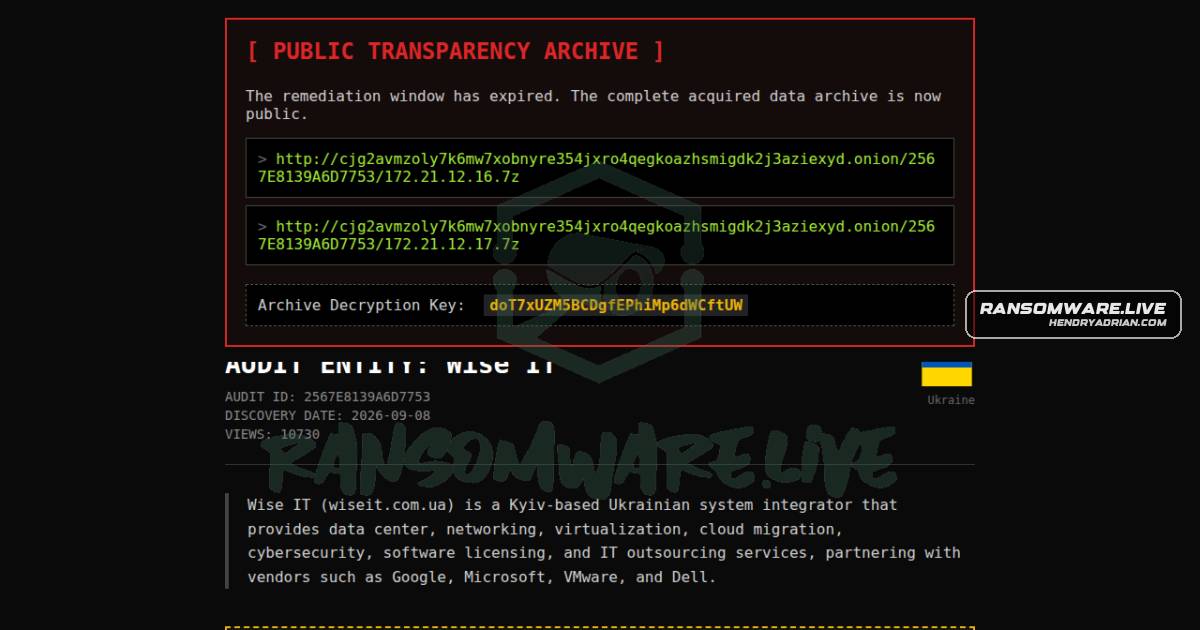
Summary
A ransomware monitoring post says AuditTeam targeted Ukrainian technology company Wi***IT, encrypting files, disrupting operations, and demanding ransom. The post says the group’s claims are unconfirmed.
Key points
- The post identifies Wi***IT, a technology company in Ukraine, as the alleged victim.
- The claim is attributed to ransomware group AuditTeam.
- The post says files were encrypted, operations disrupted, and ransom demanded to restore access.
- The incident was listed as discovered on September 8, 2026, and published on the same date.
- The post states it cannot confirm the ransomware group's claims.
Article Details
- Victim
- Wi***IT
- Claim Date
- 2026-09-08
- Encryption Status
- Reported by the ransomware group; not independently confirmed.
- Exfiltration Status
- Unknown; not reported.
- Ransom Demand
- The article reports a ransom demand to restore access, based on the group's public claims; the amount is not disclosed.
- Leak Status
- Unknown; the article does not report a leak or publication of victim data.