cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

624 articles

Detection & Defense · socprime.com

How to Find, Export, and Investigate SSH Logs on Linux

A practical guide to locating and exporting SSH logs across Linux distributions, interpreting authentication events, and checking for suspicious logins. It covers permissions, journal retention, rotated files, timestamps, and OpenSSH 9.8 log tags.
Oct 21, 2026
Detection & Defense · socprime.com

Guide Compares Log Analysis Tools and Demonstrates a LogTotal Investigation Workflow

A guide compares 10 log analysis tools and walks through exporting Windows and Linux logs, sanitizing them, and analyzing them with LogTotal. The vendor says LogTotal correlates findings into attack chains and does not retain logs.

Oct 21, 2026
Detection & Defense · aikido.dev

Software Supply Chain Security Best Practices for 2026

Aikido’s guide recommends package-age gates, lockfile and commit-SHA pinning, scoped credentials, developer-device protections, AI-agent sandboxing, and audit logs to reduce software supply chain risk.

Oct 21, 2026
Detection & Defense · abstract.security

PHP2Shell: Emergency PHP Fixes and Detection Guidance for Two Critical RCE Flaws

PHP released fixes for CVE-2026-109618 and CVE-2026-109619 on October 21, 2026. The article details separate WAF signatures, detection rules and compromise hunts for the two unauthenticated RCE flaws, stressing that patching is the only complete remedy.

Oct 21, 2026
Detection & Defense · huntress.com

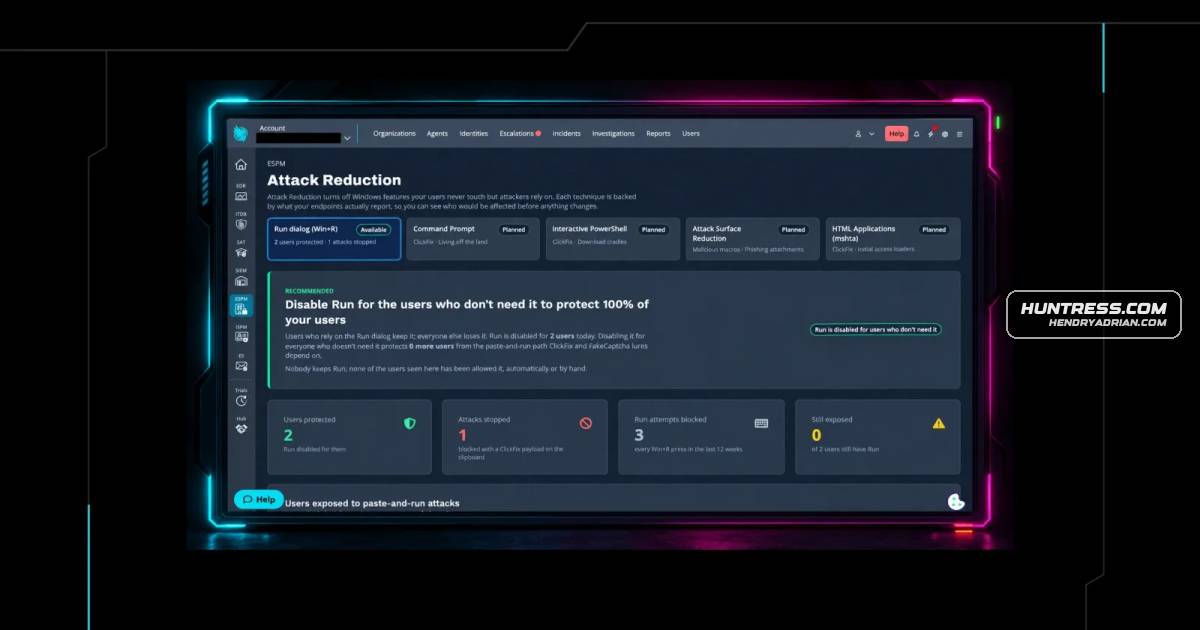
Huntress Attack Reduction Blocks Windows Run Dialog to Disrupt ClickFix

Huntress introduced an Early Access feature that baselines Windows Run dialog use and can block the shortcut for users who do not need it, disrupting a common ClickFix method. Further command-line controls are planned.

Oct 21, 2026
Detection & Defense · cybersecuritypulse.net

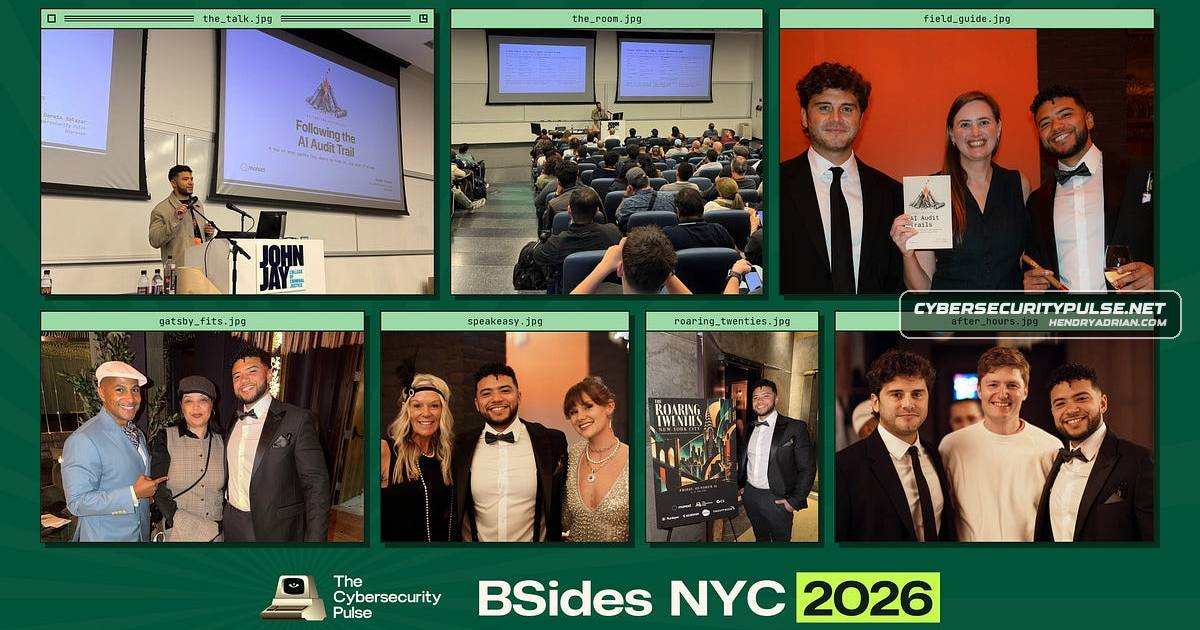
BSides NYC Talk Explains How to Collect and Correlate AI Audit Logs

A BSides NYC presentation outlined what AI platform, runtime, transcript, and endpoint logs capture, how to correlate events, and why rejected tool calls matter. Some client telemetry must be enabled in advance.

Oct 20, 2026
Detection & Defense · securityweek.com

US Agencies Outline Incident-Response Practices for Rogue AI Agents

NIST, NSA and CISA outline ten practices for preparing for and responding to AI-agent incidents, covering preparation, detection, response, recovery and reporting. The article describes the document as a clear checklist, not new guidance.

Oct 20, 2026
Detection & Defense · malwarebytes.com

How to Stop Android from Automatically Linking Your Phone Number to Google Accounts

Google’s default Android phone-number verification can associate a device’s number with signed-in Google accounts. The article explains how to disable automatic verification and review or remove the number and its other uses.

Oct 20, 2026
Detection & Defense · thehackernews.com

How Security Teams Can Govern Employee-Built AI Workflows

As employees build AI apps and workflows, the article recommends built-in governance: limit data access and actions, maintain controls in production, monitor activity, and establish ownership and response paths.

Oct 20, 2026
Detection & Defense · cofense.com

How Phishing Emails Abuse Device-Code Authentication

Cofense describes phishing emails that impersonate business invitations and familiar brands to trick victims into authorizing an attacker’s device-code sign-in, and outlines steps to take if an untrusted code is entered.

Oct 20, 2026
Detection & Defense · bleepingcomputer.com

CJIS v6.1: Five Security Priorities for Agencies

A sponsored guide outlines five CJIS v6.1 priorities for agencies: MFA, account management, passwords, logging, and audit readiness, with specific review timelines and compliance practices.

Oct 20, 2026
Detection & Defense · rapid7.com

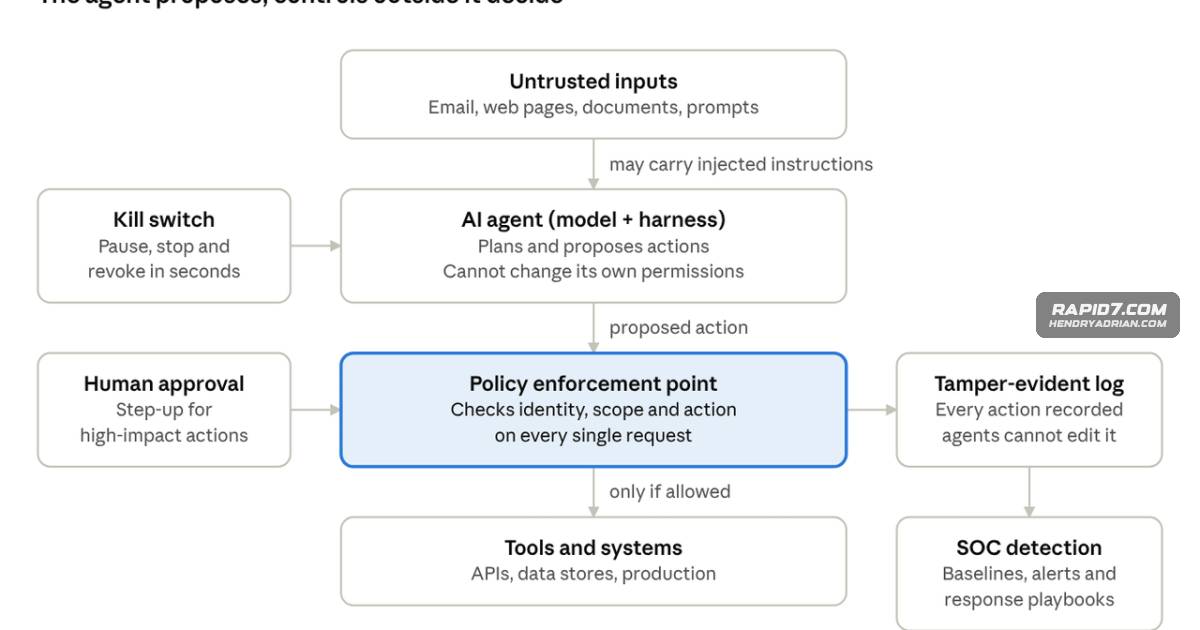
How Security Teams Can Defend AI Agents Against Insider-Style Risks

The article argues that AI agent controls should be enforced outside the model and offers SOC guidance on agent identities, least privilege, tamper-evident logs, testing, monitoring and response.

Oct 19, 2026
Detection & Defense · wiz.io

Wiz Describes Pipeline for Detecting Malicious npm Packages at Publication

Wiz says its pipeline analyzes new npm releases with static and dynamic analysis, sandboxed execution, and runtime monitoring to detect malicious packages before CVEs are published. It describes detecting keyv malware that retrieved C2 domains through an Ethereum smart

Oct 19, 2026
Detection & Defense · blog.cloudflare.com

Cloudflare Outlines Layered Defenses for NetScaler Gateways

Cloudflare recommends patching NetScaler gateways and layering access policies, WAF inspection, and origin restrictions to limit exposure to CVE-2026-88771 and CVE-2026-88772. It cautions that DTLS-enabled listeners need separate review.

Oct 19, 2026
Detection & Defense · hornetsecurity.com

Security Awareness Training Should Be Continuous, Role-Specific and Measurable

The article recommends continuous, role-specific security awareness training to help employees recognize social engineering, verify unusual requests and report concerns. It outlines practical program measures and promotes Hornetsecurity’s training service.

Oct 19, 2026
Detection & Defense · jamf.com

How to Secure Agentic AI When Prevention Fails

The final installment of Jamf’s agentic-AI security series recommends separating trusted instructions from retrieved content, monitoring agent decisions, planning recovery, limiting delegated authority and matching controls to an agent’s capabilities.

Oct 19, 2026
Detection & Defense · stepsecurity.io

OpenCode Says Breach Affected 1.4% of Console Users With Linked AI Providers

OpenCode says an ongoing breach affected 1.4% of Console users with linked Anthropic, OpenAI, or Google providers; the cause and accessed data remain undisclosed. StepSecurity advises inventorying installations, checking credentials, rotating keys, and reviewing usage.

Oct 18, 2026
Detection & Defense · cyble.com

AI Agents Lack MFA—Here Are the Security Controls They Need

The article describes reported AI-agent security incidents and recommends controls including scoped credentials, isolation of untrusted inputs, restricted package installs, automatic limits and tamper-resistant logging.

Oct 16, 2026
Detection & Defense · ic3.gov

FBI and CISA Warn Election Officials of Phishing and Smishing Threats Ahead of 2026 Midterms

The FBI and CISA warn that election and campaign officials may face phishing and smishing aimed at stealing credentials or sensitive data, including attacks using convincing AI-generated messages and deepfakes. They recommend phishing-resistant MFA and other security措施.

Oct 16, 2026
Detection & Defense · securityweek.com

Contextual Defense Connects Security Signals to Catch Attacks Earlier

The article argues that defenders should correlate identity, device, network, and threat signals to spot attack patterns early, then take proportionate action. It recommends reliable data, clear limits on automation, reversible actions, scalability, and outcome-based KP

Oct 15, 2026
Detection & Defense · decodedsecurity.com

Industry Analysis Finds Exploitation Can Precede Patch Disclosure by Seven Days on Average

The article says average time-to-exploit was estimated at seven days before public disclosure and cites Rapid7 finding 55% of known exploited zero-days in its dataset were exploited within a week of disclosure. It explains a risk-based patch-management lifecycle.

Oct 15, 2026
Detection & Defense · wazuh.com

Detecting REVSTEALER Activity and Automating File Removal With Wazuh

A Wazuh walkthrough demonstrates detecting REVSTEALER modules on Windows 11 using Sysmon, custom rules, and file integrity monitoring, with automated removal of files matching known malware hashes.

Oct 15, 2026
Detection & Defense · aws.amazon.com

How to Gate CI/CD Deployments with AWS Continuum Penetration Tests

AWS explains how to run scoped penetration tests after deployment and block production promotion based on findings, using OIDC authentication and CI/CD pipeline settings. It also warns about baseline advancement and fail-open defaults.

Oct 14, 2026
Detection & Defense · thehackernews.com

How to Run a Deepfake Readiness Drill to Test Verification Procedures

A practical guide to testing whether staff verify high-risk payment and access requests when faced with deepfake voice or video calls, using staged simulations, clear rules, measurement, and follow-up improvements.

Oct 14, 2026
PreviousPage 7 of 26 Next
© 2026 cyber.hendryadrian.com