cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

624 articles

Detection & Defense · elastic.co

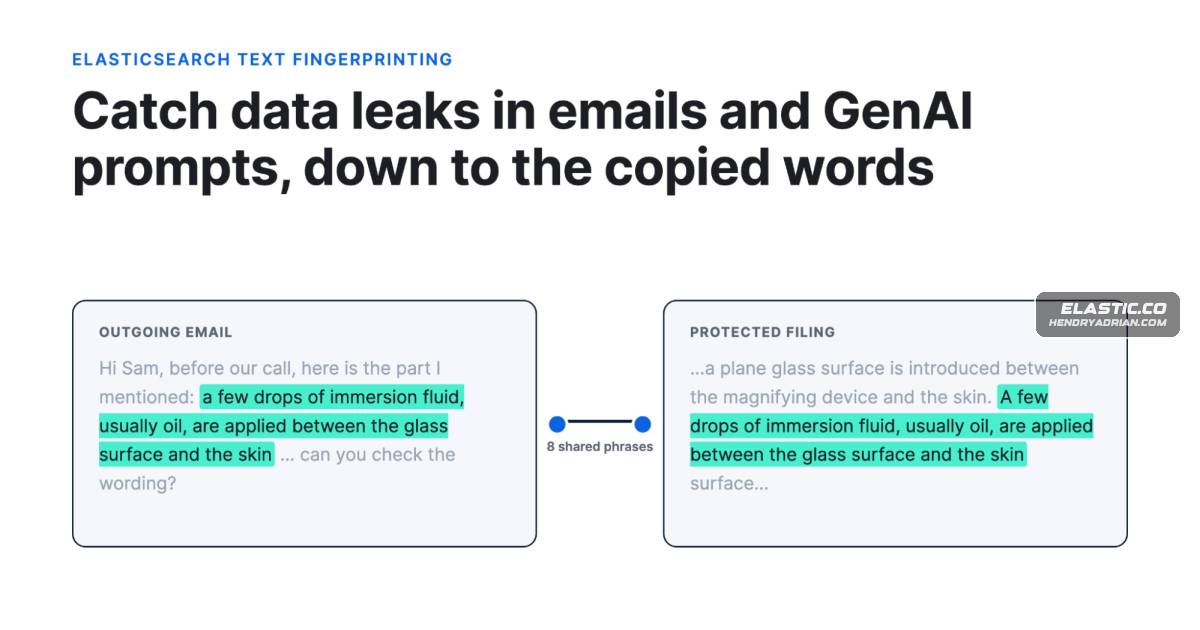
Using Elasticsearch Text Fingerprinting to Detect Copied Data in Emails and GenAI Prompts

The article shows how Elasticsearch can use overlapping text fingerprints to find and highlight copied passages in emails and GenAI prompts, with tuning guidance, test results, and limitations.
Nov 18, 2026
Detection & Defense · aws.amazon.com

AWS Details Two Secure Ingress Patterns for Bedrock AgentCore Runtime

AWS outlines API Gateway and AgentCore Gateway architectures for protecting AgentCore Runtime with identity validation, per-hop least privilege, session binding, network and edge controls, Guardrails, rate limiting, and audit logging.

Nov 17, 2026
Detection & Defense · blog.qualys.com

How to Secure Public AWS AMIs Against Look-Alike and Misconfigured Images

Public AWS AMIs can carry malware, exposed credentials, or outdated software; the whoAMI attack uses look-alike image names. Validate owner IDs, restrict trusted sources, scan images, and regularly rebuild Golden AMIs.

Nov 17, 2026
Detection & Defense · socprime.com

How to Detect and Defend Against Autonomous AI Cyberattacks

The article explains how AI agents could automate intrusion tasks, citing Anthropic's estimate that an agent handled 80–90% of tactical work in a state-sponsored campaign, and recommends behavior-based detection, identity monitoring and machine-speed defense.

Nov 17, 2026
Detection & Defense · socprime.com

SOC Prime Outlines Detection and Hunting for ARTEX and PHP2Shell

The article outlines behavior-based detection and mitigation for ARTEX, an LLM-driven pentesting framework reportedly used in attacks, and provides PHP2Shell hunting guidance for CVE-2026-109618 and CVE-2026-109619.

Nov 17, 2026
Detection & Defense · guardsix.com

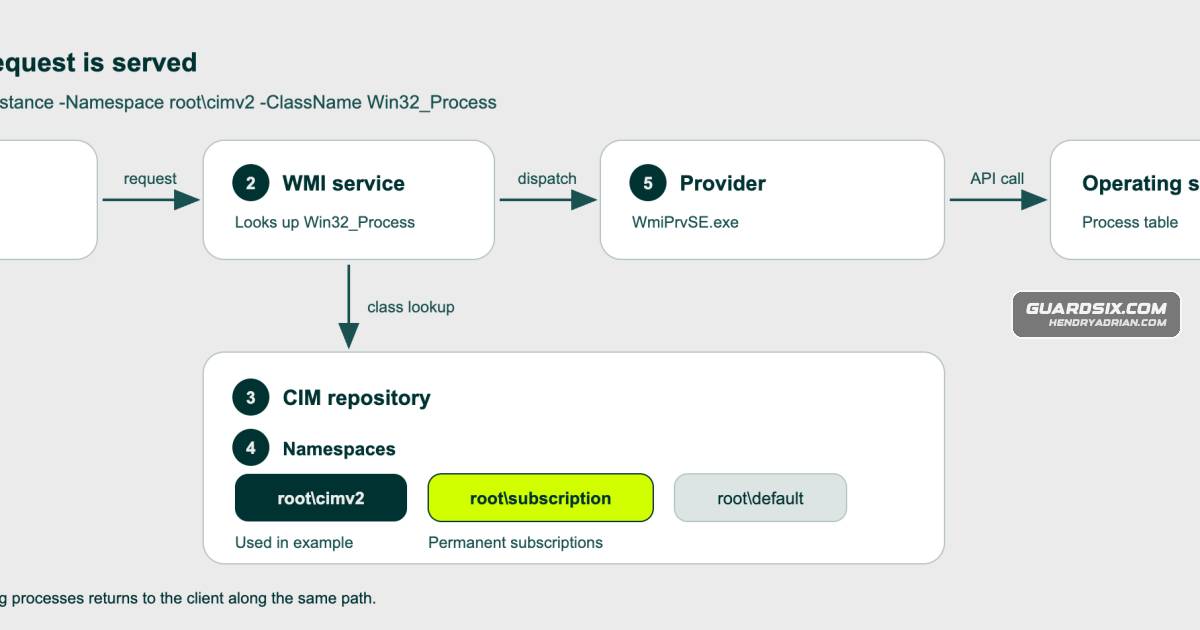
Detecting Persistence Through WMI Event Subscriptions

Explains how attackers abuse permanent Windows WMI event subscriptions for reboot-persistent execution and provides SIEM/Sysmon detections, relevant telemetry, and hardening advice.

Nov 17, 2026
Detection & Defense · bleepingcomputer.com

Huntress Details Phishing Kits That Steal Microsoft 365 Session Tokens

Huntress analyzed EvilTokens, Knight Office and Kali365, phishing kits that capture and replay Microsoft 365 session tokens. The sponsored article explains device-code and AiTM techniques and recommends ways to detect and contain session theft.

Nov 17, 2026
Detection & Defense · decodedsecurity.com

Microsoft 365 Outage Highlights Business Continuity Risks and Preparedness

The article reports a Microsoft 365 outage lasting about 24 hours across 74 countries, with a network change triggering a hidden bug and cascading server failures. It recommends continuity measures including backup communications, offline documents, assigned decision-pも

Nov 16, 2026
Detection & Defense · socradar.io

How to Choose a Secure DNS Resolver and Defend DNS Infrastructure

A 2026 guide compares public DNS resolvers by threat blocking, privacy, encryption and resilience, and explains protective DNS limits, enterprise logging, DNS hijacking defenses and risks from abandoned records and subdomain takeovers.

Nov 16, 2026
Detection & Defense · blog.qualys.com

ARTEX Speeds Up Attack Paths, Driving Calls for Faster Vulnerability Remediation

The article says ARTEX and similar AI pentest agents can chain existing weaknesses quickly; cited reports describe privileged access in under three hours. It urges complete asset inventories, exploitability validation, faster patching and controls on agent use.

Nov 16, 2026
Detection & Defense · databreachtoday.com

Utilities Need Fast, Controlled Remote Access to OT Systems

The article recommends framework-based OT remote access with approved, time-limited vendor sessions, named users, monitoring and safe shutdown. It cites attacks on water systems and warns that VPNs alone leave important access controls unaddressed.

Nov 16, 2026
Detection & Defense · bleepingcomputer.com

7 Tips for Meeting CJIS Password and MFA Requirements

A sponsored guide outlines CJIS password and MFA practices for law enforcement agencies, including blocking compromised passwords, resetting credentials when compromise is suspected, protecting stored and transmitted passwords, and extending MFA across accounts and log,

Nov 16, 2026
Detection & Defense · morphisec.com

AI Tools Leave Unmanaged Node.js Runtimes on Endpoints, Morphisec Warns

The article argues that AI tools add unmanaged Node.js runtimes and package-execution risks to endpoints, then outlines inventory, patching, access-control and monitoring measures. It reports no public evidence of attacks targeting agents through Node runtime bugs.

Nov 15, 2026
Detection & Defense · blog.cloudflare.com

Cloudflare Sees Surge in AI Pentesting Scans, Recommends Modern Security Model

Cloudflare reports 50+ AI pentesting frameworks scanning customers and a 30-fold rise in requests since Oct. 1. It says exposed CI/CD tokens enabled cross-environment access and recommends WAF, bot defense, identity gating, microsegmentation and schema validation.

Nov 13, 2026
Detection & Defense · blog.qualys.com

Qualys Outlines Risk-Based Patch Prioritization for November 2026

Qualys says Microsoft addressed 1,252 CVEs in November 2026 and rates about 35% of patches low reliability. It recommends prioritizing exposed assets, piloting high-impact updates, and using compensating controls when patches fail.

Nov 13, 2026
Detection & Defense · thehackernews.com

How to Contain an AI Agent When It Goes Wrong

Stopping an AI agent may not stop queued work, active sessions or valid credentials. The article outlines containment, investigation and recovery steps, including revoking access and verifying that controls work.

Nov 13, 2026
Detection & Defense · fieldeffect.com

Microsoft 365 Outage Fuels Credential Phishing and Fake Support Scams

Field Effect detected an outage-themed credential phishing email on November 13, 2026. The article describes related phishing and fake support scams, explains their risks, and recommends investigation, account cleanup and user-verification steps.

Nov 13, 2026
Detection & Defense · databreachtoday.com

Microsoft 365 Outage Highlights Healthcare Resilience Gaps

Microsoft said its 365 outage was not caused by malicious actors. Experts said healthcare organizations largely maintained patient care but faced communication and administrative disruption, highlighting the need for tested fallback channels and independent dependencies

Nov 13, 2026
Detection & Defense · bleepingcomputer.com

How One AI Agent Exposed Five Critical Enterprise Security Gaps

A sponsored, fictional AI-agent scenario illustrates security gaps in access, review, prompt-injection defenses, behavioral detection, and audit trails, alongside practical controls for addressing them.

Nov 13, 2026
Detection & Defense · cisecurity.org

CIS Urges UK Organizations to Strengthen Basic Cyber Hygiene

CIS recommends asset inventories, unique passwords, disabling unnecessary services, and consistent secure configurations to address common weaknesses, including as attackers adopt AI. It also describes tools for assessing and tracking progress.

Nov 12, 2026
Detection & Defense · privacyaffairs.com

Developer Reports Microsoft Defender Uploaded 217 Files, Including Unreleased Builds

Developer Garrett Stimpson says Defender logs showed 217 files uploaded in three months, including unreleased builds. The article explains how to check submission logs and settings, while noting that disabling uploads reduces some cloud protection.

Nov 12, 2026
Detection & Defense · elastic.co

How to Enforce Fine-Grained Authorization in Elasticsearch RAG with SpiceDB

A practical guide to using SpiceDB relationship-based access control in Elasticsearch RAG pipelines, with a deterministic authorization step that filters retrieved documents before they reach an LLM.

Nov 11, 2026
Detection & Defense · socprime.com

How to Export Snowflake Logs for Security Investigations

The guide explains how to export Snowflake audit logs as JSON or JSONL, check login history for suspicious activity, and follow sessions into query history. It also covers access, latency, and export troubleshooting.

Nov 11, 2026
Detection & Defense · socprime.com

How to Export Databricks Audit Logs for Security Review

A tutorial shows how to export Databricks audit logs with Spark SQL, save them as JSON in a Unity Catalog volume, and download them with the Databricks CLI. It also highlights activity to investigate and troubleshooting tips.

Nov 11, 2026
Page 1 of 26 Next
© 2026 cyber.hendryadrian.com