
UNC6671 Uses Vishing to Steal SaaS Credentials and Extort Victims
Summary
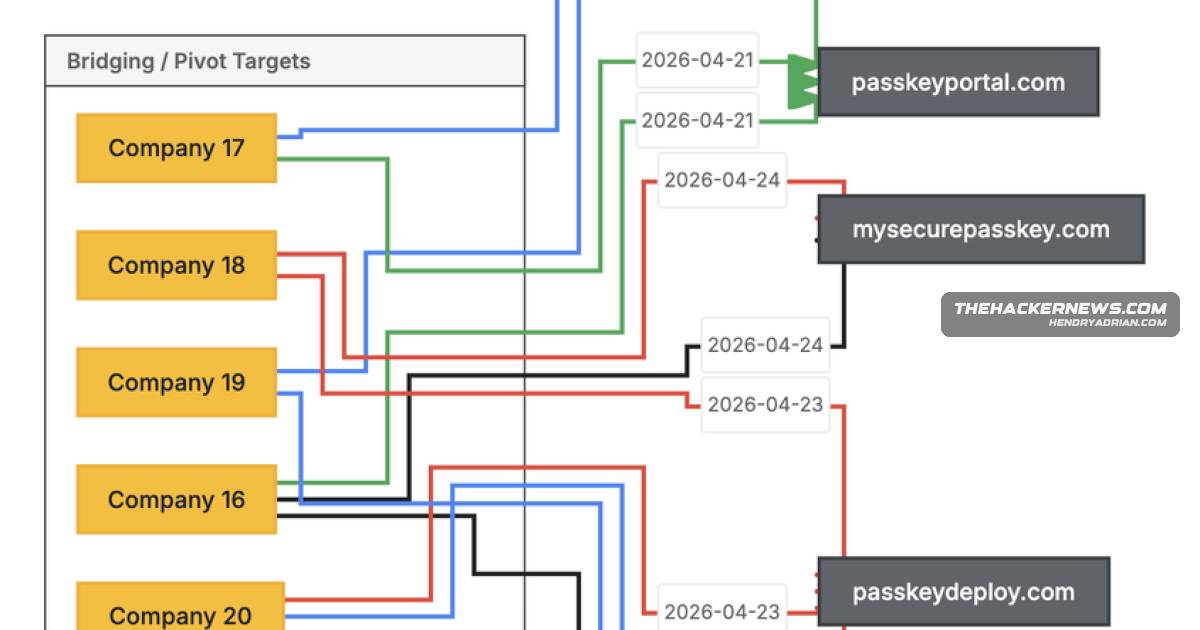
Google and Mandiant say UNC6671 uses vishing and adversary-in-the-middle phishing to steal credentials and sessions, access SaaS services, and extort victims under multiple brands. The report details targets, payment estimates and defenses.
Key points
- Google and Mandiant attribute vishing-led extortion campaigns targeting financial services, private equity and professional services to UNC6671.
- The group impersonates IT help desk staff, often calling employees' personal phones and directing them to fake adversary-in-the-middle login pages to capture credentials, MFA tokens and sessions.
- The actors use captured access to reach SaaS environments including Microsoft 365 and Okta; reported tactics include registering actor-controlled MFA devices and using scripts to exfiltrate cloud data.
- UNC6671 has operated under multiple extortion brands, including Redact, Pink, Helix, Falcon and the now-retired BlackFile.
- Google says it tracked more than $10.6 million in Bitcoin payments to associated wallets from January 7 to May 12, 2026; it reported that over 53% of tracked cases settled for an average of $750,000.
- Recommended defenses include phishing-resistant MFA, session controls, restricting access to trusted networks and managed devices, and monitoring identity-provider logs for suspicious MFA registrations.
- In a separate incident documented by Bridewell, existing controls blocked a suspected fraudulent Okta login attempt before credentials were entered; attribution was uncertain.
Article Details
- Event Type
- Vishing-led credential theft and data extortion campaign targeting enterprise SaaS environments.
- Impact
- UNC6671 is reported to steal credentials, MFA tokens, and active session data through fraudulent login portals, then access SaaS environments and exfiltrate cloud data for extortion. Google reported tracking more than $10.6 million in Bitcoin payments associated with the group between January 7 and May 12, 2026; tracked cases reportedly averaged $750,000 in settlements.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | idokta[.]com | Listed as an example of a domain hosting a credential-harvesting panel used in the campaign’s targeted vishing activity. |
| DOMAIN | passkeyhelpdesk[.]com | Listed as an example of a domain hosting a credential-harvesting panel used in the campaign’s targeted vishing activity. |
| DOMAIN | setupsso[.]com | Listed as an example of a domain hosting a credential-harvesting panel used in the campaign’s targeted vishing activity. |
MITRE ATT&CK
T1056.003 · Web Portal CaptureFake login portals capture credentials and MFA tokens.T1070.008 · Clear Mailbox DataOperators reportedly delete password-reset confirmations and security alerts from compromised email accounts.T1078 · Valid AccountsCaptured credentials and sessions are used to access identity providers and connected SaaS applications.T1098.005 · Device RegistrationOperators establish persistence by registering attacker-controlled MFA devices to compromised accounts.T1539 · Steal Web Session CookieOperators capture active session data and tokens for access to SaaS environments.T1557 · Adversary-in-the-MiddleAdversary-in-the-middle infrastructure intercepts credentials, MFA tokens, and session data.T1566.004 · Spearphishing VoiceOperators use voice phishing calls while impersonating IT help desk staff.
People
Threat Actors
Bling LibraIdentified in the article as an alternate name for ShinyHunters, a financially motivated hacking group whose tradecraft is associated with UNC6671.Cordial SpiderName CrowdStrike uses for the umbrella collective it characterizes as conducting rapid data-theft and extortion campaigns through vishing and fraudulent AitM pages.Scattered Lapsus$ HuntersMentioned as a possible actor behind a separate unsuccessful vishing campaign, or as a group whose tradecraft is consistent with shared phishing-kit infrastructure; attribution is uncertain.ShinyHuntersDescribed as a financially motivated hacking group whose tradecraft is associated with UNC6671; Google assesses that UNC6671’s operations act independently.UNC6671Google attributes vishing-led credential theft, SaaS access, cloud-data exfiltration, and extortion activity to this threat cluster.
Vendors
MicrosoftThe group uses captured sessions to access Microsoft 365 and Okta, exfiltrate cloud data, and operate under multiple extortion brands including Redact, Pink, Helix, Falcon, and BlackFile.OktaThe group uses captured sessions to access Microsoft 365 and Okta, exfiltrate cloud data, and operate under multiple extortion brands including Redact, Pink, Helix, Falcon, and BlackFile.
Products
Microsoft 365 Apps for EnterpriseThe group uses captured sessions to access Microsoft 365 and Okta, exfiltrate cloud data, and operate under multiple extortion brands including Redact, Pink, Helix, Falcon, and BlackFile.Microsoft Entra IDin June 2026, SOCRadar described the group as focused on Big Game Hunting using tailored Okta and Microsoft Entra ID phishing kits, access gates to block sandboxes and researchers, and Cloudflare and DDoS-Guard forOktaThe group uses captured sessions to access Microsoft 365 and Okta, exfiltrate cloud data, and operate under multiple extortion brands including Redact, Pink, Helix, Falcon, and BlackFile.
Countries
AustraliaThe threat actor is known for maintaining a high operational cadence, targeting dozens of organizations in North America, Australia, and the U.K.United KingdomThe threat actor is known for maintaining a high operational cadence, targeting dozens of organizations in North America, Australia, and the U.K.
Industries
Financial ServicesUNC6671 is carrying out vishing-led extortion campaigns against financial services, private equity, and professional services by impersonating IT help desk staff and stealing credentials through fake login portals.Healthcarein the threat actor’s targeting footprint: from large enterprises in the manufacturing, real estate, healthcare, and insurance sectors during April and May 2026, to technology, transportation, and hospitality firmsHospitalityhealthcare, and insurance sectors during April and May 2026, to technology, transportation, and hospitality firms in June 2026, and then to high-value financial and legal organizations in July 2026.Insuranceactor’s targeting footprint: from large enterprises in the manufacturing, real estate, healthcare, and insurance sectors during April and May 2026, to technology, transportation, and hospitality firms in June 2026,Legalto technology, transportation, and hospitality firms in June 2026, and then to high-value financial and legal organizations in July 2026.Manufacturingnew techniques is a shift in the threat actor’s targeting footprint: from large enterprises in the manufacturing, real estate, healthcare, and insurance sectors during April and May 2026, to technology,Private equityUNC6671 is carrying out vishing-led extortion campaigns against financial services, private equity, and professional services by impersonating IT help desk staff and stealing credentials through fake login portals.Professional ServicesUNC6671 is carrying out vishing-led extortion campaigns against financial services, private equity, and professional services by impersonating IT help desk staff and stealing credentials through fake login portals.real estateis a shift in the threat actor’s targeting footprint: from large enterprises in the manufacturing, real estate, healthcare, and insurance sectors during April and May 2026, to technology, transportation, andTechnologyin the manufacturing, real estate, healthcare, and insurance sectors during April and May 2026, to technology, transportation, and hospitality firms in June 2026, and then to high-value financial and legalTransportationreal estate, healthcare, and insurance sectors during April and May 2026, to technology, transportation, and hospitality firms in June 2026, and then to high-value financial and legal organizations in July