
Ransom Busters Claims Access to Ransomware Servers, Demands Up to $60,000
Summary
GuidePoint says Ransom Busters has contacted ransomware victims claiming access to RaaS servers and offering to delete stolen data for $20,000–$60,000. The article also details UNC6671 extortion activity and a more fragmented ransomware ecosystem.
Key points
- GuidePoint reports that Ransom Busters contacts victims and claims it can delete their data from ransomware servers for $20,000–$60,000; the group’s access and promises are unverified.
- In two incidents, investigators found overlaps including SoftPerfect Network Scanner, s5cmd, an RMM tool installed through PowerShell, a shared backdoor password, and the same attacker-controlled hostname. GuidePoint says this may indicate a single operator.
- GuidePoint believes Ransom Busters is likely an affiliate operating across multiple RaaS operations and observed its activity in incidents involving DragonForce, Settra, and Anubis.
- GuidePoint describes UNC6671’s AitM and phishing activity across 76 organizations, with 78 targeted phishing subdomains and extortion brands including Falcon, Helix, Pink, Redact, and BlackFile.
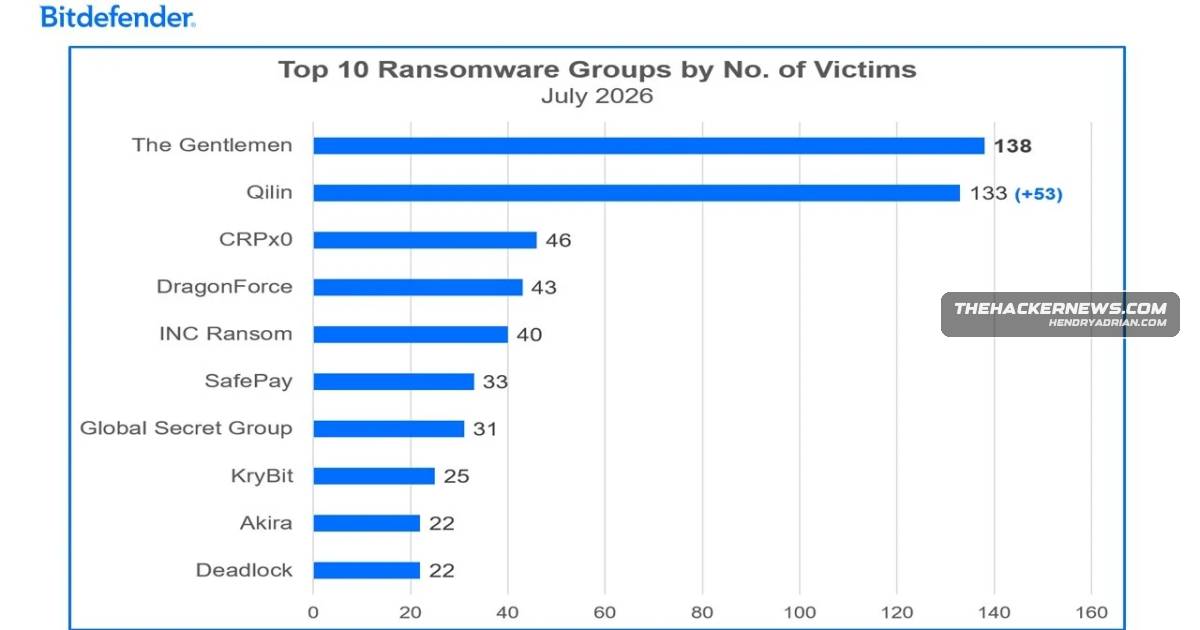
- Check Point’s Q2 2026 report recorded 2,139 organizations on ransomware leak sites; the number of active groups rose from 71 to 93 as the top 10 groups’ share fell from 71% to 57.6%.
- Huntress reported that an Akira affiliate’s Safe Mode attempt disabled security tools but also prevented ransomware execution; credentials and file shares had reportedly already been exfiltrated.
Article Details
- Event Type
- Disclosure of a deceptive ransomware-affiliate extortion scheme and a separate UNC6671 credential-phishing campaign.
- Impact
- Ransom Busters contacted victims and demanded $20,000–$60,000, claiming it could delete stolen data held by ransomware groups; GuidePoint described the claimed access and deletion offer as untrustworthy. Separately, GuidePoint reported that UNC6671's extortion brands were linked to more than $8 million in payments across 15 Bitcoin wallets, and identified 78 phishing subdomains targeting 76 organizations.
MITRE ATT&CK
T1046 · Network Service DiscoverySoftPerfect Network Scanner was used for internal reconnaissance.T1059.001 · PowerShellA PowerShell script was used to install the Remotely RMM tool.T1136.001 · Local AccountThe intrusions involved creating a local backdoor account.T1557 · Adversary-in-the-MiddleGuidePoint described UNC6671 conducting adversary-in-the-middle operations involving real-time credential relay.T1562.001 · Disable or Modify ToolsAn Akira affiliate reportedly rebooted a victim host into Safe Mode with Networking to take security tools offline.T1562.009 · Safe Mode BootAn Akira affiliate reportedly rebooted a victim host into Safe Mode with Networking as a defense-evasion measure.T1566.002 · Spearphishing LinkThe article reports phishing subdomains and phishing templates used to target organizations and impersonate identity providers.T1567.002 · Exfiltration to Cloud Storages5cmd was used to exfiltrate data to cloud storage via AWS.
People
James NortheyA security researcher who discussed an Akira incident in which the attacker’s Safe Mode defense-evasion attempt reportedly prevented the ransomware from deploying.Justin TimothyA Principal Consultant at GuidePoint Research and Intelligence Team who commented on Ransom Busters' claimed access and the apparent legality of its activity.Rakesh KrishnanA security researcher who assessed the technical characteristics of the Majinahanashi ransomware family.
Threat Actors
AkiraA ransomware group whose affiliate reportedly rebooted a victim host into Safe Mode to take security tools offline; the ransomware did not deploy in that incident, but credentials and file shares had already been exfiltrated.AnubisA threat group involved in incidents GuidePoint said it had responded to; those incidents were cited in connection with Ransom Busters' activity.Cordial SpiderAn explicitly stated alternate name for UNC6671, which GuidePoint reported conducting AitM and extortion operations.CRPx0A ransomware group reported to offer white-label ransomware operations and hacking-as-a-service, and to use fake CAPTCHA lures and a clipper payload.DragonForceA ransomware group involved in incidents GuidePoint said it had responded to; those incidents were cited in connection with Ransom Busters' activity.O-UNC-045An explicitly stated alternate name for UNC6671, which GuidePoint reported conducting AitM and extortion operations.Ransom BustersA ransomware affiliate persona that GuidePoint reported contacting victims, claiming access to ransomware-group servers, and demanding payment to delete stolen data. GuidePoint considers the offer deceptive and the activity likely unlawful.SettraA threat group involved in incidents GuidePoint said it had responded to; those incidents were cited in connection with Ransom Busters' activity.Shiny HuntersNamed as a group whose SaaS-centric targeting resembles the targeting attributed to UNC6671.Silent RansomA ransomware group reported by Coveware to be conducting a campaign against high-profile law firms; the source explicitly identifies Luna Moth as an alternate name.Silent Ransom GroupAn explicitly stated alternate name for Silent Ransom, which Coveware linked to a campaign against high-profile law firms.UNC6671GuidePoint reported that this tracked group conducted sustained AitM and extortion operations targeting organizations through multiple extortion brands.
Malware
Products
Microsoft 365 Apps for Enterpriserelay management using phishing templates that impersonate identity providers like Okta and Microsoft 365.OktaAs recently detailed by Okta, UNC6671 operates a custom console called Work Panel that enables role-based access control, integrated target reconnaissance via commercial B2B data APIs, automated infrastructureSonicWall VPNSafe Mode with Networking to knock security tools offline after obtaining initial access through a SonicWall VPN.
Tools
RemotelyRemotely remote monitoring and management (RMM) tool, which is installed through a PowerShell scripts5cmdIts activity overlaps with DragonForce, Settra, and Anubis incidents, using tools like SoftPerfect Network Scanner and s5cmd.SoftPerfect Network ScannerIts activity overlaps with DragonForce, Settra, and Anubis incidents, using tools like SoftPerfect Network Scanner and s5cmd.Work PanelAs recently detailed by Okta, UNC6671 operates a custom console called Work Panel that enables role-based access control, integrated target reconnaissance via commercial B2B data APIs, automated infrastructure
Countries
Bulgariaand Turkey, Majinahanashi has mostly targeted Switzerland, Italy, Germany, Bulgaria, and India.Germanyand Turkey, Majinahanashi has mostly targeted Switzerland, Italy, Germany, Bulgaria, and India.Indiaand Turkey, Majinahanashi has mostly targeted Switzerland, Italy, Germany, Bulgaria, and India.Italyand Turkey, Majinahanashi has mostly targeted Switzerland, Italy, Germany, Bulgaria, and India.Switzerlandand Turkey, Majinahanashi has mostly targeted Switzerland, Italy, Germany, Bulgaria, and India.Turkeyand Turkey, Majinahanashi has mostly targeted Switzerland, Italy, Germany, Bulgaria, and India.
Industries
Financial Services(AitM) operation orchestrated by UNC6671 (aka Cordial Spider and O-UNC-045) targeting financial services, legal, and other industries since April under various extortion brands, such as Falcon, Helix,Legal(AitM) operation orchestrated by UNC6671 (aka Cordial Spider and O-UNC-045) targeting financial services, legal, and other industries since April under various extortion brands, such as Falcon, Helix, Pink, Redact, and