Microsoft Details Passkey Phishing and Million-Email Payment Scam Campaigns
Summary
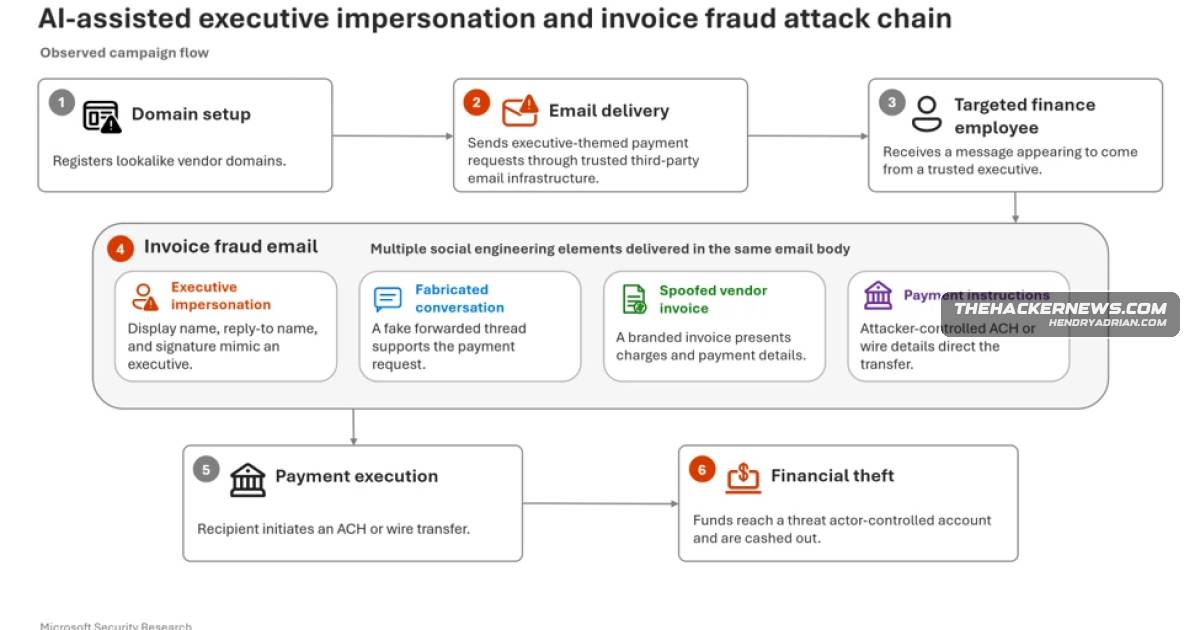
Microsoft disclosed two campaigns: one sent over a million executive-impersonation payment scam emails, while another used passkey-themed lures to compromise cloud accounts, establish MFA persistence, and collect data from Microsoft services.
Key points
- One campaign sent over a million fake CEO payment requests between August 3 and 5, 2026, seeking fraudulent ACH transfers for a supposed ServiceNow subscription.
- The payment scam used AI-generated, tailored messages, forged invoices, fake email threads, and impersonation domains.
- A separate campaign, detected since May 2026, used calls or messages posing as IT support to direct employees to counterfeit Microsoft sign-in pages.
- Lures sought to capture credentials or induce victims to approve adversary-in-the-middle or device-code authentication flows.
- After gaining access, actors registered their own MFA methods to maintain access, then used Microsoft Graph to enumerate accounts and resources and collect mailbox, SharePoint, and OneDrive data.
- Microsoft associated initial access activity with Storm-3121 and Storm-3032; the article says connections among related groups and extortion brands remain unclear.
- Microsoft said Graph activity should be assessed across behavioral sequences and correlated events, rather than judged by individual API calls.
Article Details
- Event Type
- Two cybercrime campaigns involving executive impersonation for fraudulent ACH payments and passkey-themed phishing to compromise cloud accounts.
- Impact
- The campaigns exposed organizations to fraudulent payment requests and unauthorized cloud-account access. After gaining access, attackers added their own MFA methods, conducted reconnaissance, collected mailbox data, and downloaded files from SharePoint and OneDrive for exfiltration. Microsoft reported more than one million scam emails sent between August 3 and 5, 2026; the cloud activity had been detected since May 2026.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | add-passkey[.]com | Domain registered for passkey-themed social engineering and counterfeit sign-in lures. |
| DOMAIN | domainlify[.]net | Bogus domain listed by Microsoft in connection with the financial fraud campaign. |
| DOMAIN | integratedsso[.]com | Domain registered for SSO-themed social engineering and counterfeit sign-in lures. |
| DOMAIN | oktasession[.]com | Domain registered for identity-themed social engineering and counterfeit sign-in lures. |
| DOMAIN | passkeyhelpdesk[.]com | Domain registered for passkey-themed social engineering and counterfeit sign-in lures. |
| DOMAIN | portalsetuphub[.]com | Domain registered for account-setup-themed social engineering and counterfeit sign-in lures. |
| DOMAIN | secure-passkey[.]com | Domain registered for passkey-themed social engineering and counterfeit sign-in lures. |
| DOMAIN | service-nowinc[.]com | Impersonation domain used in the fake ServiceNow subscription payment scam. |
| DOMAIN | setupmypasskey[.]com | Domain registered for passkey-themed social engineering and counterfeit sign-in lures. |
| DOMAIN | syncmykey[.]com | Domain registered for passkey-themed social engineering and counterfeit sign-in lures. |
MITRE ATT&CK
T1078.004 · Cloud AccountsThe intrusions used compromised cloud identities to access accounts and applications.T1098.005 · Device RegistrationAfter initial access, attackers registered phone, authenticator-app, or software OTP authentication methods under their control.T1114 · Email CollectionAttackers enumerated and collected mailbox messages, folders, and attachment metadata.T1530 · Data from Cloud StorageAttackers accessed and downloaded data from SharePoint and OneDrive.T1557 · Adversary-in-the-MiddleThe article describes adversary-in-the-middle authentication flows used to take control of Microsoft accounts.T1566.004 · Spearphishing VoiceThe attackers used phone calls or messages impersonating IT help desks to direct users to phishing flows.
Threat Actors
BlackFileThe article says UNC6671 actors broke off from BlackFile, also identified as CL-CRI-1116.Cordial SpiderOne of the names used by the article for the cybercrime collective associated with overlapping phishing infrastructure and targeting.FalconThe article says Storm-3121 activity can lead to Falcon extortion and identifies Falcon as also known as CL-CRI-1182.HelixThe article says actors who broke off from BlackFile now operate under the Helix extortion brand.O-UNC-045One of the names used by the article for the cybercrime collective associated with overlapping phishing infrastructure and targeting.PREY-0058One of the names used by the article for the cybercrime collective associated with overlapping phishing infrastructure and targeting.ShinyHuntersThe article says Storm-3121 activity can lead to ShinyHunters extortion.Storm-3121Microsoft attributed initial-access activity in the passkey-themed campaign to Storm-3121; the article says its activity can lead to ShinyHunters and Falcon extortion.UNC6671A tracked group associated with passkey-themed phishing; the article says Storm-3032 is Microsoft’s designation for UNC6671.
Vendors
Products
Microsoft Exchange OnlineConduct high-volume access and download activity aimed at SharePoint Online and OneDrive for Business, and even Microsoft Exchange Online in some cases.Microsoft Graphactivity involved bogus domains, counterfeit Microsoft sign-in pages, MFA persistence, and extensive Microsoft Graph, SharePoint, OneDrive, and mailbox abuse tied to groups including Storm-3121, Storm-3032, UNC6671,Microsoft Office Homeinvestigated by Microsoft, the threat actors are said to have carried out an anomalous sign-in to Microsoft Office Home from an unmanaged device to expand their access to other applications like SharePoint Online andMicrosoft OneDrivecounterfeit Microsoft sign-in pages, MFA persistence, and extensive Microsoft Graph, SharePoint, OneDrive, and mailbox abuse tied to groups including Storm-3121, Storm-3032, UNC6671, Cordial Spider, O-UNC-045,Microsoft SharePointbogus domains, counterfeit Microsoft sign-in pages, MFA persistence, and extensive Microsoft Graph, SharePoint, OneDrive, and mailbox abuse tied to groups including Storm-3121, Storm-3032, UNC6671, Cordial Spider,Microsoft Teams“In a smaller number of cases, actors take advantage of already compromised accounts to expand their reach” by sending similar passkey-themed messages via Microsoft Teams.
Industries
consumer goodsThe activity primarily singled out enterprise users in the U.S., spanning IT services, consumer goods, real estate, and discrete manufacturing sectors.discrete manufacturingThe activity primarily singled out enterprise users in the U.S., spanning IT services, consumer goods, real estate, and discrete manufacturing sectors.IT servicesThe activity primarily singled out enterprise users in the U.S., spanning IT services, consumer goods, real estate, and discrete manufacturing sectors.real estateThe activity primarily singled out enterprise users in the U.S., spanning IT services, consumer goods, real estate, and discrete manufacturing sectors.