
Fake Software Sites Deliver Malware That Disables Windows Update and Weakens Defender
Summary
Microsoft reports a Silver Fox-linked campaign using fake software sites to deliver malware that weakens defenses and disables Windows Update. The campaign targets Chinese-speaking users and China-based operations; Microsoft says Defender initiated containment.
Key points
- Fake, high-fidelity vendor download sites use Chinese-language lures to distribute malicious installers, with victims across multiple sectors.
- Microsoft assesses with moderate confidence that the campaign is linked to Silver Fox, also known as Yinhu.
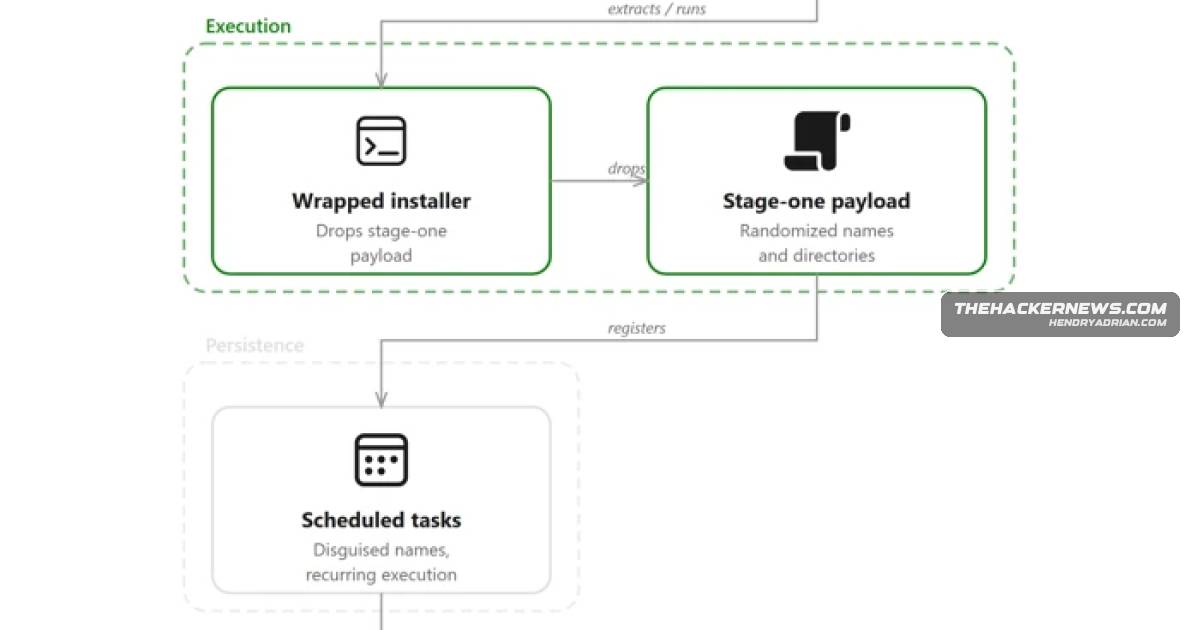
- The installers establish persistence with scheduled tasks and use PowerShell to configure Microsoft Defender exclusions, delete shadow copies, and restrict access to payload directories.
- The malware tampers with Windows Update by disabling related services, renaming update DLLs, and deleting the SoftwareDistribution cache.
- Microsoft observed command-and-control traffic over non-standard ports and identified iualef[.]net and oijfwe[.]net as associated domains.
- Microsoft says Defender detected the activity and initiated automated containment; the campaign’s end goal remains unclear.
- Separately, Kaspersky reported a QN Wallpaper installer used for DLL sideloading to deliver ValleyRAT, which can capture keystrokes and clipboard contents.
Article Details
- Event Type
- Malware campaign distributing malicious installers through counterfeit software-download websites, with related reporting on ValleyRAT delivery through DLL sideloading.
- Impact
- Victims across multiple organizations and industries, primarily China-based operations of multinational organizations and Chinese-speaking users. The malware establishes persistence, weakens Microsoft Defender and Windows Update protections, and communicates with attacker-controlled infrastructure. Microsoft reported automated containment; the campaign's ultimate goal is unclear.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | app-microsoft-edge[.]com[.]cn | Counterfeit software-download website used to impersonate a trusted vendor and distribute malicious installers. |
| DOMAIN | baidu-pan[.]com[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | calibre-ebook[.]com[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | cn-drawio[.]com[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | gehie246[.]com | Domain serving the ZIP archive downloaded from counterfeit software sites. |
| DOMAIN | gw-sogou[.]com[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | iualef[.]net | C2 domain associated with the malware campaign. |
| DOMAIN | kaspersky-lab[.]hl[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | mindmoster[.]com[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | ocam-pc[.]com[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | oijfwe[.]net | C2 domain associated with the malware campaign. |
| DOMAIN | pc-razerzone[.]com[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | sejda[.]hl[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | steelseries-cn[.]com[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | translate-youdao[.]hl[.]cn | Counterfeit software-download website used to distribute malicious installers. |
| DOMAIN | zh-diskgenius[.]com[.]cn | Counterfeit software-download website used to distribute malicious installers. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelValleyRAT sends keylogger logs and clipboard data to C2.T1056.001 · KeyloggingThe backdoor captures keystrokes.T1059.001 · PowerShellPowerShell is used to configure Microsoft Defender exclusions.T1105 · Ingress Tool TransferValleyRAT can download additional DLL or shellcode modules.T1115 · Clipboard DataThe backdoor captures clipboard contents.T1574.002 · DLL Side-LoadingRelated ValleyRAT reporting describes DLL sideloading to run malicious code under the guise of a signed process.
People
Threat Actors
CuboidalCanineA subgroup within GoldenEyeDog, according to an Expel report; attributed use of ValleyRAT and reported targeting of the gambling industry.GoldenEyeDogThe article says ValleyRAT has been known to be used by this group.Silver FoxMicrosoft assessed with moderate confidence that the campaign was consistent with this Chinese threat cluster; the article identifies Yinhu as an alternative name.
Malware
Gh0st RATSilver Fox (aka Yinhu), which has a track record of using spoofed vendor download pages to distribute Gh0st RAT and ValleyRAT (aka WinOS 4.0).QN Wallpapera malicious installer that deploys a modified Chinese desktop wallpaper management tool known as QN Wallpaper, while using it to initiate a DLL sideloading chain responsible for delivering ValleyRAT.ValleyRATThe activity is linked with moderate confidence to Silver Fox (Yinhu), and related reporting also ties ValleyRAT delivery to malicious installers and DLL sideloading techniques.
Vendors
Products
Microsoft Defender Antimalware Platformis also responsible for creating a short-lived scheduled task that runs as SYSTEM and configures Microsoft Defender exclusions via PowerShell, deletes volume shadow copies, and ensures payload directories cannot beQN Wallpapera malicious installer that deploys a modified Chinese desktop wallpaper management tool known as QN Wallpaper, while using it to initiate a DLL sideloading chain responsible for delivering ValleyRAT.Windows UpdateIn addition, it tampers with Windows Update by stopping and disabling wuauserv, UsoSvc, uhssvc, and WaaSMedicSvc, renaming update dynamic-link libraries (DLLs), and deleting the SoftwareDistribution cache.
Tools
Countries
Industries
EducationThe activity has resulted in victims spanning healthcare, manufacturing, gaming, technology, logistics, government, and education sectors.Gamblingmoved away from Gh0st RAT “at some point.” CuboidalCanine, per the cybersecurity company, targets the gambling industry and uses watering holes to distribute the malware by abusing code-signing certificates toGamingThe activity has resulted in victims spanning healthcare, manufacturing, gaming, technology, logistics, government, and education sectors.GovernmentThe activity has resulted in victims spanning healthcare, manufacturing, gaming, technology, logistics, government, and education sectors.HealthcareThe activity has resulted in victims spanning healthcare, manufacturing, gaming, technology, logistics, government, and education sectors.logisticsThe activity has resulted in victims spanning healthcare, manufacturing, gaming, technology, logistics, government, and education sectors.ManufacturingThe activity has resulted in victims spanning healthcare, manufacturing, gaming, technology, logistics, government, and education sectors.TechnologyThe activity has resulted in victims spanning healthcare, manufacturing, gaming, technology, logistics, government, and education sectors.