
Elastic Details REVSTEALER Stealer and Four Companion Modules That Persist After It Deletes Itself
Summary
Elastic Security Labs documented REVSTEALER and four associated Windows programs, including one that disables updates and Defender before running a miner. The report details their capabilities, delivery, technical links, and response steps.
Key points
- REVSTEALER steals credentials, cookies, wallet and messaging data, then deletes itself; Elastic says it did not observe the four associated programs being delivered to a live REVSTEALER host.
- The four programs—ProManager, WinUpdate, SoftManager, and LockAppHost—are separate executables that install in the user profile and can remain after the stealer exits.
- ProManager targets cryptocurrency wallets with overlay content and captures passwords or passphrases; WinUpdate replaces copied wallet addresses and collects text resembling recovery phrases.
- SoftManager routes attacker network traffic through victims’ connections. LockAppHost disables Windows Update and adds Microsoft Defender exclusions before running a cryptocurrency miner with administrator rights.
- Elastic linked the programs to REVSTEALER through shared build tradecraft and investigative context, not an observed hand-off to infected hosts.
- Elastic traced distribution to game-cheat lures and pirated or impersonated software. A detection rule matched about 4,700 VirusTotal samples, which the article says is a file count, not confirmed infections.
- Elastic published YARA and behavior rules and indicators. Its response guidance includes restoring disabled update settings and Defender exclusions, checking for hidden miners, and changing passwords and ending active sessions.
Article Details
- Attack Vectors
- REVSTEALER is distributed through game-cheat lures and pirated or impersonated software, including a fake “Claude Opus 5 Free Desktop” application.
- ProManager overlays attacker-controlled content on desktop cryptocurrency wallet windows and records passwords or passphrases entered or pasted into identified fields.
- WinUpdate monitors the clipboard, replaces copied cryptocurrency addresses with attacker-controlled addresses, and collects text resembling wallet recovery phrases.
- SoftManager routes attacker network traffic through the infected machine as a reverse proxy.
- LockAppHost abuses the Windows CMSTP tool to seek administrator rights, disables Windows Update and adds Microsoft Defender exclusions, then runs a cryptocurrency miner.
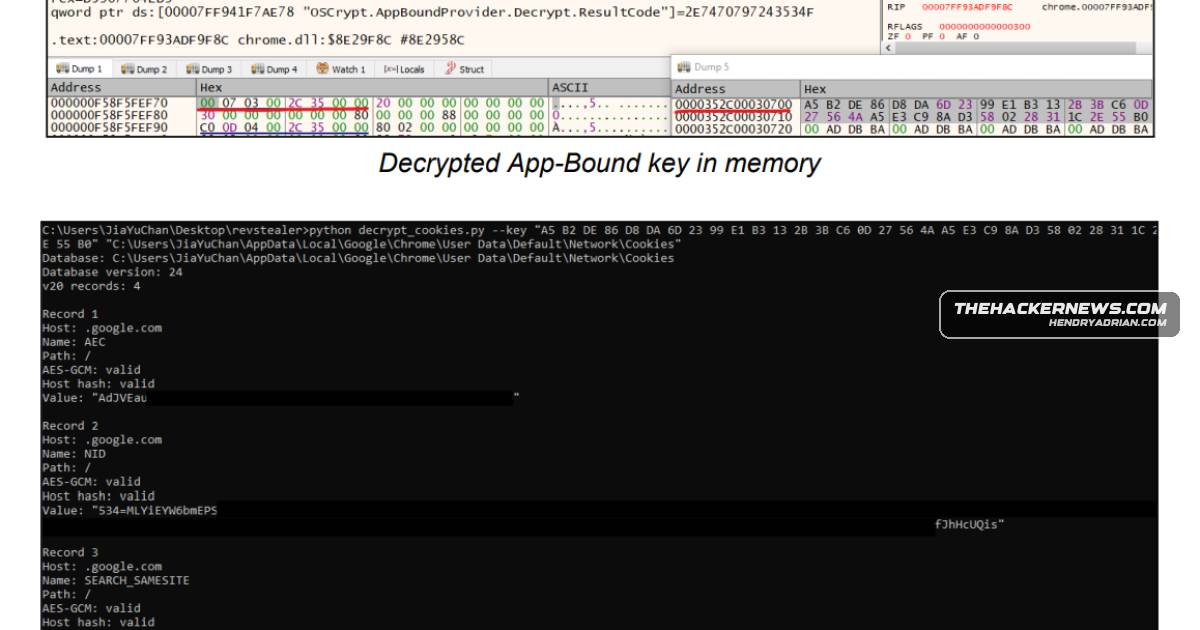
- REVSTEALER extracts browser passwords, cookies, wallet data, messaging data, gaming sessions, VPN and FTP configuration, and selected files; it can read Chrome’s App-Bound Encryption key from browser memory.
- Defensive Notes
- Avoid unofficial versions of paid AI tools and game cheats; obtain Claude only from Anthropic’s official channels.
- Use Elastic’s published YARA and behavior rules and indicators for detection and blocking; the public YARA file does not cover LockAppHost.
- After a LockAppHost infection, re-enable the Windows Update services and scheduled tasks it disabled, remove the Microsoft Defender exclusions it added, and check for a miner hidden in a suspended instance of nslookup.exe or svchost.exe.
- Because REVSTEALER steals session cookies and Chrome’s App-Bound Encryption key, affected users should change passwords and end active account sessions.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | config[.]hubdisplay[.]lol | ProManager command-and-control domain. |
| DOMAIN | health[.]journal-metric[.]lol | WinUpdate command-and-control domain. |
| DOMAIN | metric[.]gardenpark[.]click | SoftManager command-and-control domain. |
| DOMAIN | monitor5[.]roast-core85[.]click | REVSTEALER command-and-control domain. |
| SHA256 | 13d7237d7289e67c2d806a65d52580b453ce4987acbe2c4c4d04833f55ebccfa | SHA-256 hash identified for the ProManager module. |
| SHA256 | 14b2ac356ed75d10ef40bbaaa48e7dd9fff7de9719c2a43ad123fe843dd4e4e2 | SHA-256 hash identified for the SoftManager module. |
| SHA256 | 7c08cf409194056a8517865e5d3433d1499bb8262263b55b49b8b07d9d182fcb | SHA-256 hash identified for the WinUpdate module. |
| SHA256 | adc4aa652965396b52e79435ca54987ae9eb21bf5e67de5e9461b09655165ee4 | SHA-256 hash identified for the REVSTEALER stealer. |
| SHA256 | c66d2b77b9e85c53391891212413ad9a99eb66f4b11c6a431e78884a5b2651e5 | SHA-256 hash identified for the LockAppHost module. |
MITRE ATT&CK
T1037.001 · Logon Script (Windows)SoftManager can persist through a logon script.T1053.005 · Scheduled TaskWinUpdate and SoftManager can use scheduled tasks for persistence.T1056.001 · KeyloggingProManager records text typed or pasted into wallet password and passphrase fields.T1090 · ProxySoftManager turns the victim machine into a reverse proxy that routes the attacker’s network traffic through the victim’s connection.T1115 · Clipboard DataWinUpdate watches the clipboard, replaces copied cryptocurrency addresses, and collects text resembling wallet recovery phrases.T1218.003 · CMSTPLockAppHost abuses the Windows CMSTP tool to seek administrator rights.T1496.001 · Compute HijackingLockAppHost runs a cryptocurrency miner with administrator rights.T1539 · Steal Web Session CookieREVSTEALER collects browser cookies and session data, including a Roblox session cookie.T1543.003 · Windows ServiceLockAppHost can persist as a service.T1547.001 · Registry Run Keys / Startup FolderThe modules can persist through a Registry Run key.T1555.003 · Credentials from Web BrowsersREVSTEALER collects browser passwords and, to obtain Chrome credentials protected by App-Bound Encryption, launches the browser in a debugger and reads the decryption key from memory.T1562.001 · Disable or Modify ToolsLockAppHost disables Windows Update services and tasks and adds exclusions to Microsoft Defender.
Malware
LockAppHostREVSTEALER and four previously unreported companion programs—ProManager, WinUpdate, SoftManager, and LockAppHost—that can remain on infected Windows systems after the main stealer deletes itself.ProManagerElastic Security Labs documented REVSTEALER and four previously unreported companion programs—ProManager, WinUpdate, SoftManager, and LockAppHost—that can remain on infected Windows systems after the main stealerRevStealerElastic Security Labs documented REVSTEALER and four previously unreported companion programs—ProManager, WinUpdate, SoftManager, and LockAppHost—that can remain on infected Windows systems after the main stealerSoftManagerLabs documented REVSTEALER and four previously unreported companion programs—ProManager, WinUpdate, SoftManager, and LockAppHost—that can remain on infected Windows systems after the main stealer deletes itself.WinUpdateSecurity Labs documented REVSTEALER and four previously unreported companion programs—ProManager, WinUpdate, SoftManager, and LockAppHost—that can remain on infected Windows systems after the main stealer deletes
Vendors
Products
Claude Opus 5 Free Desktopa miner, with distribution tied to game-cheat lures and fake software such as the impersonated “Claude Opus 5 Free Desktop” app.Microsoft Defender Antimalware Platformhijacks crypto transactions, turns victims into a reverse proxy, and can disable Windows Update and Microsoft Defender before dropping a miner, with distribution tied to game-cheat lures and fake software such as theMicrosoft Windowscompanion programs—ProManager, WinUpdate, SoftManager, and LockAppHost—that can remain on infected Windows systems after the main stealer deletes itself.Windows Updatesteals credentials, hijacks crypto transactions, turns victims into a reverse proxy, and can disable Windows Update and Microsoft Defender before dropping a miner, with distribution tied to game-cheat lures and fake