
PEEP Uses Chrome and Edge Extensions for Persistent Host Command Execution
Summary
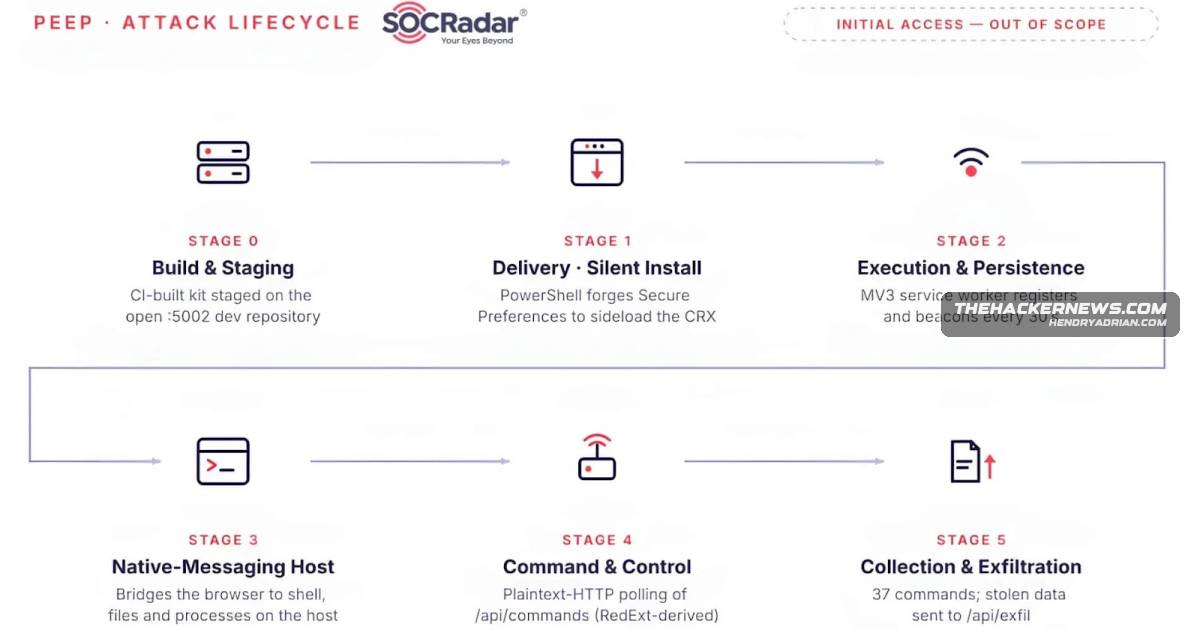
SOCRadar describes PEEP, a post-compromise toolkit that disguises itself as a Chrome and Edge bookmarks extension, steals browser data, and uses a native-messaging bridge for host commands. Its operators and targets remain unknown.
Key points
- PEEP requires prior administrative or code-execution access; it has no initial access vector of its own.
- It masquerades as the “Smart Bookmarks” extension and tampers with Chromium Secure Preferences to persist, using sideloading and enterprise installation policies.
- The toolkit collects browser history, cookies, active-tab data, and session details, and can hijack sessions and modify web pages.
- A native-messaging host enables shell commands, file management, and process and service discovery on the host.
- PEEP polls C2 infrastructure over plaintext HTTP for commands and uses separate endpoints for registration, task results, updates, and data exfiltration.
- SOCRadar links PEEP to the open-source RedExt framework; the activity remains unattributed, though Chinese-language source artifacts may indicate a Chinese-speaking actor.
- A C2 status endpoint showed 34 agent entries, 10 active sessions, and 507 data records, but researchers could not distinguish infections from test entries or verified deployments.
Article Details
- Attack Vectors
- PEEP requires an existing machine compromise or prior administrative or code-execution access; the article says it does not provide its own initial access vector.
- The installer sideloads a disguised Chrome/Edge extension and tampers with Chromium Secure Preferences to bypass Web Store checks and user prompts.
- PEEP uses enterprise force-install policies, external extension registration, and a ScriptCache fallback to maintain persistence.
- A native-messaging host bridges the browser extension to the operating system for shell-command execution, file management, and process and service discovery.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | xfjcc[.]fun | Reported PEEP command-and-control domain used for polling and data exfiltration. |
| IPV4 | 206[.]237[.]30[.]232 | Reported PEEP command-and-control endpoint used for polling and data exfiltration. |
MITRE ATT&CK
T1007 · System Service DiscoveryThe native-messaging host can discover system services.T1041 · Exfiltration Over C2 ChannelPEEP sends collected browser data, including cookies and browsing history, to its C2 through an exfiltration endpoint.T1057 · Process DiscoveryThe native-messaging host can discover processes on the compromised system.T1059.001 · PowerShellThe article names PowerShell scripts used to enable sideloading and modify Secure Preferences.T1071.001 · Web ProtocolsThe extension polls its C2 over plaintext HTTP for commands and uses HTTP endpoints for registration, updates, results, and exfiltration.T1113 · Screen CaptureThe article identifies screenshots as a browser-based command PEEP can run locally.T1115 · Clipboard DataThe article identifies clipboard access as a browser-based command PEEP can run locally.T1176 · Software ExtensionsPEEP masquerades as a Chrome/Edge bookmarks extension and is sideloaded into browser profiles.T1539 · Steal Web Session CookiePEEP collects session cookies and hijacks browser sessions.T1555.003 · Credentials from Web BrowsersThe article reports that PEEP steals credentials and extracts browser artifacts.
Malware
Products
EdgeSOCRadar revealed PEEP, a Chromium-based post-exploitation toolkit that disguises itself as a “Smart Bookmarks” extension and uses forged Secure Preferences values to persist in Chrome and Edge.Google ChromeSOCRadar revealed PEEP, a Chromium-based post-exploitation toolkit that disguises itself as a “Smart Bookmarks” extension and uses forged Secure Preferences values to persist in Chrome and Edge.