Huntress Says It Stopped MacSync Infostealer Before Data Exfiltration
Summary
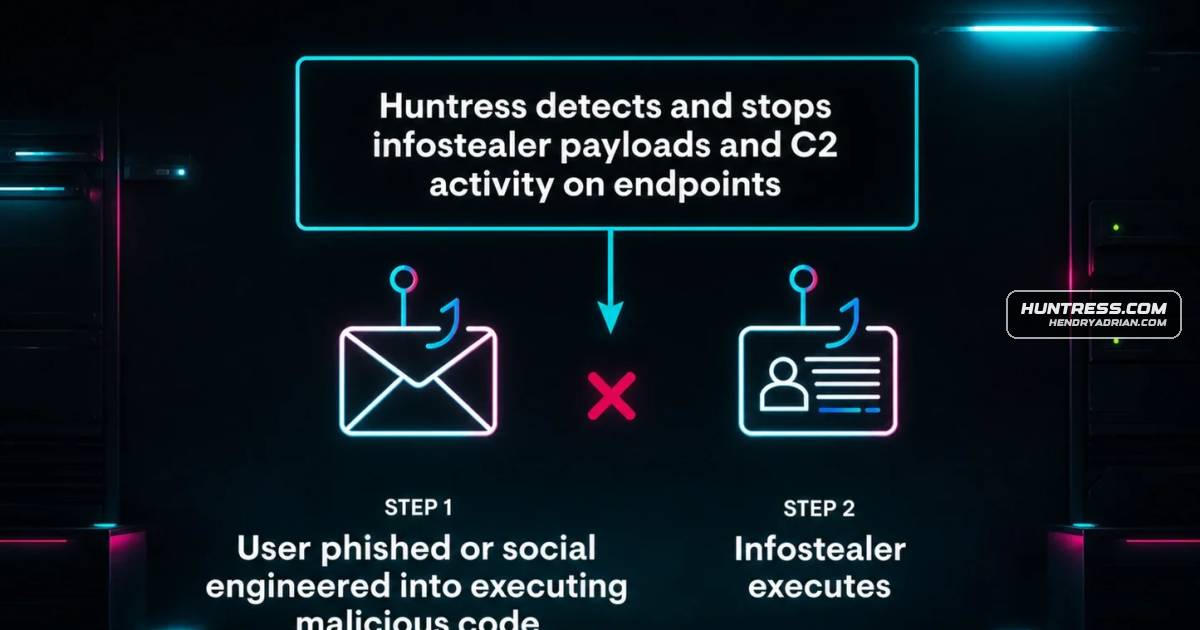
Huntress says a fake macOS Protection Service prompt led an employee to run MacSync, which collected sensitive data and prepared it for exfiltration. Huntress isolated the Mac before the upload, according to the company.
Key points
- Huntress reports that an employee entered their password into a fake “macOS Protection Service” prompt, launching the MacSync infostealer.
- The malware targeted browser data, Apple Keychain credentials, crypto wallets, and other files, staging them in /tmp/salmonela/.
- MacSync attempted to zip the staged data and send it to a command-and-control server using curl.
- Huntress says its detection and SOC analysts identified the activity and isolated the endpoint before the data could be exfiltrated.
- Huntress says the customer received remediation guidance and the endpoint was restored without a full rebuild.
- The article recommends user education about suspicious prompts, limiting local privileges, endpoint monitoring, and rotating credentials and invalidating sessions after an infostealer infection.
Article Details
- Victim Organization
- Not disclosed
- Incident Type
- MacSync infostealer attack involving credential and data collection, with exfiltration attempted but prevented by endpoint isolation.
- Disclosure Date
- 2026-03-18
- Data Types Exposed
- Chrome cookies and saved logins
- Safari data
- Apple Keychain credentials
- Crypto wallet data
- Notes, documents, and other sensitive files stored on disk
- Affected Records
- Not disclosed
- Affected Data Size
- Data was staged locally in /tmp/salmonela/; no data was exfiltrated.
- Operational Impact
- The endpoint was isolated from the network and returned to a safe state without a full rebuild. The article says Huntress contained the activity before the attacker could receive the staged data.
- Ransom Or Extortion
- None reported
- Claim Status
- confirmed
MITRE ATT&CK
T1027.013 · Encrypted/Encoded FileThe article describes use of curl, a legitimate binary, in preparing the data for exfiltration.T1041 · Exfiltration Over C2 ChannelMacSync attempted to POST the archive to a command-and-control server; Huntress says isolation prevented the data from being exfiltrated.T1056.002 · GUI Input CaptureThe user entered their password into a fake macOS Protection Service dialog presented by the attacker.T1070.004 · File DeletionThe malware attempted to delete the archive after the attempted exfiltration.T1074.001 · Local Data StagingCollected data was staged locally in /tmp/salmonela/ before attempted exfiltration.T1539 · Steal Web Session CookieThe infostealer targeted browser cookies, including Chrome cookies.T1555.001 · KeychainMacSync attempted to access credentials stored in Apple Keychain.T1555.003 · Credentials from Web BrowsersThe article reports collection of credentials and saved logins from browsers.T1560.001 · Archive via UtilityMacSync zipped the staged contents into an archive.
People
Malware
Vendors
Products
Apple KeychainApple Keychain credentialsGoogle ChromeChrome cookies and Safari dataHuntress Managed EDRWhile MacSync was trying to quietly plate up stolen data, Huntress Managed EDR and our 24/7 AI-Centric SOC were already on the case.macOSIn a recent attack observed by the Huntress AI-Centric SOC, one employee fell for what looked like an official “macOS Protection Service” prompt.SafariChrome cookies and Safari data