PamStealer macOS Variant Uses Live C2 Key Exchange and Multiple Persistence Methods
Summary
A new PamStealer macOS variant uses a fake Wavel wallet site, server-assisted payload decryption, and multiple persistence methods. Its Swift stealer targets passwords, keychain items, browser credentials, and system data.
Key points
- A fake Wavel wallet site directs victims to download Wavel.dmg, which launches a JXA carrier that passes execution to a zsh dropper.
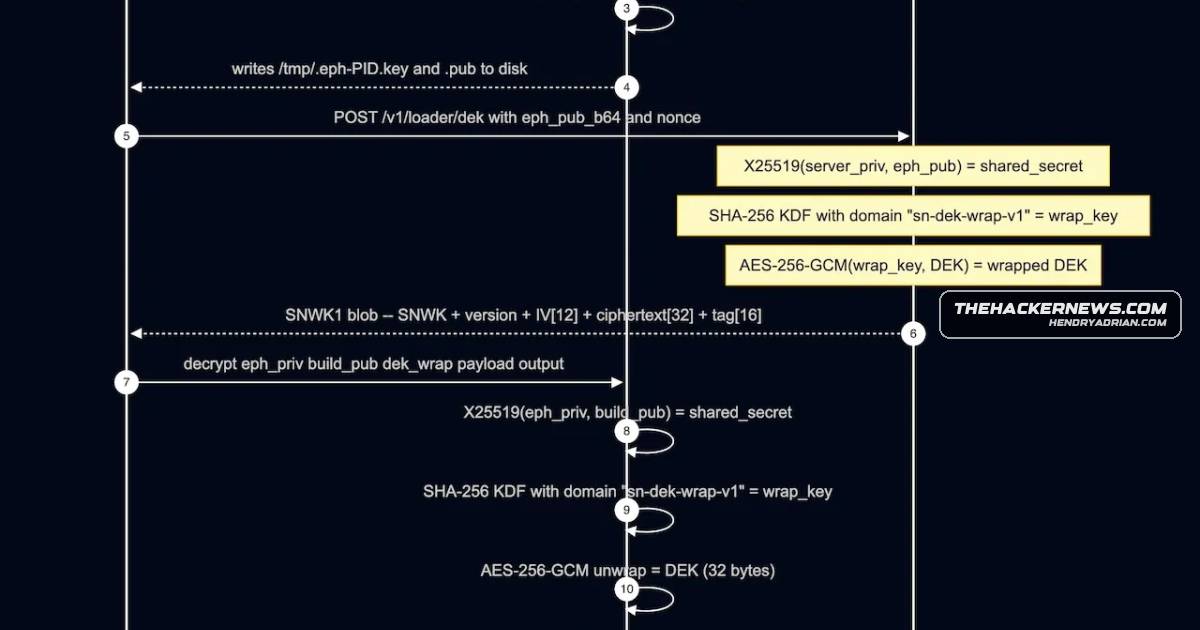
- The dropper downloads the pkgunpack utility from wavel[.]apple03cloudstore[.]com and uses an X25519 key exchange with the server to decrypt and stage the payload.
- Researchers say the payload cannot be recovered statically without server cooperation; each execution generates an ephemeral keypair.
- Persistence includes a LaunchAgent, a repair script, a shell hook, and Git hooks that trigger the repair script during checkout or commit actions.
- The Swift stealer collects passwords, keychain items, browser credentials, system metadata, user files, process lists, and installed applications.
- The malware can upload the staging directory as a ZIP archive and suppress notifications about new background login items.
Article Details
- Attack Vectors
- A fake Wavel cryptocurrency-wallet website distributes the Wavel.dmg disk image, which contains a compiled AppleScript file that launches a JXA dropper.
- The JXA carrier decodes a base64 string and pipes it to /bin/zsh -s for execution.
- The zsh dropper downloads and invokes the pkgunpack decryption utility from wavel.apple03cloudstore[.]com, exchanges X25519 keys with the server, and decrypts and stages the payload.
- The malware establishes persistence through a LaunchAgent, a repair zsh script, and a shell hook in ~/.zshrc; it also places repair scripts in Git hook directories and sets core.hooksPath so Git checkout or commit actions trigger the repair script.
- The Swift stealer collects passwords, keychain items, browser credentials, system metadata, user files, and a ZIP archive of the staging directory for upload.
- Defensive Notes
- The article reports that payload decryption requires cooperation from the live C2 server; static recovery is not possible without the server-held private key.
- A fresh ephemeral keypair is generated for each execution, preventing a captured DEK from being replayed to decrypt the payload.
- Review unexpected LaunchAgents, zsh startup files, Git hook paths, and files under ~/Library/Application Support/System/.githooks/ for persistence described in the article.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | wavel[.]app | Fake Wavel wallet site used to lure victims and deliver the malicious Wavel.dmg disk image. |
| DOMAIN | wavel[.]apple03cloudstore[.]com | Host from which the zsh dropper downloads the pkgunpack decryption utility. |
MITRE ATT&CK
T1053.005 · Scheduled TaskA LaunchAgent is installed to provide persistence.T1056.002 · GUI Input CaptureThe stealer presents a fake crash dialog to capture the system password and validates entered information using PAM.T1059.003 · Windows Command ShellThe malware adds repair scripts to Git post-checkout and pre-commit hook locations and configures core.hooksPath to trigger them.T1059.004 · Unix ShellThe dropper and repair script use zsh, including execution via /bin/zsh -s.T1059.007 · JavaScriptThe JXA carrier decodes a base64 string and passes it to /bin/zsh -s for execution.T1204.002 · Malicious FileVictims are lured to download and open Wavel.dmg, triggering the AppleScript and JXA execution chain.T1546.004 · Unix Shell Configuration ModificationA shell hook appended to ~/.zshrc runs the repair script in new interactive zsh sessions.T1547.011 · Plist ModificationThe malware installs a LaunchAgent as one of its persistence methods.T1555.001 · KeychainThe Swift stealer enumerates and retrieves macOS keychain items.T1555.003 · Credentials from Web BrowsersThe stealer targets credentials stored by Chromium- and Firefox-based browsers.T1560.001 · Archive via UtilityThe malware packages the staging directory as a ZIP archive before uploading it.
People
Malware
Products
macOSPamStealer has appeared in a new macOS variant that uses a server-side decryption chain, making the payload impossible to recover statically without live C2 cooperation.Script EditorOpening the file launches Apple’s built-in Script Editor with instructions to trigger the execution of a JXA dropper.WavelThe campaign lures victims through a fake Wavel cryptocurrency wallet site and ultimately steals passwords, keychain items, browser credentials, and system data from compromised Macs.