
Qilin Developer Arrest and Reported Haise Identification Highlight Enforcement Limits
Summary
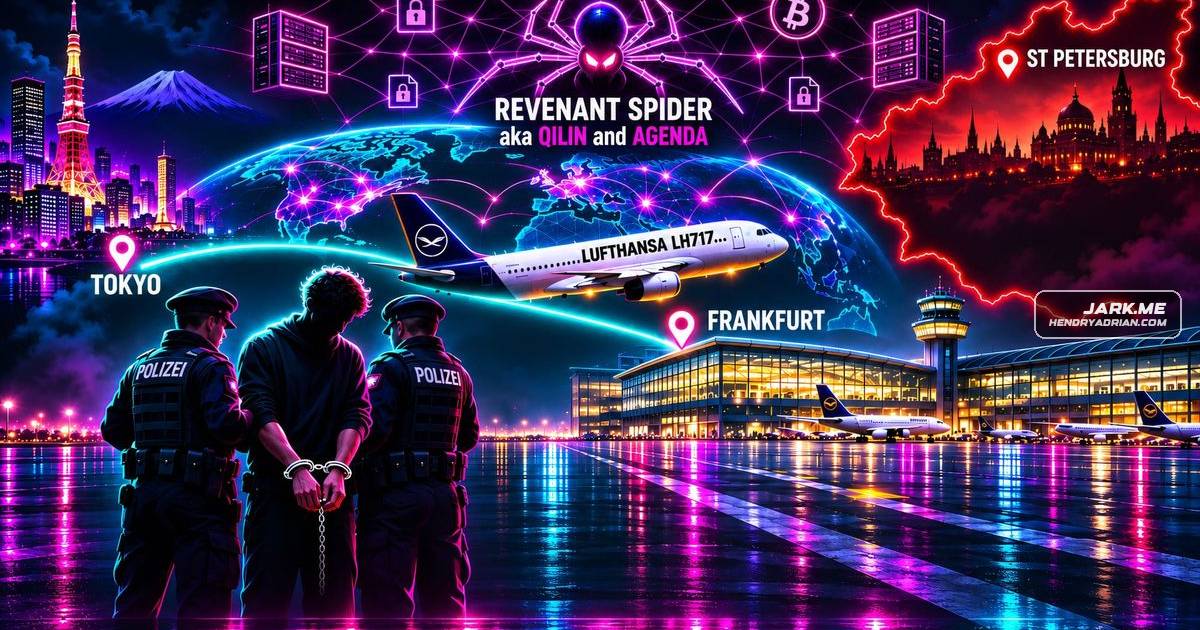
A Russian suspect known as Snake was transferred to Germany, where authorities allege he developed Qilin. KrebsOnSecurity separately identified Haise as Aleksey Yakovtsev; the article notes the attribution is unconfirmed by government and its evidence may overlap.
Key points
- German authorities allege Snake is a core Qilin member and developer wanted over a 2024 attack on a logistics company; he was detained in Osaka in May 2026 and transferred to Germany on October 2.
- KrebsOnSecurity identified Qilin persona Haise as Aleksey Yakovtsev, citing linked forum accounts, a persistent Telegram identifier, and identity datasets. Yakovtsev did not respond, and no government has publicly charged or identified him as Haise.
- The article assesses the Haise attribution with moderate confidence but cautions that the published investigations may rely on overlapping archives and leaked datasets, which limits independent corroboration.
- Qilin continued posting victims after Snake's detention. Trellix counted 655 Qilin victim posts from April through September 2026, 22% fewer than in the prior six months; the article says the timing does not establish that the arrest caused the decline.
- Trellix counted 719 posts for rival The Gentlemen over the same period. Group-IB traces the operation to former Qilin affiliate crew ArmCorp, which reportedly split with Qilin over an unpaid commission.
- PRODAFT reported largely automated Qilin affiliate exploitation of FortiGate devices through CVE-2024-21762 and CVE-2024-55591 in 2025, with people selecting the victims.
Article Details
- Event Type
- Ransomware investigation, arrest, and public attribution of alleged Qilin leadership
- Impact
- Japanese police detained a 28-year-old Russian national known as Snake in Osaka; German authorities allege he is a core REVENANT SPIDER/Qilin member and central software developer, and transferred him to Germany on October 2, 2026. Separately, KrebsOnSecurity identified Aleksey Mikhailovich Yakovtsev as the Haise persona, which fronted Qilin's affiliate program; the article assesses that attribution with moderate confidence, but no government has charged or publicly identified Yakovtsev as Haise. Qilin continued operating after Snake's detention. German investigators attribute nearly 4,000 attacks worldwide since 2024 to Qilin affiliates, with demands approaching US$3 billion and more than US$140 million reportedly paid. A Qilin-attributed 2024 attack on Synnovis disrupted London hospital services and forced more than 800 planned operations to be rescheduled in its first week. Qilin claimed the 2025 Asahi Group attack; the article provides no measured impact for that claim.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | holapor67[.]top | Defanged domain listed as a confirmed indicator in the Cisco Talos Qilin incident set. |
| DOMAIN | regsvchst[.]com | Defanged domain listed as a confirmed indicator in the Cisco Talos Qilin incident set. |
| IPV4 | 85[.]239[.]34[.]91 | Defanged IPv4 address listed as a confirmed indicator in the Cisco Talos Qilin incident set. |
| IPV4 | 86[.]106[.]85[.]36 | Defanged IPv4 address listed as a confirmed indicator in the Cisco Talos Qilin incident set. |
| SHA256 | 8fe746dd277e644fa0337db3394f0eadfafe57df029e13df9feef25c536adf4d | SHA-256 of a Qilin ransomware sample, detected as Win.Ransomware.Qilin by Cisco Talos. |
| SHA256 | dbe9ed8e8e8cdff3670e7205cb9f11b5a0fa9d1983a6c6bab67527d8775c4ffd | Hash listed in the confirmed Cisco Talos Qilin incident indicator set; the article identifies the set's hashes as samples from those incidents. |
| SHA256 | dd29138bf369863c33402a3fc995458ab5fc015a13a9378022131ab31d940c9f | Hash listed in the confirmed Cisco Talos Qilin incident indicator set; the article identifies the set's hashes as samples from those incidents. |
| SHA256 | e129dd5cc80f39b24db489df999c847335d169910bd966814d2f81b0b1bbc365 | Hash listed in the confirmed Cisco Talos Qilin incident indicator set; the article identifies the set's hashes as samples from those incidents. |
MITRE ATT&CK
T1003.001 · LSASS MemoryOperators enabled WDigest plaintext credential retention and used Mimikatz and related utilities to recover logon material.T1021.001 · Remote Desktop ProtocolOperators used RDP from a compromised VPN to reach a domain controller and internal hosts.T1021.002 · SMB/Windows Admin SharesQilin.B used PsExec to copy and execute an encryptor across remote Windows hosts.T1048 · Exfiltration Over Alternative ProtocolA script sent consolidated credential data to an attacker-controlled SMTP server.T1053.005 · Scheduled TaskA scheduled task ran a ransomware executable disguised as a TeamViewer installer at logon.T1059.001 · PowerShellQilin operators used PowerShell to disable AMSI, query Active Directory, clear event logs, and alter vCenter and ESXi settings.T1070.001 · Clear Windows Event LogsQilin used PowerShell and Mimikatz functionality to clear Windows event logs.T1133 · External Remote ServicesCisco Talos reported entry through a victim VPN and use of remote access paths into the internal network.T1190 · Exploit Public-Facing ApplicationReported Qilin affiliates exploited internet-facing FortiGate devices and Veeam Backup & Replication through identified vulnerabilities.T1486 · Data Encrypted for ImpactQilin.B encrypted local systems and network shares using separate encryptors.T1490 · Inhibit System RecoveryQilin changed Volume Shadow Copy Service configuration and deleted shadow copies.T1537 · Transfer Data to Cloud AccountCyberduck was used to upload stolen data to cloud storage, including a reported Backblaze destination.T1547.001 · Registry Run Keys / Startup FolderA Qilin executable and its password argument were added to the Windows Run key for execution after reboot.T1555.003 · Credentials from Web BrowsersMimikatz and SharpDecryptPwd collected saved credentials from Chrome and other client applications.T1560.001 · Archive via UtilityWinRAR was used to package selected victim data before exfiltration.
CVE
CVE-2023-27532Veeam · Veeam backup & replicationQilin exploited CVE-2023-27532 in internet-facing Veeam Backup & Replication to extract stored credentials, then reached the backup server over RDPCVE-2024-21762Fortinet · FortiOS; Fortinet · FortiProxyPRODAFT reports largely automated Qilin exploitation of FortiGate devices through CVE-2024-21762 and CVE-2024-55591, with humans choosing only the victims.CVE-2024-55591Fortinet · FortiOS; Fortinet · FortiProxyPRODAFT reports largely automated Qilin exploitation of FortiGate devices through CVE-2024-21762 and CVE-2024-55591, with humans choosing only the victims.
People
Herbert ReulNorth Rhine-Westphalia Interior Minister who publicly characterized Snake's arrest as Germany's biggest blow against cyber crime.Leo BogodIntelHawk's Leo Bogod described the account's reported progression from carding and traffic arbitrage to malware, botnets, and payment infrastructure.
Threat Actors
Aleksey Mikhailovich YakovtsevKrebsOnSecurity identified Yakovtsev as the likely controller of the Haise persona and linked accounts; the article assesses this attribution with moderate confidence, while noting no government has charged or publicly named him as Haise.HaiseQilin administrator and spokesperson persona that fronted the affiliate program. KrebsOnSecurity identified Aleksey Mikhailovich Yakovtsev as its likely controller; the article assesses the attribution with moderate confidence and notes that no government has publicly charged or identified him as Haise.Moonstone SleetMicrosoft reportedly observed this North Korean adversary deploying Qilin ransomware in 2025. Bitdefender assessed its involvement in the Korean Leaks campaign as plausible and probable, but the article says attribution remains unconfirmed.QilinRansomware-as-a-service operation whose affiliates are reported to have conducted attacks worldwide; German investigators attribute nearly 4,000 attacks since 2024 to its affiliates.RjunForum account sharing a Telegram handle later linked to Haise; Flashpoint profiled it as a broker trading stolen logs, traffic, and corporate access.Scattered SpiderMicrosoft reportedly observed this adversary deploying Qilin and RansomHub payloads in 2024; the article cautions that this use does not establish membership in Qilin's core or shared direction.StinkbugNamed in the article's entity annex as an alias of REVENANT SPIDER/Qilin.TurlaPersona of the Russian national detained in Japan and transferred to Germany. German investigators allege he was a core Qilin member and central software developer, and link him to a September 2024 attack on a logistics company.
Malware
Qilinhim as "Snake." They allege he is a core member and central software developer of REVENANT SPIDER (aka Qilin, Agenda), one of the most prolific ransomware-as-a-service operations of the past two years. Japan had itsQilin.BQilin.B used PsExec to copy and execute one encryptor across remote Windows hostsSystemBCThe complete Cisco Talos collection includes additional ScreenConnect, Cyberduck, Mimikatz, HRSword, network scanning, SystemBC, and Cobalt Strike artifacts from the same incident set.
Vendors
Check PointTrellix places Qilin affiliates among the first to use a Check Point VPN zero-day in June and a Palo Alto Networks GlobalProtect authentication bypass in July.FortinetFortinet FortiOS out-of-bounds write vulnerability associated by Group-IB and PRODAFT with Qilin access through exposed Fortinet devicesPalo Alto NetworksTrellix places Qilin affiliates among the first to use a Check Point VPN zero-day in June and a Palo Alto Networks GlobalProtect authentication bypass in July.VeeamVeeam Backup & Replication vulnerability used in reported Qilin activity to obtain encrypted credentials from the configuration database
Products
Fortinet FortiGateAutomated FortiGate ExploitationFortiOSFortinet FortiOS out-of-bounds write vulnerability associated by Group-IB and PRODAFT with Qilin access through exposed Fortinet devicesFortiProxyFortiOS and FortiProxy authentication bypass vulnerability associated by Group-IB and PRODAFT with Qilin access through exposed Fortinet devicesGlobalProtectTrellix places Qilin affiliates among the first to use a Check Point VPN zero-day in June and a Palo Alto Networks GlobalProtect authentication bypass in July.Veeam Backup & ReplicationVeeam Backup & Replication vulnerability used in reported Qilin activity to obtain encrypted credentials from the configuration database
Tools
Cobalt StrikePsExec, Mimikatz, Cyberduck, Cobalt Strike, ScreenConnect, AnyDesk, Chrome Remote Desktop, Quick Assist, WinRAR, Backblaze, and other legitimate or dual-use products are not indicators by themselves.HRSwordThe threat actor disabled AMSI and attempted to stop or uninstall endpoint protection through service commands, dark-kill, and HRSwordMimikatzQilin used PowerShell and Mimikatz functionality to clear Windows event logsSharpDecryptPwdMimikatz and SharpDecryptPwd collected saved credentials from Chrome and other client applications
Countries
GermanyNorth Rhine-Westphalia, GermanyJapan(aka Qilin, Agenda), one of the most prolific ransomware-as-a-service operations of the past two years. Japan had its own stake in the case. Qilin claimed the 2025 attack on Asahi Group, one of the breaches I trackedNorth KoreaMicrosoft reports the North Korean adversary deploying Qilin, its first use of ransomware built by a ransomware-as-a-service provider.Russiaa border and entered German custody. Yakovtsev, if Krebs is right, appears to have kept his travel inside Russia. Western enforcement can arrest the first and expose the second. Qilin kept operating after the arrest,South Koreathe Korean Leaks campaign, with 33 claimed victims and 28 publicly listed, nearly all of them South Korean asset managers. Bitdefender attributes the shared access most probably to a compromised upstream ITUnited KingdomUnited Kingdom and InternationalUnited StatesUnited States, United Kingdom, and Australia