
ROMULUS ClickFix Attacks Use DLL Sideloading to Deliver CNCMachineRMS RAT
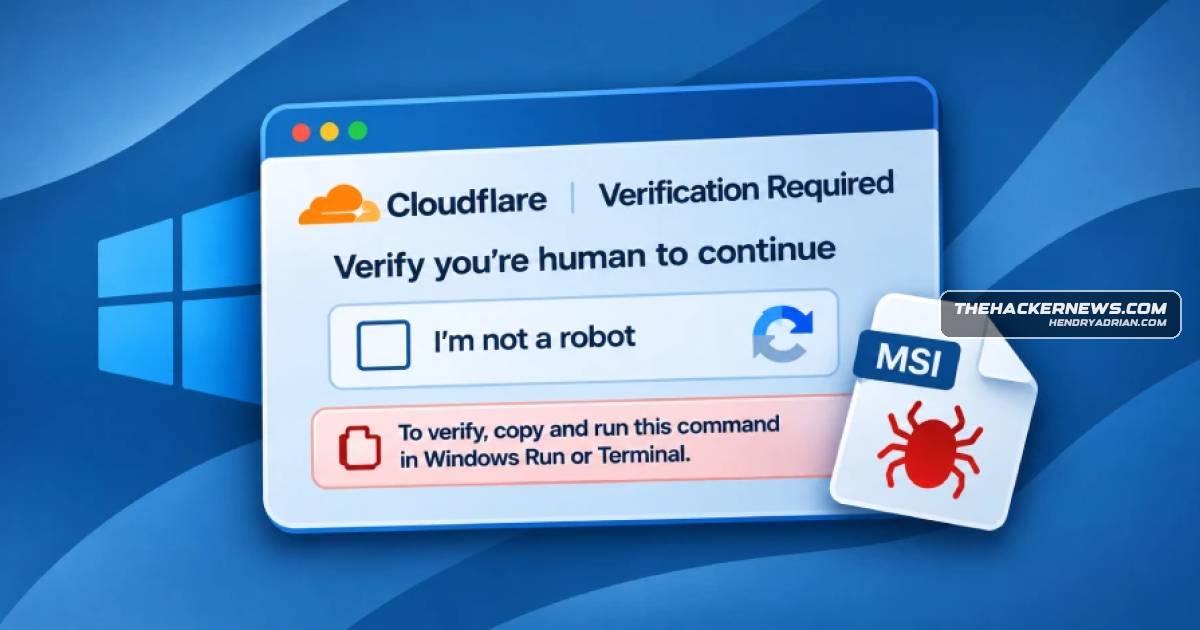
Summary
Blackpoint Cyber says ROMULUS uses separate ClickFix infection chains to deliver CNCMachineRMS and Legion Loader. One chain runs a disguised MSI via PowerShell, sideloads a DLL and launches the RAT, which supports remote control, surveillance, file management and DoH.
Key points
- Blackpoint Cyber researchers assess that ROMULUS distributes CNCMachineRMS and Legion Loader through separate infection chains.
- In one chain, a malicious MSI masquerading as Stardock Smart DeElevation Tool is executed with msiexec.exe through a PowerShell command.
- The MSI initiates DLL sideloading; the DLL decodes and runs embedded shellcode that launches CNCMachineRMS.
- The RAT supports remote desktop control, screen streaming, microphone and camera capture, file management, system reconnaissance and additional payload execution.
- The malware communicates with attacker-controlled infrastructure through DNS over HTTPS.
- The article also notes Huntress findings that some ClickFix campaigns use persistence, lateral movement, reconnaissance, credential theft and steganography.
Article Details
- Attack Vectors
- ROMULUS uses ClickFix-style lures to direct victims to malicious sites and deliver payloads.
- A malicious MSI installer masquerading as Stardock Smart DeElevation Tool is launched with msiexec.exe through a PowerShell command.
- The installer starts a DLL sideloading chain that runs a malicious DLL; the DLL decodes embedded shellcode to launch CNCMachineRMS.
- Separate ROMULUS infection chains distribute CNCMachineRMS and Legion Loader.
- Related campaigns use ChatGPT Custom GPTs to direct victims to malicious sites; CNCMachineRMS has also been delivered through BabaDeda Loader using DLL sideloading with the signed IBM SPSS IDE executable.
MITRE ATT&CK
T1059.001 · PowerShellA PowerShell command is used to execute the malicious MSI installer.T1071.004 · DNSThe RAT communicates with attacker-controlled infrastructure through DNS over HTTPS.T1082 · System Information DiscoveryThe RAT performs system reconnaissance.T1113 · Screen CaptureThe RAT can stream the victim's screen.T1123 · Audio CaptureThe RAT can capture microphone audio.T1125 · Video CaptureThe RAT can capture camera video.T1140 · Deobfuscate/Decode Files or InformationI++u.dll decodes embedded shellcode before it is run to launch CNCMachineRMS.T1218.007 · MsiexecThe malicious MSI installer is executed using msiexec.exe.T1574.002 · DLL Side-LoadingThe installer initiates a DLL sideloading chain to run I++u.dll; a related chain sideloads through the signed IBM SPSS IDE executable.
People
Andi UrsryBlackpoint Cyber researcher whose report describes ROMULUS delivery chains and their malware.Nevan BealBlackpoint Cyber researcher whose report describes ROMULUS delivery chains and their malware.Sam DeckerBlackpoint Cyber researcher whose report describes ROMULUS delivery chains and their malware.
Malware
BabaDeda LoaderInterestingly, CNCMachineRMS has also been delivered via another malware loader called BabaDeda Loader through ClickFix attacks that employ DLL sideloading involving the legitimately signed IBM SPSS IDE executable.CNCMachineRMSThreat actors have been observed using the ROMULUS ClickFix malware delivery platform to deliver a previously undocumented remote access trojan (RAT) that shares similarities with CNCMachineRMS.Legion Loader"ROMULUS likely operates as a delivery service, distributing CNCMachineRMS and Legion Loader through separate chains while retaining ClickFix and signed binary sideloading techniques," Blackpoint Cyber researchers Sam
Products
ChatGPT Custom GPTsAttacks involving ROMULUS have also leveraged ChatGPT Custom GPTs as a pathway to direct unsuspecting victims to malicious sites that employ ClickFix lures to deliver a RAT payload by means of DLL sideloading.IBM SPSS IDEInterestingly, CNCMachineRMS has also been delivered via another malware loader called BabaDeda Loader through ClickFix attacks that employ DLL sideloading involving the legitimately signed IBM SPSS IDE executable.Stardock Smart DeElevation Toolexecuted using "msiexec.exe" by means of a PowerShell command. The installer masquerades as Stardock Smart DeElevation Tool, while initiating a DLL sideloading chain to run a malicious DLL ("I++u.dll").