
Google Disrupts UNC2814 Espionage Campaign Using GRIDTIDE Backdoor
Summary
Google GTIG, Mandiant and partners disrupted UNC2814’s espionage campaign, reporting 53 confirmed intrusions in 42 countries and suspected activity in at least 20 more. The GRIDTIDE backdoor used Google Sheets for C2; sensitive-data exfiltration was not directly seen.
Key points
- GTIG reported 53 confirmed intrusions in 42 countries and suspected infections in at least 20 more, targeting telecommunications and government organizations.
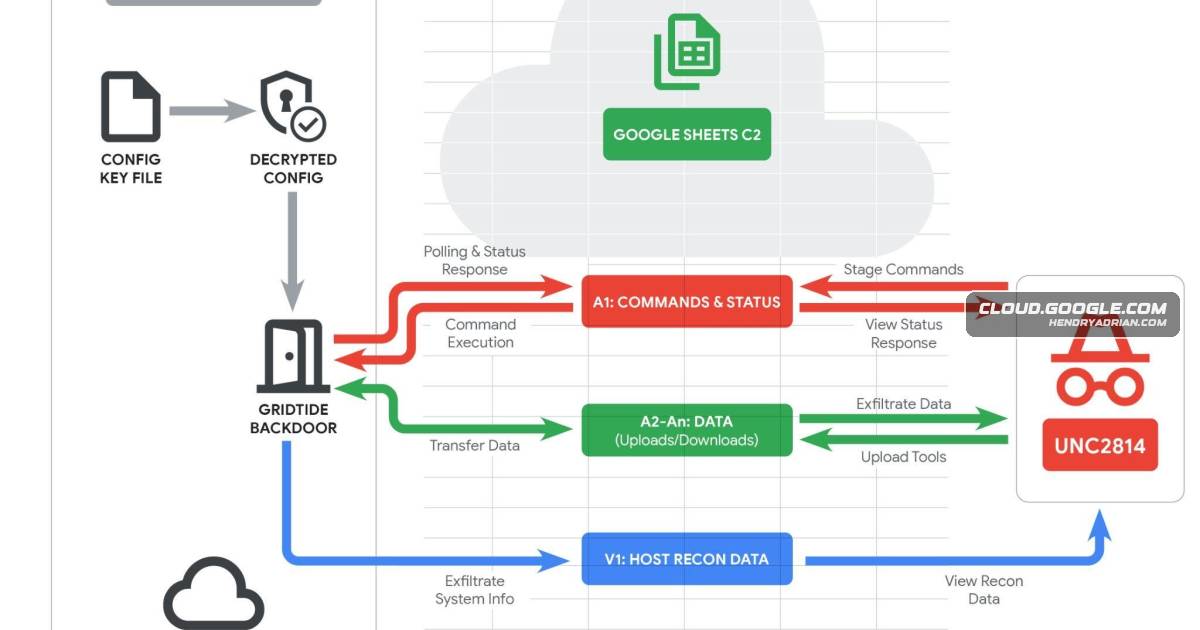
- GRIDTIDE is a C-based backdoor that uses Google Sheets cells as a command-and-control channel to run commands and transfer files.
- The malware uses a local 16-byte key to decrypt configuration data containing Google service-account credentials and a spreadsheet identifier.
- UNC2814 used a systemd service for persistence, SSH for lateral movement, and SoftEther VPN Bridge for outbound encrypted connectivity.
- Mandiant observed /var/tmp/xapt spawn a shell with root privileges; the campaign’s initial access vector remains undetermined.
- GTIG and partners terminated attacker-controlled cloud projects, disabled accounts and API access, disrupted infrastructure, notified victims, and released indicators and detection guidance.
- GTIG did not directly observe exfiltration of sensitive data during this campaign.
Article Details
- Attack Vectors
- The initial access vector for this campaign was not determined; UNC2814 has a history of gaining entry by exploiting and compromising web servers and edge systems.
- UNC2814 used a service account to move laterally via SSH.
- The operators deployed GRIDTIDE, a C-based backdoor, and established persistence with a systemd service at /etc/systemd/system/xapt.service.
- GRIDTIDE used Google Sheets API calls as a cell-based command-and-control channel, sending commands and transferring host data through spreadsheet cells.
- The operators deployed SoftEther VPN Bridge to establish an outbound encrypted connection.
- Defensive Notes
- Hunt for suspicious executables launched from /var/tmp that spawn a shell, including the observed /var/tmp/xapt process behavior.
- Review creation or modification of suspicious configuration files in /var/tmp, /usr/sbin, and /sbin, and inspect systemd services such as /etc/systemd/system/xapt.service.
- Investigate non-browser processes making outbound requests to Google Sheets API endpoints, particularly batchClear, batchUpdate, and valueRenderOption=FORMULA requests.
- Review SSH activity involving service accounts for signs of lateral movement.
- GTIG and partners reported terminating attacker-controlled Google Cloud projects, disabling attacker accounts and Sheets API access, sinkholing domains, and issuing victim notifications.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 1cv2f3d5s6a9w[.]ddnsfree[.]com | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | admina[.]freeddns[.]org | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | afsaces[.]accesscam[.]org | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | ancisesic[.]accesscam[.]org | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | applebox[.]camdvr[.]org | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | evilginx2[.]loseyourip[.]com | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | googlel[.]gleeze[.]com | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | googles[.]ddnsfree[.]com | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | telcomn[.]giize[.]com | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | telkomservices[.]theworkpc[.]com | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | transport[.]dynuddns[.]net | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | updatetools[.]giize[.]com | Listed as a C2 domain associated with UNC2814 infrastructure. |
| DOMAIN | vmtools[.]camdvr[.]org | Listed as a C2 domain associated with UNC2814 infrastructure. |
| IPV4 | 130[.]94[.]6[.]228 | Attacker-controlled download host for archives containing GRIDTIDE and SoftEther VPN Bridge components. |
| IPV4 | 195[.]123[.]211[.]70 | Listed as an attacker IP in the campaign's network indicators. |
| IPV4 | 202[.]59[.]10[.]122 | Listed as an attacker IP in the campaign's network indicators. |
| IPV4 | 38[.]180[.]205[.]14 | IP address targeted by a curl command to verify HTTPS access to the actor's infrastructure. |
| IPV4 | 38[.]54[.]112[.]184 | Listed as an attacker IP in the campaign's network indicators. |
| IPV4 | 38[.]60[.]171[.]242 | Listed as an attacker IP in the campaign's network indicators. |
| IPV4 | 38[.]60[.]194[.]21 | IP address identified as the threat actor's SoftEther VPN server. |
| IPV4 | 38[.]60[.]252[.]66 | IP address identified as hosting a malicious C2 domain. |
| SHA256 | 01fc3bd5a78cd59255a867ffb3dfdd6e0b7713ee90098ea96cc01c640c6495eb | SHA-256 hash of xapt.cfg, the key file GRIDTIDE uses to decrypt its Google Drive configuration. |
| SHA256 | 4eb994b816a1a24cf97bfd7551d00fe14b810859170dbf15180d39e05cd7c0f9 | SHA-256 hash of hamcore.se2, identified as a SoftEther VPN Bridge component. |
| SHA256 | 669917bad46a57e5f2de037f8ec200a44fb579d723af3e2f1be1e8479a267966 | SHA-256 hash of vpn_bridge.config, identified as a SoftEther VPN Bridge configuration. |
| SHA256 | ce36a5fc44cbd7de947130b67be9e732a7b4086fb1df98a5afd724087c973b47 | SHA-256 hash listed for the GRIDTIDE host artifact xapt. |
| SHA256 | d25024ccea8eac85a9522289cfb709f2ed4e20176dd37855bacc2cd75c995606 | SHA-256 hash of a self-signed X.509 certificate associated with attacker infrastructure. |
| SHA256 | eb08c840f4c95e2fa5eff05e5f922f86c766f5368a63476f046b2b9dbffc2033 | SHA-256 hash of the malicious xapt.service file created for GRIDTIDE persistence. |
| URL | hxxp[:]//130[.]94[.]6[.]228/amp.tar.gz | Archive download URL from attacker infrastructure; the archive contained the hamcore.se2 SoftEther VPN Bridge component. |
| URL | hxxp[:]//130[.]94[.]6[.]228/apt.tar.gz | Malicious archive download URL; the archive contained GRIDTIDE. |
| URL | hxxp[:]//130[.]94[.]6[.]228/update.tar.gz | Archive download URL from attacker infrastructure; the archive contained a SoftEther VPN Bridge component. |
MITRE ATT&CK
T1005 · Data from Local SystemGRIDTIDE read files from encoded local paths and transferred their contents to spreadsheet cells.T1016 · System Network Configuration DiscoveryGRIDTIDE collected the endpoint's local IP address during host-based reconnaissance.T1021.004 · SSHUNC2814 used a service account to move laterally within an environment via SSH.T1027 · Obfuscated Files or InformationGRIDTIDE used a URL-safe Base64 encoding scheme for data sent and received.T1033 · System Owner/User DiscoveryGRIDTIDE collected the victim's username, and the observed shell command retrieved user and group identifiers.T1036.005 · Match Legitimate Resource Name or LocationThe payload was likely named xapt to resemble a legacy tool and avoid suspicion.T1041 · Exfiltration Over C2 ChannelGRIDTIDE sent host metadata and command output to cells in the attacker-controlled spreadsheet used for C2.T1059.004 · Unix ShellGRIDTIDE executed Bash shell commands on the endpoint, including the observed sh -c id 2>&1 command.T1078 · Valid AccountsGRIDTIDE authenticated to the Google Sheets API using a Google service account and associated private key stored in its configuration.T1082 · System Information DiscoveryGRIDTIDE collected endpoint OS details and other system information during host reconnaissance.T1102.002 · Bidirectional CommunicationGRIDTIDE used Google Sheets for bidirectional C2, polling spreadsheet cells for commands and writing status and data back to cells.T1105 · Ingress Tool TransferGRIDTIDE supported transferring data from spreadsheet cells to the endpoint, including uploading tools.T1543.002 · Systemd ServiceThe operators created a systemd service at /etc/systemd/system/xapt.service for GRIDTIDE persistence.
Threat Actors
Malware
Vendors
Googlepartners disrupted UNC2814’s global espionage campaign that used a novel GRIDTIDE backdoor and abused the Google Sheets API as a covert C2 channel to target telecommunications and government organizations across dozensMandiantGTIG, Mandiant, and partners disrupted UNC2814’s global espionage campaign that used a novel GRIDTIDE backdoor and abused the Google Sheets API as a covert C2 channel to target telecommunications and government
Products
CentOSMandiant detected initial activity on a CentOS host where /var/tmp/xapt spawned a shell and executed ‘sh -c id 2>&1’, indicating privilege escalation to root.Google CloudThe operation terminated attacker-controlled Google Cloud Projects, disabled attacker accounts and infrastructure, and published IOCs to help defenders identify related activity.Google Security OperationsMandiant leverages Google Security Operations (SecOps) to perform continuous detection, investigation, and response across our global customer base.Google Sheetsdisrupted UNC2814’s global espionage campaign that used a novel GRIDTIDE backdoor and abused the Google Sheets API as a covert C2 channel to target telecommunications and government organizations across dozens ofGoogle WorkspaceGTIG’s disruption actions included terminating attacker Google Cloud projects, disabling attacker Google Workspace accounts and Sheets API access, sinkholing domains, issuing victim notifications, and releasing IOCs and
Tools
Industries
Governmentbackdoor and abused the Google Sheets API as a covert C2 channel to target telecommunications and government organizations across dozens of countries.Telecommunicationsused a novel GRIDTIDE backdoor and abused the Google Sheets API as a covert C2 channel to target telecommunications and government organizations across dozens of countries.