
LummaC2 Infection Exposes Suspected DPRK IT Worker's Fraud Operation
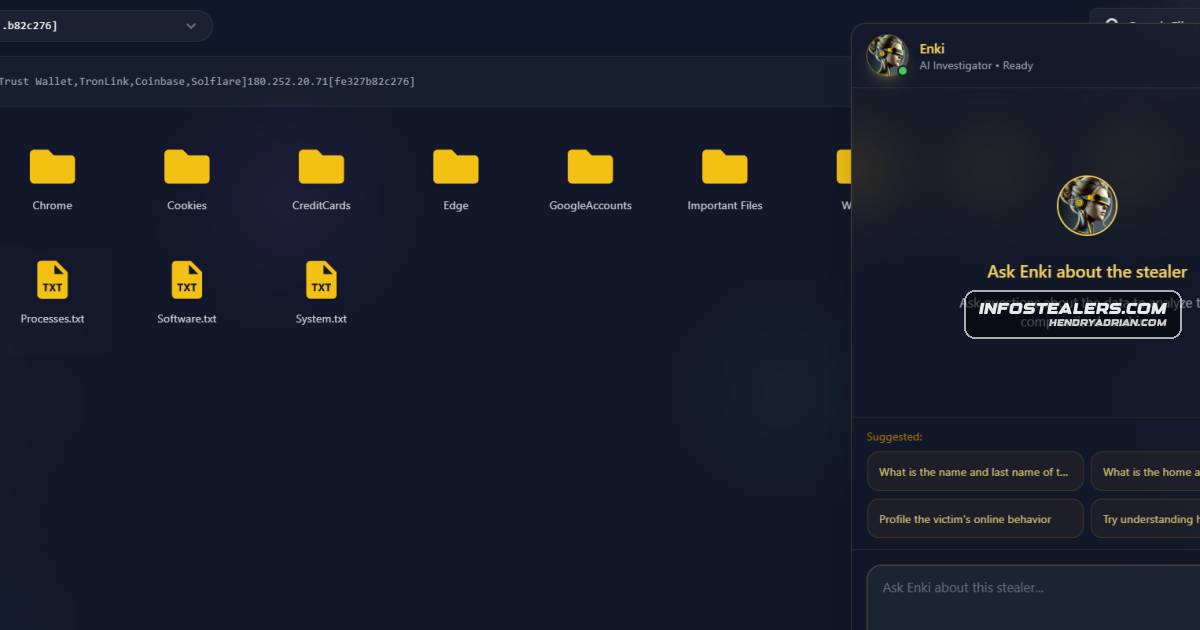
Summary
Researchers say LummaC2 logs from a machine linked to a suspected DPRK IT worker exposed an Indonesian proxy node and evidence of synthetic identities, crypto scams and a likely infection after GTA V cheat downloads.
Key points
- Researchers analyzing Hudson Rock telemetry say an infected machine linked to a suspected DPRK IT worker contained exfiltrated logs and corporate CDN credentials that led them to an undocumented Indonesian proxy node.
- Browser profiles, aliases and localized searches led the researchers to infer that the operator used synthetic identities and Indonesian browsing activity to disguise the proxy's use.
- Installed OBS Studio and OBS-VirtualCam, alongside searches for video and voice-generation tools, were presented as evidence of preparations to support synthetic identities in remote job interviews.
- Search history and administrative records indicated activity involving cloned cryptocurrency exchanges, task-scam portals and smart contracts intended to drain USDT; these are findings attributed to the researchers' analysis.
- The researchers report that on November 6, 2024, two game-cheat downloads preceded the LummaC2 log. They suggest a local facilitator's search for GTA V cheats may have led to the infection.
- The article describes analysis of 4,077 search queries, but the machine's ownership and the suspected DPRK connection remain the researchers' interpretation rather than independently established facts in the article.
Article Details
- Attack Vectors
- A suspected DPRK IT worker used synthetic identities and deepfake video tools to pass remote job interviews and gain access to Western companies.
- The operator used an Indonesian proxy node and localized browsing activity to make the connection appear residential and local.
- Fraudulent exchange interfaces and task-scam portals were used to seek cryptocurrency credentials and payments.
- A local facilitator likely downloaded GTA V cheat files from MediaFire; the files were identified as likely delivery files for the LummaC2 infection.
- Defensive Notes
- The article recommends hunting for behavioral indicators such as aaPanel deployments on non-standard ports.
- The article advises identifying fraudulent insiders before they gain network access, using behavioral markers and cybercrime telemetry.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 180[.]252[.]20[.]71 | Reported Indonesian proxy IP used by the suspected operator. |
| URL | hxxps[:]//director[.]grab-amazon[.]com | Fake task-scam portal; password logs reportedly showed direct administrative access. |
| URL | hxxps[:]//grab-alibaba[.]com/admin/login | Fake task-scam portal; password logs reportedly showed direct administrative access. |
| URL | hxxps[:]//mesta[.]cc/admin/dashboard/mdeposits | Administrative dashboard described as being used to manage deposits for a live crypto scam. |
| URL | hxxps[:]//www[.]mediafire[.]com/file/e86n68htfmac30x/Setup.zip/file | MediaFire download identified in the article's infection timeline as the likely LummaC2 payload disguised as Setup.zip. |
| URL | hxxps[:]//www[.]mediafire[.]com/file/xxmv2att7ampfqj/Setup.rar/file | MediaFire download linked to a Setup.rar file described as a likely LummaC2 delivery file. |
MITRE ATT&CK
T1005 · Data from Local SystemThe infostealer log contained files and browser-history data collected from the infected machine.T1036 · MasqueradingThe LummaC2 payload was reportedly disguised as a file named Setup.zip.T1056.003 · Web Portal CaptureThe operator sought exchange-cloning interfaces for fraudulent sites described as harvesting user credentials.T1090 · ProxyThe suspected operator used an Indonesian proxy node and reportedly seasoned its IP with localized browsing activity.T1105 · Ingress Tool TransferThe article links files downloaded from MediaFire to delivery of the LummaC2 payload.T1555.003 · Credentials from Web BrowsersThe LummaC2 infection exposed browser-stored credentials and other data from the infected machine.T1656 · ImpersonationThe operator used synthetic identities and deepfake video during remote job interviews to pose as a legitimate worker.
Malware
CraxsRATâ Hunting for CraxsRAT, a highly sophisticated Android Remote Access Trojan used for bypassing 2FA and hijacking mobile banking sessions.LummaC2analyzing Hudson Rock cybercrime telemetry found a suspected DPRK IT worker’s machine infected with the LummaC2 infostealer, and its exfiltrated logs revealed an undocumented Indonesian proxy node tied to a broad
Vendors
FunnullThe case exposed synthetic identities, deepfake tooling, CDN infrastructure laundering via Funnull, large-scale crypto scams, and a catastrophic OPSEC failure when a local facilitator downloaded game hacks thatHudson RockResearchers analyzing Hudson Rock cybercrime telemetry found a suspected DPRK IT worker’s machine infected with the LummaC2 infostealer, and its exfiltrated logs revealed an undocumented Indonesian proxy node tied to aSilent PushAs detailed in recent research by Silent Push on “infrastructure laundering,” services like Funnull are frequently leveraged by state-sponsored actors.
Products
BandicamBandicam & VideoProc: Used to capture “proof of work” or manipulate video assets before injecting them into the virtual camera stream.CavalierImage: Overview of the extracted files from the infected DPRK IT worker’s machine via Hudson Rock’s Cavalier platform.Edgethe alias “Ikbal,” the operator maintained dozens of accounts across five distinct Chrome profiles and one Edge profile to meticulously compartmentalize their operations.Google Chrome(180.252.20.71) and the alias “Ikbal,” the operator maintained dozens of accounts across five distinct Chrome profiles and one Edge profile to meticulously compartmentalize their operations.MediaFireA local facilitator downloading GTA V cheats from MediaFire likely triggered the infostealer infection, causing the OPSEC collapse.MetaMaskinfection didn’t just capture credentials; it exfiltrated 12 separate cryptocurrency wallet instances (MetaMask, Trust Wallet, TronLink, Solflare) carefully segregated across different browser profiles to prevent theOBS StudioOBS Studio & OBS-VirtualCam: This plugin routes pre-recorded videos or AI-generated deepfakes directly into software like Zoom or Teams, making the feed appear as a legitimate, physical webcam.OBS-VirtualCamOBS Studio & OBS-VirtualCam: This plugin routes pre-recorded videos or AI-generated deepfakes directly into software like Zoom or Teams, making the feed appear as a legitimate, physical webcam.SolFlareit exfiltrated 12 separate cryptocurrency wallet instances (MetaMask, Trust Wallet, TronLink, Solflare) carefully segregated across different browser profiles to prevent the cross-contamination of illicitTronLinkcapture credentials; it exfiltrated 12 separate cryptocurrency wallet instances (MetaMask, Trust Wallet, TronLink, Solflare) carefully segregated across different browser profiles to prevent the cross-contamination ofTrust Walletdidn’t just capture credentials; it exfiltrated 12 separate cryptocurrency wallet instances (MetaMask, Trust Wallet, TronLink, Solflare) carefully segregated across different browser profiles to prevent theVideoProcBandicam & VideoProc: Used to capture “proof of work” or manipulate video assets before injecting them into the virtual camera stream.
Countries
DPRKResearchers analyzing Hudson Rock cybercrime telemetry found a suspected DPRK IT worker’s machine infected with the LummaC2 infostealer, and its exfiltrated logs revealed an undocumented Indonesian proxy node tied to aIndonesia“jadwal indonesia kualifikasi piala dunia” / “bacaan sholat sebelum jumatan”