
Analysis Details Fake Telegram Site Delivering Multi-Stage Malware Loader
Summary
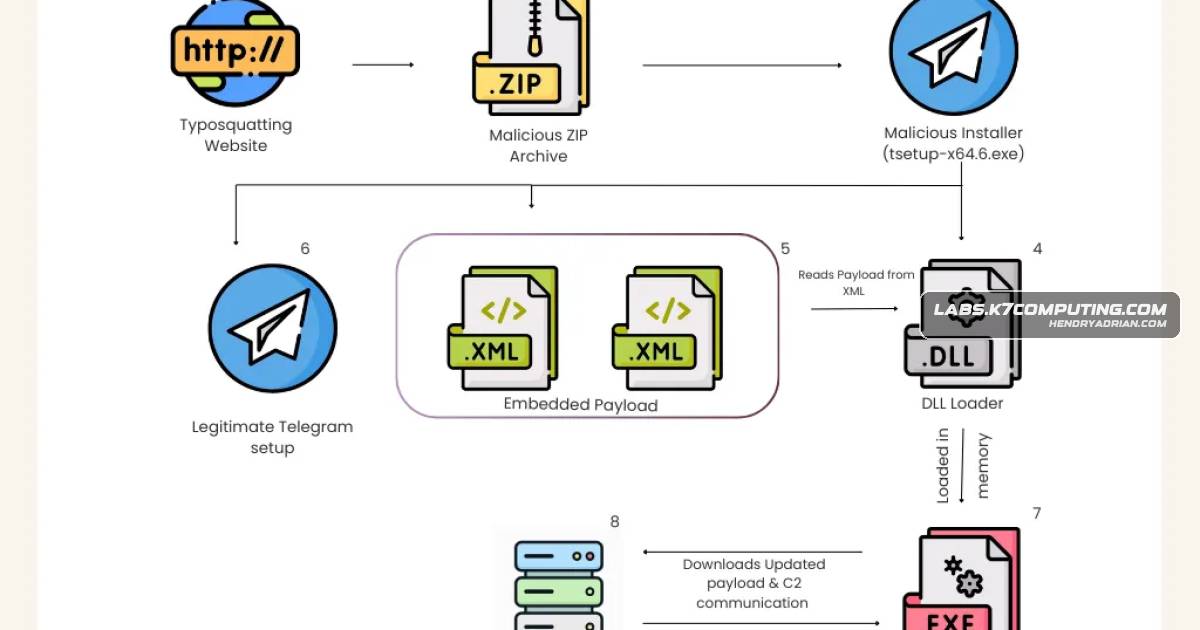
K7 researchers analyzed a fake Telegram download campaign using a typosquatted site to deliver a staged loader that adds Windows Defender exclusions, reconstructs a PE from XML in memory, and contacts a C2 server for commands and payload updates.
Key points
- A typosquatted Telegram download site, telegrgam[.]com, distributed the malicious installer tsetup-x64.6.exe.
- The installer added C:, D:, E: and F: to Windows Defender exclusions and dropped staged files under the Roaming Embarcadero directory.
- AutoRecoverDat.dll read encoded PE data from GPUCache.xml and manually reconstructed and loaded the payload in memory.
- The payload ran through rundll32.exe; analysis with x32dbg observed the PE being reconstructed and executed at runtime.
- The malware connected to jiijua[.]com at 27.50.59.77:18852; Wireshark analysis showed it downloading updated payload components.
- The installer created a registry infection marker and dropped a legitimate Telegram installer to make the installation appear normal.
Article Details
- Attack Vectors
- A typosquatted Telegram download site distributed the malicious installer tsetup-x64.6.exe.
- The installer launched commands through cmd.exe, enumerated processes, and added system drive partitions to Windows Defender exclusions using an obfuscated PowerShell command.
- The installer dropped staged files, including AutoRecoverDat.dll and GPUCache.xml, and used rundll32.exe to execute the DLL.
- The DLL reconstructed a PE payload from encoded data in an XML file and loaded it into memory.
- The loaded payload connected to command-and-control infrastructure over TCP to receive commands and updated payload components.
- Defensive Notes
- Download software only from official sources.
- The article recommends malicious-website blocking, citing K7 Antivirus as an example.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | jiijua[.]com | C2 domain associated with the malware's TCP communications and payload updates. |
| DOMAIN | telegrgam[.]com | Typosquatted Telegram download site identified as distributing the malicious installer. |
| DOMAIN | www[.]tejlegram[.]com | Typosquatted domain listed as part of the malicious campaign. |
| DOMAIN | www[.]telefgram[.]com | Typosquatted domain listed as part of the malicious campaign. |
| DOMAIN | www[.]telegrgam[.]com | Typosquatted domain listed as part of the malicious campaign. |
| IPV4 | 27[.]50[.]59[.]77 | C2 server contacted over TCP on port 18852. |
| MD5 | 62f8effc7690455abcb300e3574f0a93 | MD5 hash of the loaded payload. |
| MD5 | a9a5cc6b6766fec51b281b94f5f17ccd | MD5 hash of the malicious tsetup-x64.6.exe installer. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe PowerShell command used to modify Defender settings was obfuscated.T1057 · Process DiscoveryThe installer enumerated running processes and searched for 0tray.exe.T1059.001 · PowerShellAn obfuscated PowerShell command added drive partitions to Windows Defender exclusions.T1059.003 · Windows Command ShellThe installer launched commands through cmd.exe.T1105 · Ingress Tool TransferThe malware downloaded updated payload components from its C2 server.T1112 · Modify RegistryThe installer created a registry value identified in the article as HKCUMicrosoft UserSource.T1189 · Drive-by CompromiseThe malicious installer was distributed through a typosquatted Telegram download website.T1218.011 · Rundll32The malware used rundll32.exe to execute code from the dropped DLL.T1562.001 · Disable or Modify ToolsThe installer added drive partitions to Windows Defender exclusions, reducing antivirus scanning.T1620 · Reflective Code LoadingThe DLL reconstructed a PE payload from XML data and loaded it directly into memory.
Products
TelegramA typosquatted Telegram download site (telegrgam[.]com) distributed a malicious installer tsetup-x64.6.exe that modifies Windows Defender exclusions, drops staged payload files, and executes a DLL loader to reconstructWindows Defenderdownload site (telegrgam[.]com) distributed a malicious installer tsetup-x64.6.exe that modifies Windows Defender exclusions, drops staged payload files, and executes a DLL loader to reconstruct and run a PE