Researchers Tie Network-Edge Campaign to More Than 70,000 Exposed Credentials
Summary
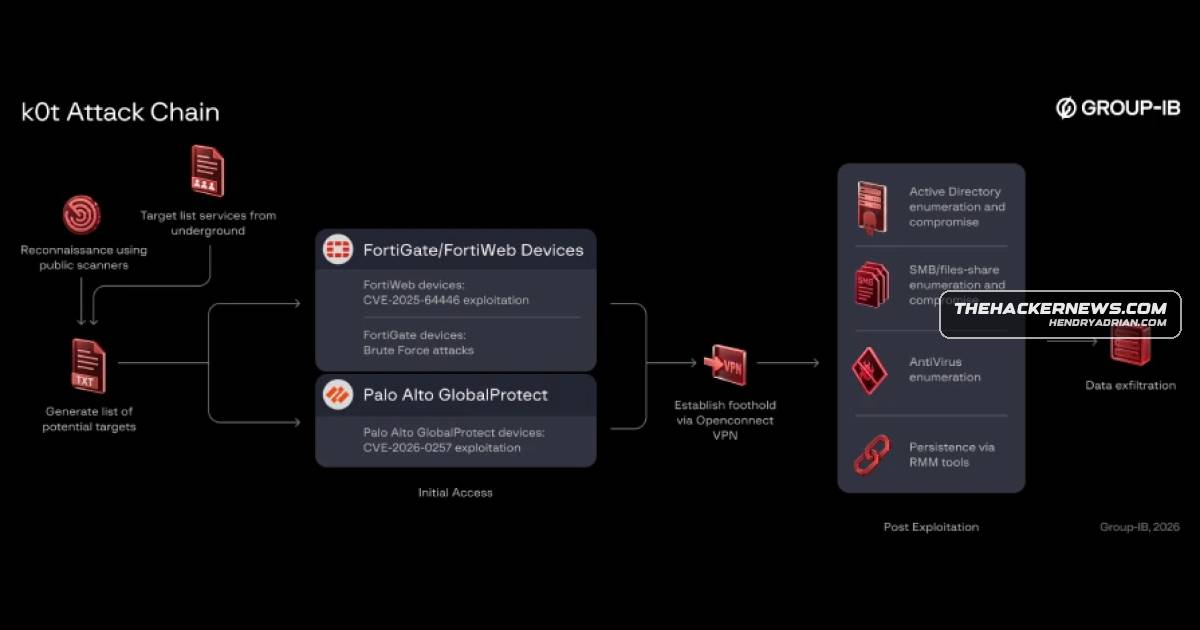
Group-IB and NyxLab link a campaign targeting exposed Fortinet and Palo Alto network devices to actor k0t, reporting persistent access attempts and more than 70,000 exposed credentials associated with the activity.
Key points
- Group-IB and NyxLab say the campaign targeted exposed Fortinet FortiGate and Palo Alto Networks GlobalProtect devices across organizations worldwide.
- The researchers attribute the activity to k0t, also known as CryptoFeel, Member19, and QazWsxShop.
- Investigation artifacts reportedly indicate access to numerous organizations, attempts to compromise some victims further, persistent remote access, and data exfiltration.
- More than 70,000 exposed credentials associated with network devices and LDAP dumps were identified in connection with the campaign.
- The researchers report negligible overlap with FortiBleed, while saying the activity may involve a separate dataset, operator subset, or related access operation.
- The actor's links to Qilin and The Gentlemen are unclear; some campaign victims were later listed on those groups' data-leak sites.
Article Details
- Event Type
- Campaign targeting exposed enterprise firewalls and VPNs
- Impact
- Group-IB and NyxLab report access to numerous organizations worldwide, with some victims further compromised through persistent remote access and data exfiltration. More than 70,000 exposed credentials associated with network devices and LDAP dumps were identified in connection with the campaign.
MITRE ATT&CK
Threat Actors
CryptoFeelAlias of k0t, the threat actor attributed the campaign to by the investigation.k0tThreat actor attributed the widespread exploitation activity to in the investigation.Member19Alias of k0t, the threat actor attributed the campaign to by the investigation.QazWsxShopAlias of k0t, the threat actor attributed the campaign to by the investigation.QilinRansomware group linked to the campaign because some victims were later listed on its data leak site; the exact connection is unclear.The GentlemenRansomware group linked to the campaign because some victims were later listed on its data leak site; the exact connection is unclear.
Vendors
FortinetCybersecurity researchers have disclosed details of a large-scale campaign that has targeted exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls.Palo Alto NetworksCybersecurity researchers have disclosed details of a large-scale campaign that has targeted exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls.
Products
Fortinet FortiGateCybersecurity researchers have disclosed details of a large-scale campaign that has targeted exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls.GlobalProtectCybersecurity researchers have disclosed details of a large-scale campaign that has targeted exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls.
Tools
Impacketcharacterized by the use of legitimate administrator and pentesting utilities like NetExec, SoftPerfect, Impacket, noPac, Kerbrute, PetitPotam, and Mimikatz to burrow deeper into victims' corporate environments.Kerbrutethe use of legitimate administrator and pentesting utilities like NetExec, SoftPerfect, Impacket, noPac, Kerbrute, PetitPotam, and Mimikatz to burrow deeper into victims' corporate environments.Mimikatzand pentesting utilities like NetExec, SoftPerfect, Impacket, noPac, Kerbrute, PetitPotam, and Mimikatz to burrow deeper into victims' corporate environments.NetExecThe attacks are also characterized by the use of legitimate administrator and pentesting utilities like NetExec, SoftPerfect, Impacket, noPac, Kerbrute, PetitPotam, and Mimikatz to burrow deeper into victims' corporatenoPacby the use of legitimate administrator and pentesting utilities like NetExec, SoftPerfect, Impacket, noPac, Kerbrute, PetitPotam, and Mimikatz to burrow deeper into victims' corporate environments.PetitPotamlegitimate administrator and pentesting utilities like NetExec, SoftPerfect, Impacket, noPac, Kerbrute, PetitPotam, and Mimikatz to burrow deeper into victims' corporate environments.SoftPerfectare also characterized by the use of legitimate administrator and pentesting utilities like NetExec, SoftPerfect, Impacket, noPac, Kerbrute, PetitPotam, and Mimikatz to burrow deeper into victims' corporate
Countries
CanadaGroup-IB and NyxLab researchers said. "His stated geographic priorities begin with the United States and Canada, followed by European countries and selected APAC markets."United StatesGroup-IB and NyxLab researchers said. "His stated geographic priorities begin with the United States and Canada, followed by European countries and selected APAC markets."