
Bitdefender Details LummaStealer Campaign Using CastleLoader, Maps 211 IoCs
Summary
Bitdefender’s DNS investigation links LummaStealer activity to CastleLoader and reports 211 IoCs. Telemetry showed 103,038 potential victim IPs communicating with 10 IoC IPs; the researchers advise further investigation of flagged entities.
Key points
- Bitdefender reports that LummaStealer operations continued after a 2025 law-enforcement disruption, adapting hosting and delivery methods including ClickFix.
- The analyzed campaign used CastleLoader for delivery, with in-memory execution and obfuscation described as ways to evade detection.
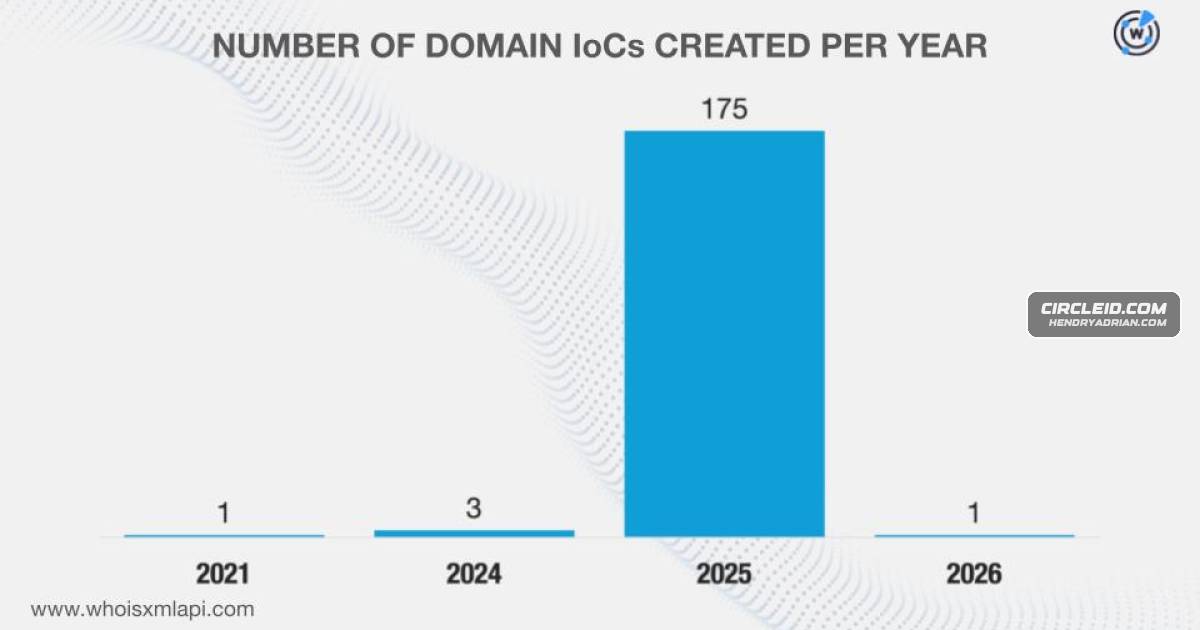
- Researchers compiled 211 IoCs: two subdomains, 180 domains, and 29 IP addresses, using historical DNS, WHOIS, and threat-intelligence data.
- Telemetry recorded 103,038 unique potential victim IPs across 115 ASNs communicating with 10 IoC IPs from January 16 to February 16, 2026; this does not by itself confirm compromise.
- The analysis identified 129 email-connected domains, 26 assessed as malicious, and 200 additional IPs, 196 of which had appeared in other malicious campaigns.
- The researchers caution that some entities labeled malicious may later be deemed harmless and recommend supplementary investigation.
Article Details
- Publisher
- CircleID
- Report Period
- 2025–2026; telemetry period: 2026-01-16 to 2026-02-16
- Scope
- Bitdefender-attributed DNS and network analysis of LummaStealer and CastleLoader infrastructure and related artifacts.
- Sample Size
- 211 network IoCs: 2 subdomains, 180 domains, and 29 IP addresses.
- Key Statistics
- The researchers identified 211 network IoCs: 2 subdomains, 180 domains, and 29 IP addresses.
- 103,038 unique potential victim IP addresses across 115 ASNs communicated with 10 IoC IP addresses between 2026-01-16 and 2026-02-16.
- Of 129 email-connected domains identified, 26 were reported as confirmed malicious.
- Of 200 additional IP addresses resolved from IoC domains, 196 had previously appeared in malicious campaigns.
- The report found 2,944 historical domain-to-IP resolutions across 161 IoC domains.
- Recommendations
- Conduct supplementary investigation to corroborate threat labels, since some entities identified as threats or malicious may later be deemed harmless in a different context.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | advennture[.]top | Reported as a confirmed malicious email-connected domain associated with malware distribution. |
| DOMAIN | boustrn[.]su | Reported as a confirmed malicious email-connected domain associated with malware distribution. |
| DOMAIN | consnbx[.]su | Reported as a confirmed malicious email-connected domain associated with malware distribution. |
| DOMAIN | cornerdurv[.]top | Reported as a confirmed malicious email-connected domain associated with malware distribution. |
| DOMAIN | coverxyzer[.]su | Reported as a confirmed malicious email-connected domain associated with malware distribution. |
| DOMAIN | diffuculttan[.]xyz | Listed as an IoC domain and as likely registered with malicious intent; the report says it was flagged 432 days before the report date. |
| DOMAIN | effecterectz[.]xyz | Listed as an IoC domain and as likely registered with malicious intent; the report says it was flagged 432 days before the report date. |
| DOMAIN | mannelaeksug[.]top | Listed as an IoC domain and as likely registered with malicious intent; the report says it was flagged 390 days before the report date. |
| DOMAIN | sterilizeflow[.]top | Listed as an IoC domain and as likely registered with malicious intent; the report says it was flagged 390 days before the report date. |
| DOMAIN | weighcobbweo[.]top | Listed as an IoC domain and as likely registered with malicious intent; the report says it was flagged 390 days before the report date. |
| HOSTNAME | convfx[.]windowmv[.]com | Listed as an IoC subdomain; the report says its naming resembles malware C2 or phishing infrastructure, while describing that assessment as characteristic rather than conclusive. |
| HOSTNAME | suzoo[.]ryxuz[.]com | Listed as an IoC subdomain; the report describes its randomly generated-looking subdomain and base domain as characteristic of DGA infrastructure. |
| IPV4 | 144[.]172[.]115[.]212 | Listed as an IoC IP address; the report also includes it among additional IPs resolved from IoC domains. |
| IPV4 | 185[.]121[.]233[.]78 | Listed as an IoC IP address in the report's network-infrastructure analysis. |
| IPV4 | 206[.]189[.]97[.]184 | Listed as an IoC IP address; the report also includes it among additional IPs resolved from IoC domains. |
| IPV4 | 31[.]220[.]109[.]219 | Listed as an IoC IP address in the report's network-infrastructure analysis. |
| IPV4 | 85[.]90[.]196[.]155 | Listed as an IoC IP address in the report's network-infrastructure analysis. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe report describes heavy obfuscation used to hinder detection and analysis.T1036 · MasqueradingThe report describes infrastructure domains mimicking legitimate software names, potentially spoofing “Windows.”T1055 · Process InjectionThe report says CastleLoader enabled in-memory execution of payloads.T1071 · Application Layer ProtocolThe report describes malware C2 communications using domain and IP infrastructure.T1105 · Ingress Tool TransferThe report identifies CastleLoader as the delivery mechanism for deploying infostealer payloads.T1204 · User ExecutionThe report describes user-interaction delivery techniques, including ClickFix.T1483 · Domain Generation AlgorithmsThe report characterizes randomly generated-looking domain strings as indicative of DGA infrastructure.
Malware
CastleLoaderhosting, adopting alternative loaders and delivery techniques (including ClickFix), and pairing with CastleLoader to enable in-memory execution and heavy obfuscation.LummaStealerLummaStealer resurfaced after a 2025 law-enforcement disruption by rapidly migrating hosting, adopting alternative loaders and delivery techniques (including ClickFix), and pairing with CastleLoader to enable in-memory