
Researchers Detail Espionage Campaigns Targeting Pakistani Police
Summary
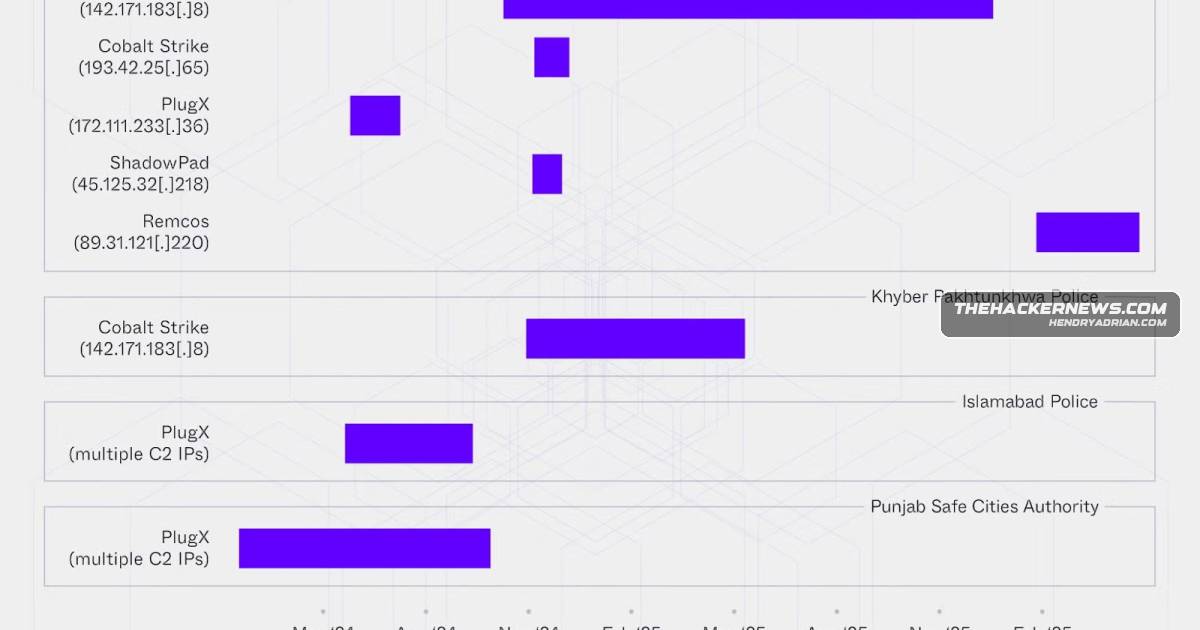
SentinelLABS reported espionage targeting Pakistani law enforcement from 2024 to 2026. Researchers linked four malware clusters to compromised systems, including a Balochistan Police portal used to host implants; China- and India-aligned actors are suspected.
Key points
- SentinelLABS reported activity against Balochistan, Khyber Pakhtunkhwa and Islamabad police, and the Punjab Safe Cities Authority, from February 2024 to April 2026.
- Targeted systems held biometric, criminal, personnel, hotel and tenant-registration records.
- Researchers identified clusters using PlugX, ShadowPad, Cobalt Strike and Remcos RAT.
- A compromised Balochistan Police Complaint Management System hosted two implant variants: a Rust stager that downloads a further payload, and a .NET executable that loads an AsyncRAT client.
- The Rust stager’s next-stage payload was unknown; the implants displayed a message mimicking a portal update.
- Researchers assessed the activity as involving suspected China- and India-aligned actors, citing malware use, infrastructure overlaps and victimology.
Article Details
- Attack Vectors
- Compromised the Balochistan Police Complaint Management System and uploaded implant variants disguised as a portal update.
- A Rust stager downloaded and executed an additional payload from an external IP address.
- A .NET executable masquerading as 360Safe.exe reflectively loaded an assembly implementing an AsyncRAT client.
- Used law-enforcement-themed lures with a decoy document purporting to contain an operational plan.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 142[.]171[.]183[.]8 | Attacker-controlled C2 server associated with the Cobalt Strike activity cluster. |
| IPV4 | 193[.]42[.]25[.]65 | Payload-download address used by the Rust stager uploaded to the compromised Complaint Management System. |
MITRE ATT&CK
T1036 · MasqueradingA .NET executable masquerades as the legitimate 360Safe.exe binary to load an AsyncRAT client.T1105 · Ingress Tool TransferThe Rust stager downloads an additional payload from 193.42.25[.]65.T1584.004 · ServerThe activity compromised a police web application and used it to host malware implants.T1620 · Reflective Code LoadingThe .NET executable reflectively loads an assembly implementing an AsyncRAT client.
People
Threat Actors
APT-C-08Named by the source as an alias of Mysterious Elephant, which is assessed to share infrastructure and tactical overlaps with the Remcos-related intrusion set.APT-K-47Named by the source as an alias of Mysterious Elephant, which is assessed to share infrastructure and tactical overlaps with the Remcos-related intrusion set.BitterThe source reports commonalities between this India-nexus adversary and Mysterious Elephant; it does not establish Bitter's responsibility for the reported intrusions.ConfuciusThe source reports commonalities between this India-nexus adversary and Mysterious Elephant; it does not establish Confucius's responsibility for the reported intrusions.Mysterious ElephantA hacking group whose infrastructure and tactical overlaps with the Remcos-related intrusion set are assessed by the source; the group is also reported to have commonalities with India-nexus adversaries.SidewinderThe source reports commonalities between this India-nexus adversary and Mysterious Elephant; it does not establish SideWinder's responsibility for the reported intrusions.TAG-179Named by the source as an alias of Mysterious Elephant, which is assessed to share infrastructure and tactical overlaps with the Remcos-related intrusion set.
Malware
AsyncRATA .NET executable that masquerades as “360Safe.exe,” a legitimate binary used by Qihoo 360 Total Security, to reflectively load an assembly implementing an AsyncRAT client.PlugXPolice, Islamabad Police, and the Punjab Safe Cities Authority, using malware families such as PlugX, ShadowPad, Cobalt Strike, and Remcos RAT.Remcos RATthe Punjab Safe Cities Authority, using malware families such as PlugX, ShadowPad, Cobalt Strike, and Remcos RAT.ShadowPadPolice, Islamabad Police, and the Punjab Safe Cities Authority, using malware families such as PlugX, ShadowPad, Cobalt Strike, and Remcos RAT.
Products
Complaint Management SystemThe compromise of the Balochistan Police Complaint Management System turned a public-facing portal into a malware delivery mechanism, extending access to police and citizen data.FortiMailA Fortinet FortiMail appliance that had served as the agency’s primary inbound email gatewayQihoo 360 Total SecurityA .NET executable that masquerades as “360Safe.exe,” a legitimate binary used by Qihoo 360 Total Security, to reflectively load an assembly implementing an AsyncRAT client.
Tools
Countries
PakistanThe activity is notable because it has drawn both a “partner and an adversary of Pakistan” to the same victim for intelligence gathering, likely fueled by geopolitical motives.TaiwanAmong those targeted are Tibetan Buddhist organizations in Taiwan, which have long been targeted by China for cyber espionage.
Industries
DefensePakistani law enforcement, victimology for PlugX and ShadowPad includes government, foreign affairs, defense, nongovernmental, and research entities across South, Southeast, Central, and East Asia, the ArabianGovernment“Beyond Pakistani law enforcement, victimology for PlugX and ShadowPad includes government, foreign affairs, defense, nongovernmental, and research entities across South, Southeast, Central, and East Asia, the ArabianLaw enforcementSustained cyber espionage has targeted multiple Pakistani law enforcement organizations, including Balochistan Police, Khyber Pakhtunkhwa Police, Islamabad Police, and the Punjab Safe Cities Authority, using malwareTelecommunications(C2) server (“142.171.183[.]8”) extends beyond Pakistani law enforcement to government, academic, telecommunications, and non-governmental entities across South, East, and Southeast Asia, the Middle East, and South