
Researchers Chain VMware Guest Escape and Windows Kernel Exploits
· 42:12 · Watch on YouTube ↗
Summary
Researchers demonstrate an exploit chain that escapes a VMware Workstation guest and escalates privileges on the Windows host using information disclosure, use-after-free and kernel heap overflow vulnerabilities.
Key points
- The researchers developed the chain for a 2024 virtualization competition and demonstrated a SYSTEM shell on the host.
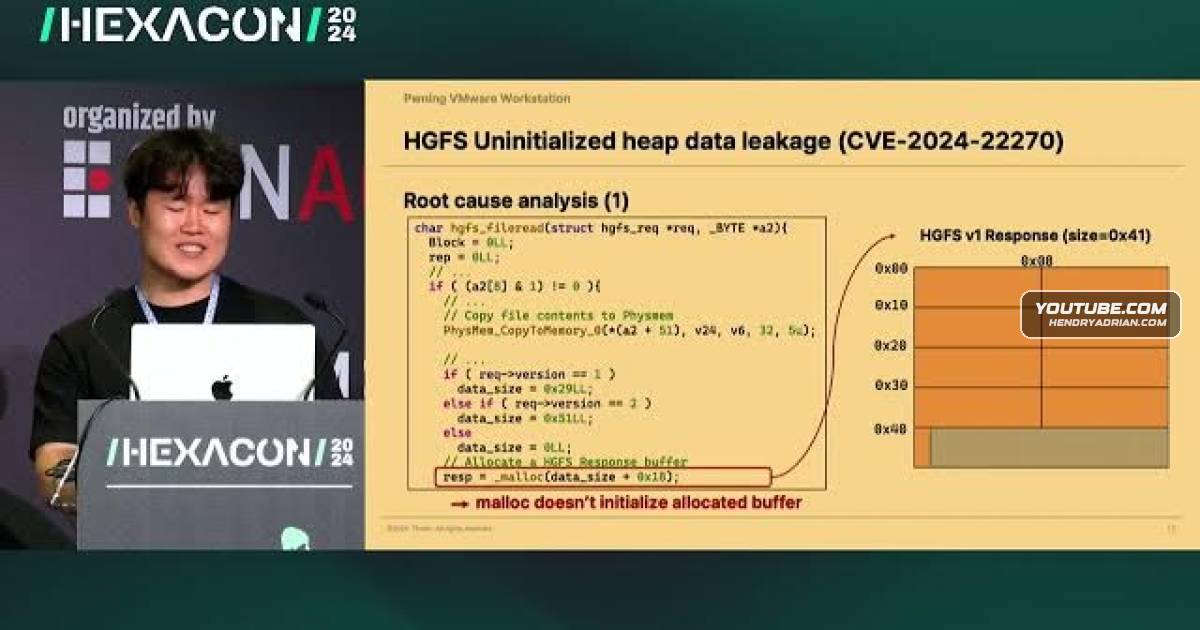
- A host-guest file-sharing flaw exposed uninitialized host heap data, allowing the researchers to recover a VMware module address.
- A use-after-free in virtual Bluetooth USB request handling enabled host code execution after the researchers bypassed Control Flow Guard.
- A Windows Cloud Filter heap overflow arose when reparse-point data was copied despite a failed length check.
- The Windows exploit used heap spraying and mailslot objects to obtain memory primitives, then manipulated a process token to escalate privileges.
- The researchers used unused guest physical memory pages to transfer the Windows exploit to the host and execute it.
Article Details
- Topics
- [01:13] Competition goals and VMware Workstation research
- [05:51] Host-guest file-sharing information disclosure
- [10:04] Virtual Bluetooth use-after-free and host code execution
- [19:29] Windows Cloud Filter heap overflow and kernel exploitation
- [38:14] Chaining the guest escape with host privilege escalation
- [40:16] Exploit demonstration