
Doommageddon Claims Upcoming Ransomware Attack on Cam Group LLC
Ransomware.live lists an upcoming Doommageddon claim against Cam Group LLC, discovered and published on Oct. 5, 2026, with a stated deadline of Oct. 15. The claim is unverified.
Ransomware.live lists an upcoming Doommageddon claim against Cam Group LLC, discovered and published on Oct. 5, 2026, with a stated deadline of Oct. 15. The claim is unverified.
Ransomware.live records an unverified Doommageddon claim of a planned operation against ENKA Schools in Turkey, marked upcoming with a deadline of October 15, 2026.

The BYOD ransomware group claims it stole about 300,000 Royal Selangor user and customer records, including contact, purchase, and payment details. The post says the claims have not been independently confirmed.
A ransomware.live post reports BYOD’s unverified claim that Trump Mobile Wireless customer PII and telecom details for 3,615 people were exposed and made available.
The Aurora ransomware group claims it exposed Thomas Y. Pickett & Co. data, including database backups, employee records, source code, client contracts and financial documents. The claims have not been independently confirmed.
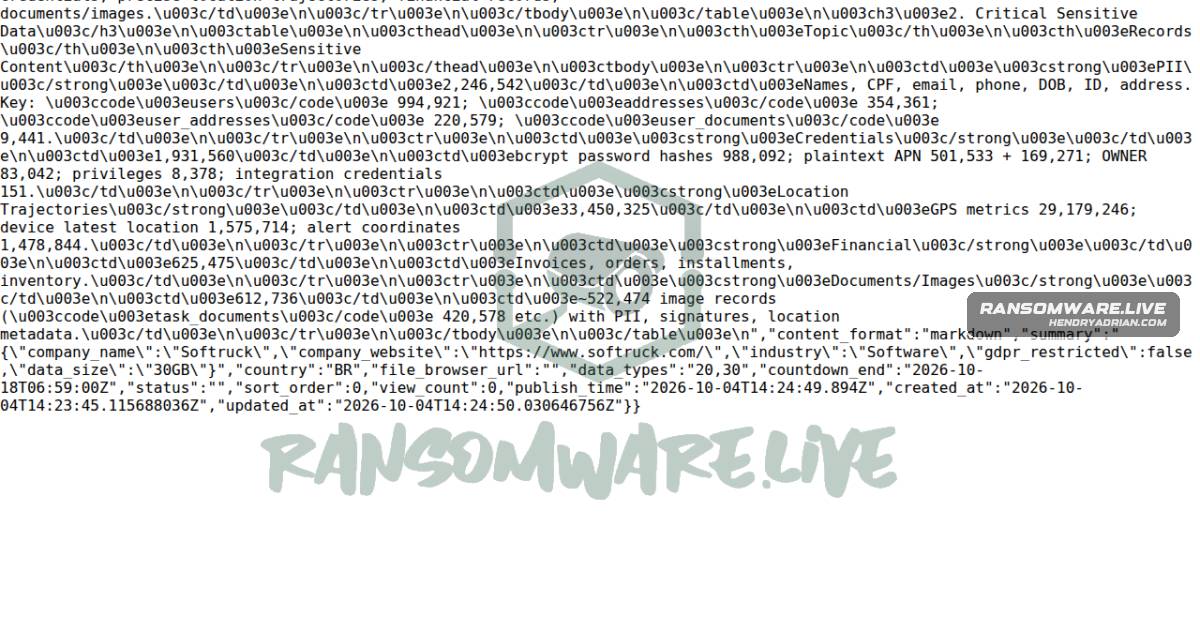
A ransomware.live monitoring post records an unverified Direwolf group claim targeting Brazilian software company Softruck. The post says malicious encryption disrupted access to business systems; the claim has not been confirmed by the company.
Ransomware.live lists Cotesma in Chile as a Qilin target, with claims of encryption and operational disruption. The site says the information is based on the group’s public claim and is unconfirmed.
Ransomware.live lists Spanish manufacturer Emser as a Qilin ransomware victim, citing the group’s public claim; the site says it cannot independently confirm the information.
Qilin claimed it targeted Australian manufacturer Chadwick Switchboards with ransomware. The claim was recorded on October 4, 2026, and has not been independently confirmed.
The Play ransomware group claims it targeted Silicon Valley Glass in the US, encrypted files and demanded payment. The monitoring post says the claim is unverified.
Ransomware.live reported a Play group claim targeting Bold Spring Nursery in the US. The post alleges encrypted files and disrupted data access, but says the claims have not been independently confirmed.
Ransomware.live reports that Qilin claimed an attack on Unident Group in the US, alleging data encryption and exposure. The post says the claim is unverified.
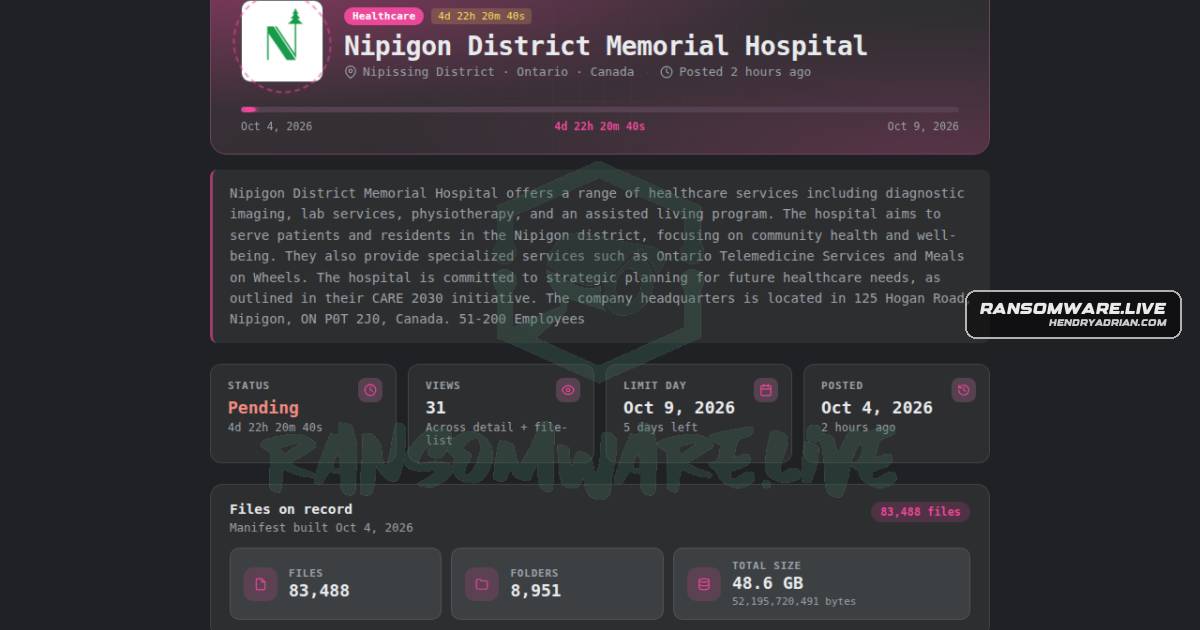
Storm reportedly targeted Nipigon District Memorial Hospital, allegedly disrupting healthcare services. The post is based on the ransomware group’s public claim, which the publisher says it cannot confirm.
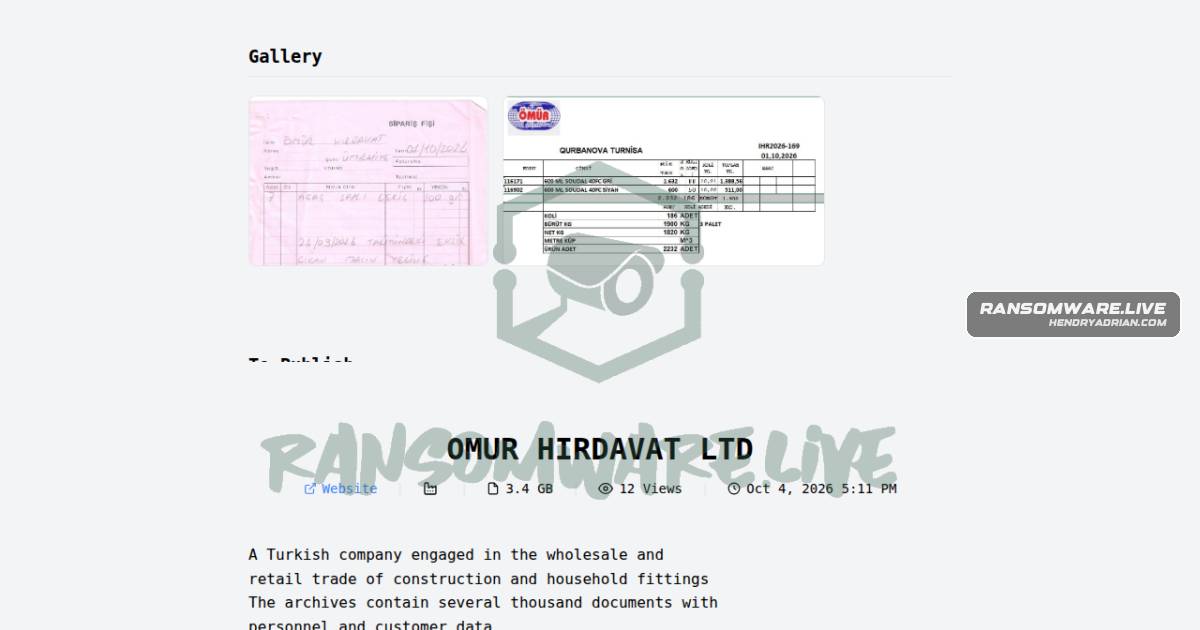
Ransomware group emperador claims it encrypted files at Turkish company OMUR HIRDAVAT LTD and demanded a ransom. The group alleges its archives contain thousands of personnel and customer documents; the claims are unverified.
Ransomware.live reports that Booba Project claimed to have stolen 344 GB of data from MorseLife Health System. The post says the claim is unconfirmed.
A ransomware.live record says thegentlemen claimed Westrop Primary & Nursery School as a victim. The post gives publication and discovery dates but says the claim is unverified.
A ransomware group identified as thegentlemen claimed it targeted Mandurah State Emergency Service in Australia. The monitoring post says the claim is unverified.
The ransomware group thegentlemen reportedly claimed Rotamac, a Canadian industrial equipment distributor, as a victim. The post says operations were affected but notes the claim is unverified.
Ransomware group thegentlemen claimed an incident involving Barcelona’s Hospital de la Santa Creu i Sant Pau. The claim was recorded by ransomware[.]live; the article says it could not be independently confirmed.
Ransomware.live records thegentlemen’s claim that it targeted Zelham, a U.S. hospitality renovation contractor. The post says the claim is unverified.
Storm claims it targeted Step By Step, a Pennsylvania nonprofit providing disability and behavioral health services, and disrupted its programs. The post says the group’s claims are unconfirmed.
Thegentlemen claimed a ransomware incident affecting South Korea’s WOOSHIN SAFETY SYSTEMS and its wooshinsys[.]co[.]kr assets. The monitoring post says the claim is unverified.
A ransomware.live monitoring post records Storm’s claim naming Allied Machine & Engineering, a U.S. manufacturer, as a victim. The post says the claim is unconfirmed.
Ransomware group Wallstreet claims it compromised the Saudi consortium building Jeddah Central Stadium and exfiltrated 17 TB of files, including employee data. The claims are unverified.