
Play Ransomware Group Claims Attack on Silicon Valley Glass
Summary
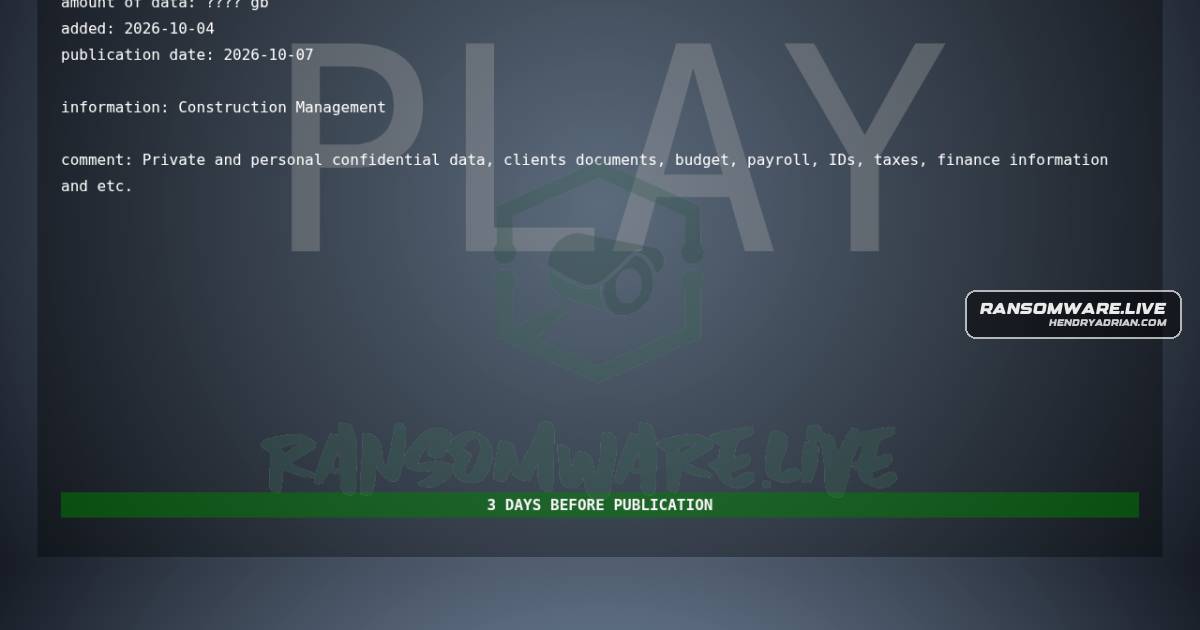
The Play ransomware group claims it targeted Silicon Valley Glass in the US, encrypted files and demanded payment. The monitoring post says the claim is unverified.
Key points
- The named victim is Silicon Valley Glass, a US manufacturing company.
- The Play group claims it encrypted files and demanded payment for decryption.
- The post attributes the claim to a Play leak-site source: hxxp://ipi4tiumgzjsym6pyuzrfqrtwskokxokqannmd6sa24shvr7x5kxdvqd[.]onion/topic.php?id=BkyYiTWXAe9Xf3.
- The claim was recorded on October 4, 2026.
- The monitoring post says it cannot confirm the claim's accuracy.
Article Details
- Victim
- Silicon Valley Glass
- Encryption Status
- Reported in the post but unconfirmed; the source states it cannot verify the group's claims.
- Exfiltration Status
- Potential data compromise is mentioned, but exfiltration is not confirmed.
- Ransom Demand
- The post says payment was demanded for decryption, but gives no amount; the claim is unconfirmed.
- Leak Status
- The post reports a ransomware-group claim; it does not establish that data was published.