
Emperador Claims Ransomware Attack on Turkish Firm OMUR HIRDAVAT LTD
Summary
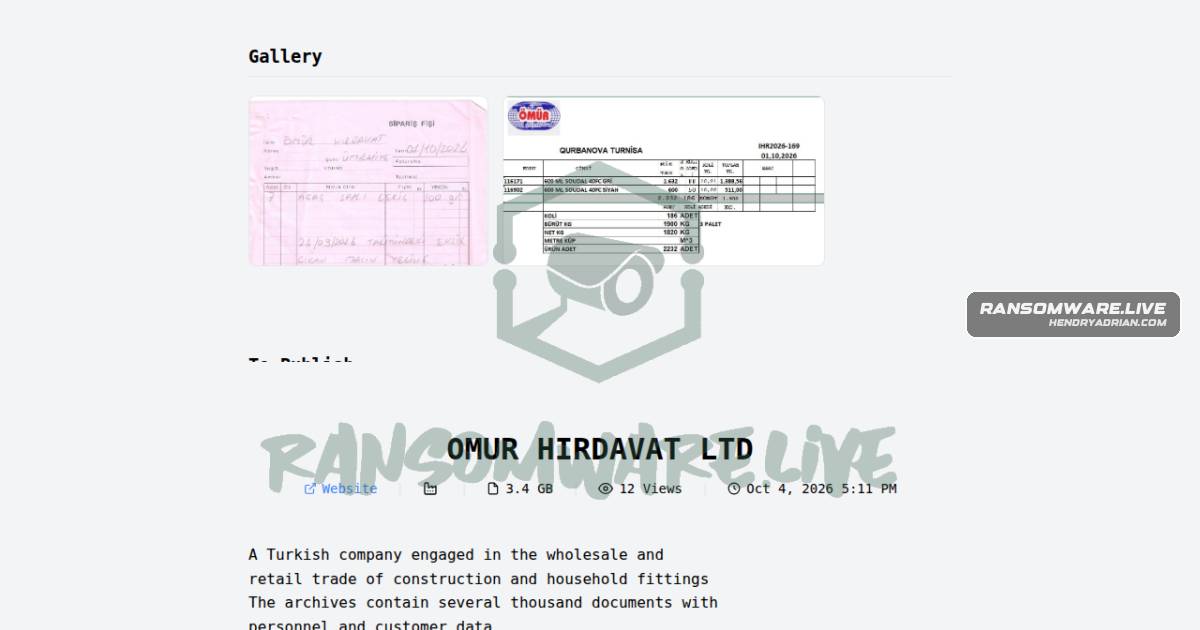
Ransomware group emperador claims it encrypted files at Turkish company OMUR HIRDAVAT LTD and demanded a ransom. The group alleges its archives contain thousands of personnel and customer documents; the claims are unverified.
Key points
- The monitoring record names Turkish company OMUR HIRDAVAT LTD as the alleged victim and emperador as the actor.
- The group claims it encrypted files and demanded a ransom.
- The group alleges its archives contain several thousand documents with personnel and customer data.
- The source attributes the claims to a post at hxxp://emprdr4p7iwlhpky33tswt3k2qdeljyjcdpoysabudmmrz4z32laexad[.]onion/post/omur-hirdavat-ltd/.
- The monitoring source says it cannot confirm the claims.
Article Details
- Victim
- OMUR HIRDAVAT LTD
- Claim Date
- 2026-10-04
- Encryption Status
- Reported by the ransomware group; unverified by the source.
- Exfiltration Status
- Unverified; the source reports that the group's post described archives containing documents, but does not confirm exfiltration.
- Exfiltrated Data
- The post reportedly described documents containing personnel and customer data.
- Exfiltrated Size
- Several thousand documents, according to the report; unverified. This is a document count, not a data-volume measurement.
- Ransom Demand
- A ransom demand is reported, but no amount is provided; unverified.
- Leak Status
- The group post is linked, but publication or authenticity of leaked data is not confirmed.