Metaencryptor Claims Attack on Bruker Corporation
Summary
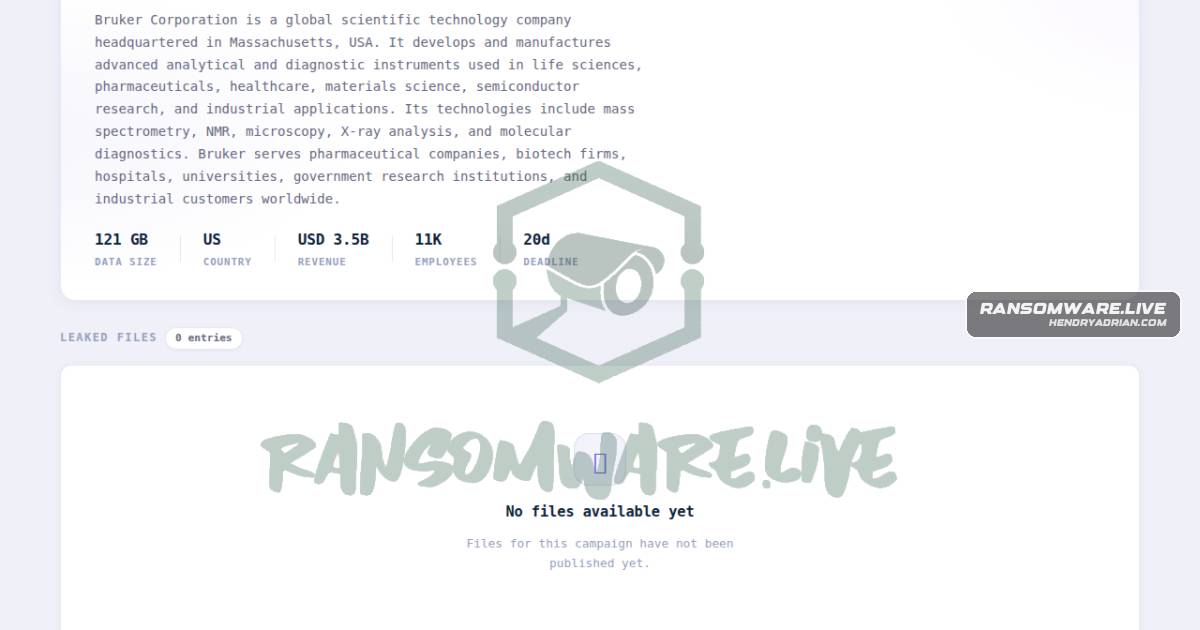
A ransomware.live post attributes an alleged attack on Bruker Corporation to metaencryptor. The post says the group’s claim cannot be independently confirmed.
Key points
- The post identifies Bruker Corporation, a US scientific technology company, as the alleged victim.
- The claim is attributed to the ransomware group metaencryptor and its leak-site source.
- The post lists the claim as discovered and published on September 21, 2026.
- The post provides no specific details about stolen data, encryption, or operational disruption.
- The publisher says it cannot confirm the group’s claims and invites an official statement from Bruker.
Article Details
- Victim
- Bruker Corporation
- Claim Date
- 2026-09-21
- Encryption Status
- Unknown
- Exfiltration Status
- Unknown
- Leak Status
- The ransomware group reportedly posted a claim; the source says it cannot confirm the claim's accuracy.