OAuth Device Code Phishing Campaigns Use Microsoft Login Flow to Steal Tokens
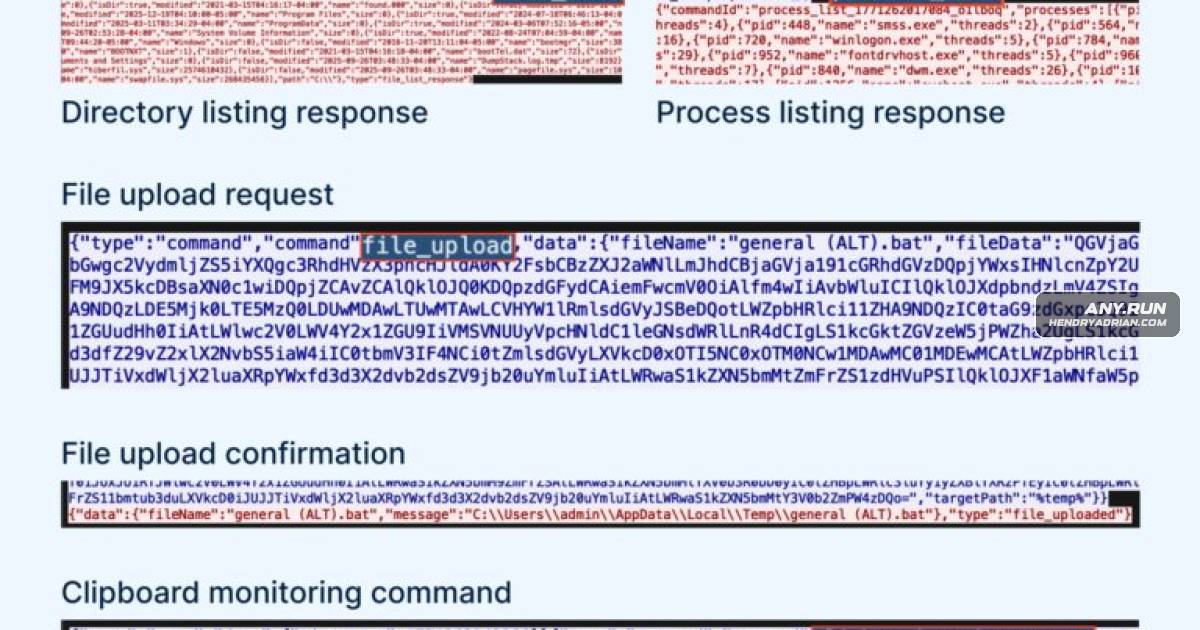
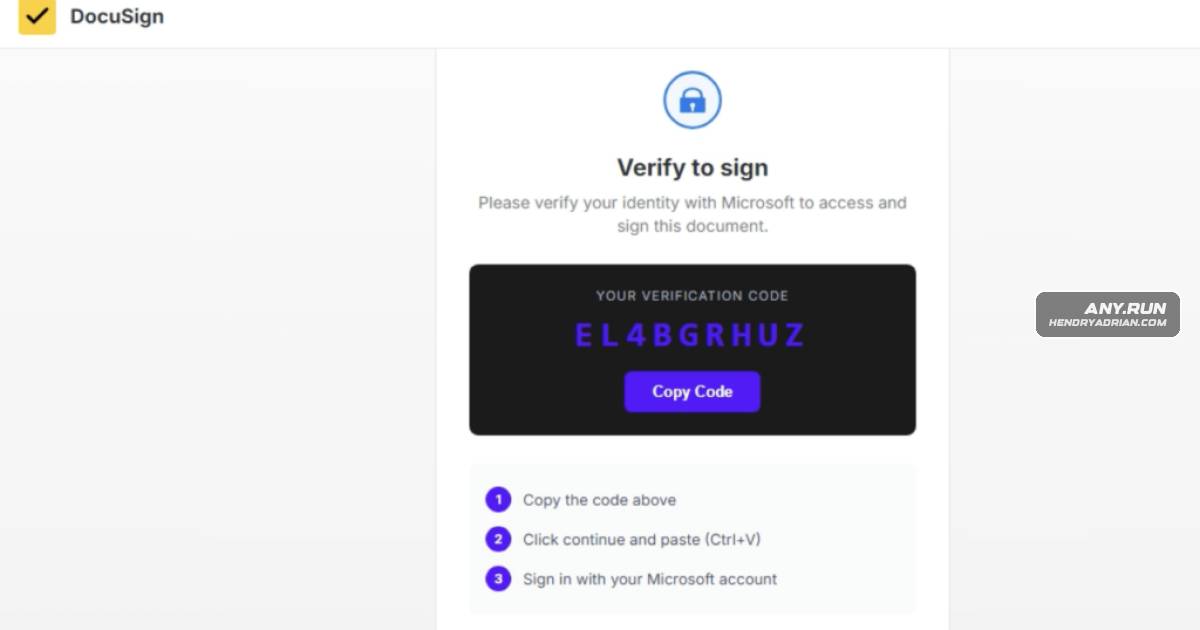
ANY.RUN analysts report more than 180 URLs in a week abusing Microsoft OAuth device authorization: victims enter attacker-generated codes on legitimate Microsoft pages, granting attackers tokens. The article describes SSL decryption exposing campaign scripts and network