
ANY.RUN Details Moonrise RAT’s WebSocket C2 and Remote-Control Capabilities
Summary
ANY.RUN reports sandbox analysis of Moonrise, a Go-based RAT, observed WebSocket-like C2 and operator interaction. It says the sample had no VirusTotal detection at the time and describes credential-theft, surveillance and persistence capabilities, with behavior-based T
Key points
- ANY.RUN reports that its sandbox analysis found Moonrise, a Go-based RAT, had no VirusTotal detection at the time of analysis.
- The analysis observed WebSocket-like C2 using client_hello, connected, and ping/pong messages before operator interaction.
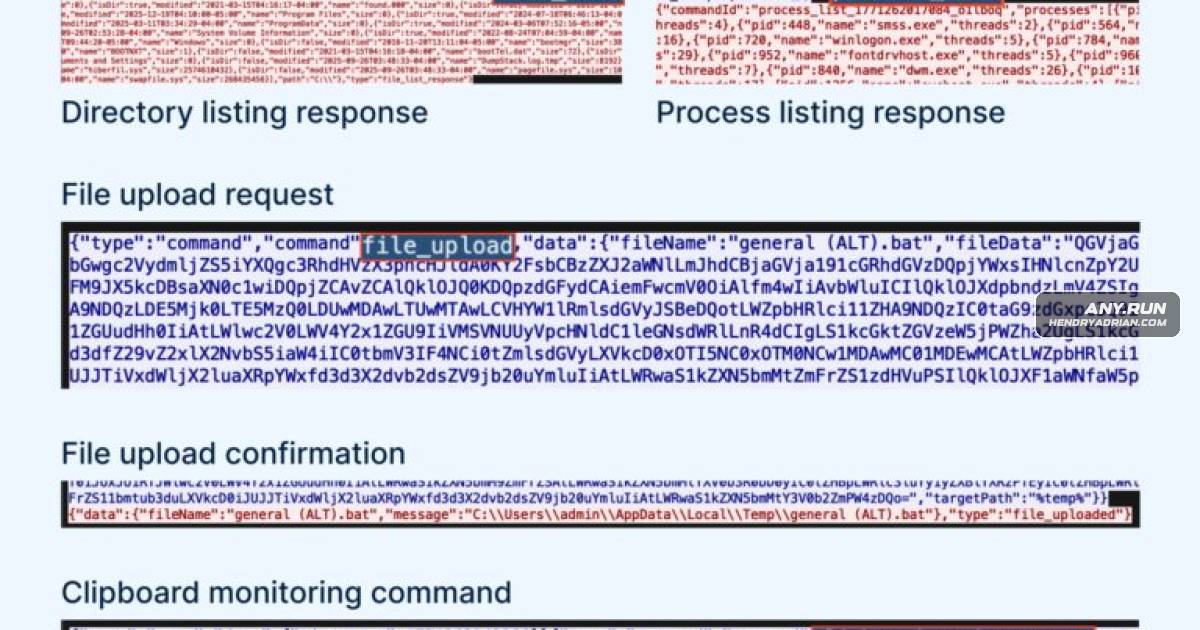
- Observed commands included process and file discovery, process termination, file upload, and remote execution.
- The sample’s command set includes credential and clipboard collection, keylogging, screen capture, and webcam and microphone access.
- Commands for UAC bypass, rootkit operations, watchdog and protection configuration suggest privilege-manipulation and persistence capabilities; the article notes not all commands were triggered in every session.
- ANY.RUN recommends monitoring new infrastructure, enriching indicators and sandboxing suspicious artifacts, then hunting for related infrastructure and samples.
Article Details
- Attack Vectors
- Moonrise is a Go-based RAT that establishes persistent WebSocket-like C2 communication and accepts operator-driven commands.
- The RAT supports remote command execution, process manipulation, file upload and execution, credential and clipboard theft, keylogging, and screen, webcam, and microphone monitoring.
- The sample includes commands associated with UAC bypass, rootkit functions, watchdog behavior, and protection configuration; the article notes that not all commands may be triggered in every session.
- Defensive Notes
- Do not rely on static reputation checks alone; use behavior-based analysis to identify active C2 and confirm malware behavior.
- Monitor for newly observed infrastructure and suspicious traffic that differs from established baselines.
- Enrich indicators, execute suspicious artifacts in a sandbox for behavioral confirmation, then use confirmed indicators to hunt for related infrastructure and samples.
- The article recommends rapid triage and containment to reduce the time available for credential theft, persistence, and further payload deployment.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 193[.]23[.]199[.]88 | C2 IP address observed in the Moonrise attack. |
| SHA256 | 082fdd964976afa6f9c5d8239f74990b24df3dfa0c95329c6e9f75d33681b9f4 | Hash listed among the Moonrise indicators of compromise. |
| SHA256 | 7609c7ab10f9ecc08824db6e3c3fa5cbdd0dff2555276e216abe9eebfb80f59b | Hash listed among the Moonrise indicators of compromise. |
| SHA256 | 8a422b8c4c6f9a183848f8d3d95ace69abb870549b593c080946eaed9e5457ad | Hash identified in the article as a Moonrise malware sample. |
| SHA256 | 8d7c1bbdb6a8bf074db7fc1185ffd59af0faffb08e0eb46a373c948147787268 | Hash listed among the Moonrise indicators of compromise. |
| SHA256 | c7fd265b23b2255729eed688a211f8c3bd2192834c00e4959d1f17a0b697cd5e | Hash identified in the article as a Moonrise malware sample. |
| SHA256 | ed5471d42bef6b32253e9c1aba49b01b8282fd096ad0957abcf1a1e27e8f7551 | Hash listed among the Moonrise indicators of compromise. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe article describes collected files, keylogger logs, and clipboard contents being transferred through the established C2 channel.T1056 · Input CaptureMoonrise includes keylogging and clipboard-monitoring commands that can collect user input and sensitive clipboard contents.T1057 · Process DiscoveryThe process_list command enumerates running processes.T1059 · Command and Scripting InterpreterThe RAT supports remote command execution; the article observed svchost.exe spawning cmd.exe to execute system commands.T1071 · Application Layer ProtocolMoonrise maintains C2 over WebSocket-like messaging, including client_hello, connected, and ping/pong messages.T1083 · File and Directory DiscoveryThe file_list command lets the operator inspect directory structures.T1105 · Ingress Tool TransferOperator-driven file_upload and file_download commands allow files or additional payloads to be transferred.T1113 · Screen CaptureThe RAT attempts screenshots and supports screen streaming through screen_stream_start and screen_stream_stop.T1123 · Audio CaptureThe microphone_record command supports capturing audio from the infected endpoint.T1547 · Boot or Logon Autostart ExecutionThe article reports persistence-related functions and commands, including watchdog and protection configurations, that can help maintain the infection.T1548 · Abuse Elevation Control MechanismThe sample includes a uac_bypass command, described as a privilege-manipulation capability.
Malware
Vendors
Products
ANY.RUN SandboxMoonrise RAT detected inside ANY.RUN sandbox, revealing its full attack chainANY.RUN Threat Intelligence Feeds (TI Feeds)This is where ANY.RUN’s Threat Intelligence Feeds help.ANY.RUN Threat Intelligence Lookup (TI Lookup)Use Threat Intelligence Lookup to pull immediate context around a hash, URL, domain, or IP (relationships, related samples, historical sightings).