
Vertex AI SDK Flaw Let Attackers Hijack Model Uploads Through Bucket Squatting
Summary
Unit 42 found that predictable staging-bucket names in the Vertex AI Python SDK let attackers replace uploaded models and execute code in serving containers. Google fixed the flaw in version 1.148.0; Unit 42 reported no in-the-wild exploitation.
Key points
- When staging_bucket was unset, the SDK used a predictable temporary Cloud Storage bucket name based on the project ID and region, without verifying bucket ownership.
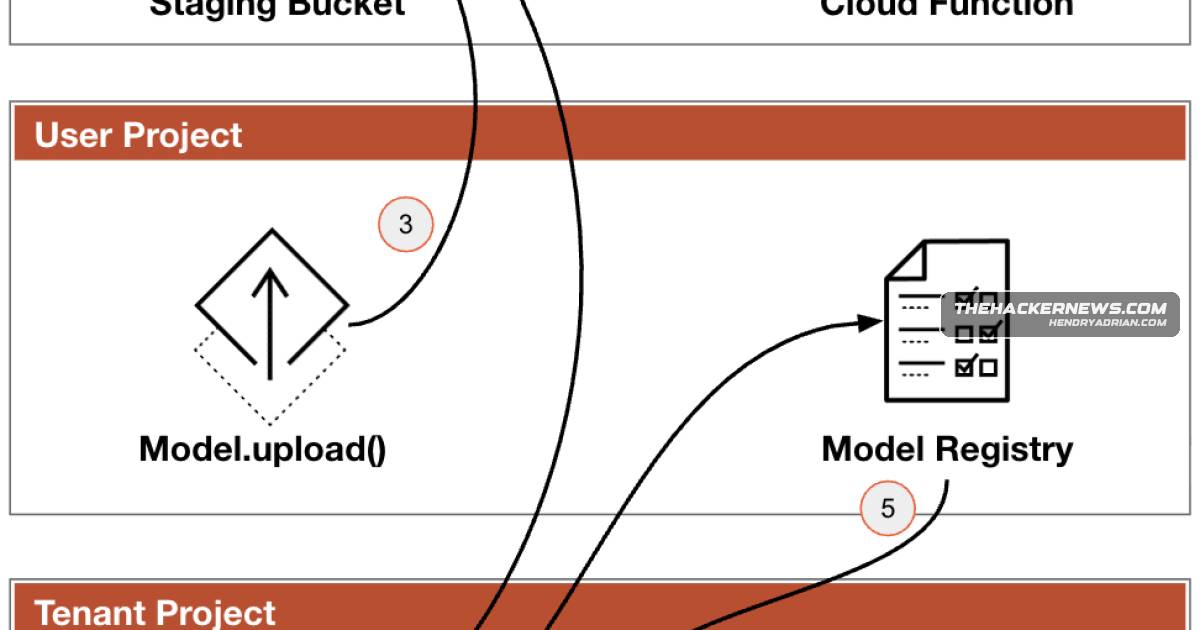
- An attacker could create the expected bucket first, intercept a victim's model upload, and replace the model with a malicious pickle or joblib file.
- When Vertex AI loaded the substituted model, its code could execute in the serving container; Unit 42's proof of concept replaced the model within the roughly 2.5-second upload-to-read window.
- In Unit 42's test environment, the payload stole an OAuth token that could access other model artifacts and tenant data in the Google-managed project.
- The attack required the default staging bucket not to exist in that region and the victim to leave staging_bucket unset.
- Google added a random UUID to bucket names in version 1.144.0 and added bucket ownership verification in version 1.148.0; Unit 42 reported no exploitation in the wild.
- Users should update to version 1.148.0 or later and set an explicit staging bucket they control.
Article Details
- Vulnerability Types
- Predictable Cloud Storage bucket naming with no bucket ownership verification (bucket squatting)
- Model substitution enabling code execution when malicious pickle or joblib files are loaded
- Affected Versions
- google-cloud-aiplatform 1.139.0
- google-cloud-aiplatform 1.140.0
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Set an explicit staging_bucket to a Cloud Storage location you control.
MITRE ATT&CK
CVE
Vendors
Products
Google Cloud StorageA flaw in the Google Cloud Vertex AI SDK for Python let attackers hijack model uploads by squatting on predictable Cloud Storage bucket names and swapping in malicious pickle or joblib models.google-cloud-aiplatformGoogle fixed the issue in google-cloud-aiplatform 1.148.0 and added bucket ownership verification.Vertex AIA flaw in the Google Cloud Vertex AI SDK for Python let attackers hijack model uploads by squatting on predictable Cloud Storage bucket names and swapping in malicious pickle or joblib models.