Atlassian Data Center Flaw Exploited Within Two Hours of Public Technical Details
Summary
Attackers have targeted CVE-2026-21589, a critical unauthenticated file-access flaw in Atlassian Data Center products. Honeypots recorded attempts within two hours of public technical details; no use of obtained credentials has been observed.
Key points
- CVE-2026-21589 has a CVSS score of 9.3 and affects several Atlassian Data Center products, including Bitbucket, Confluence, Jira, Bamboo, Crowd, Crucible, and Fisheye.
- The unauthenticated flaw can expose specific files within an affected application's web root when an attacker knows the exact file name and path; it does not allow directory listing.
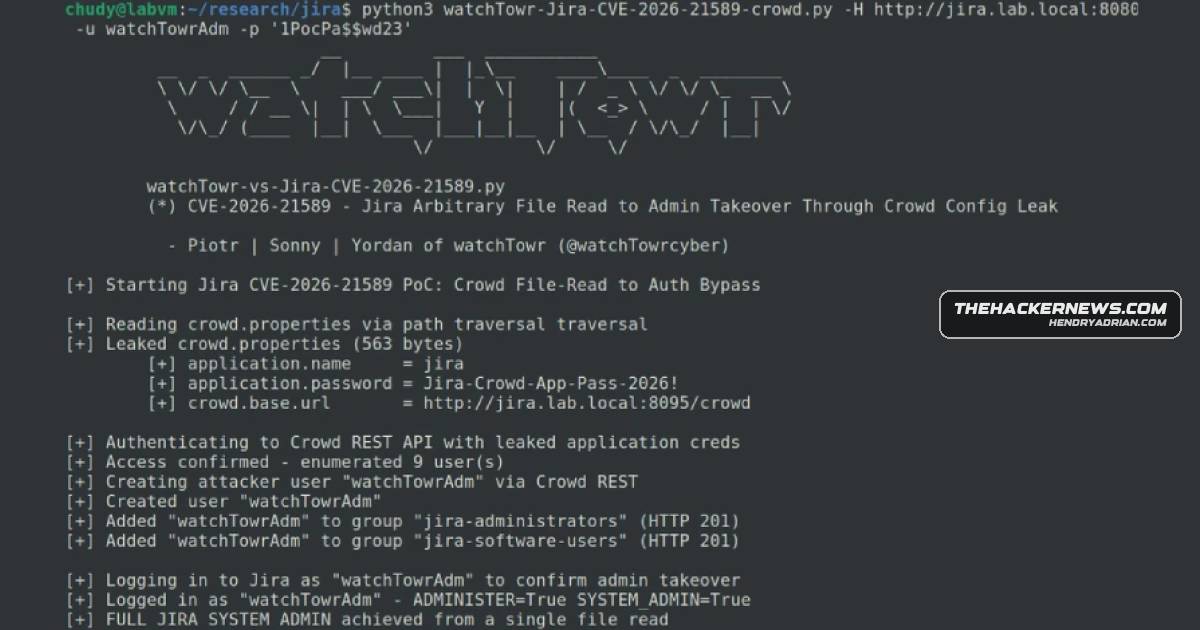
- The vulnerability stems from web-resource path resolution and can potentially expose sensitive files, including Crowd credentials in Crowd and Jira.
- Previdian reported 15 attempts from three IP addresses in Japan and the U.S., beginning within two hours of public technical details being released.
- Atlassian Cloud products have been patched. Atlassian recommends patching affected Data Center products and offers temporary mitigations, including restricting public access and applying product-specific request-blocking rules.
- WatchTowr reported exploitation attempts focused on fingerprinting and searching for sensitive files; it had not observed attackers using obtained credentials or other post-compromise activity.
Article Details
- Vulnerability Types
- Arbitrary file access
- Severity
- Critical; CVSS 9.3
- Exploitation Status
- active
- Exploit Availability
- public_exploit
- Patch Status
- available
- Workarounds
- Remove the affected instance from the public internet.
- Apply a Web Application Firewall (WAF) rule.
- For Confluence, Jira Service Management, Jira Software, Bamboo, and Crowd, block requests using Tomcat's RewriteValve.
- For Bitbucket, add a new rule to urlrewrite.xml.
CVE
People
Jake KnottwatchTowr's head of threat intelligence; reported that observed attempts focused on fingerprinting affected products and searching for configuration files and sensitive information.Ryan DewhurstPrevidian Founder and CEO; said exploitation attempts reached Previdian's honeypot network within two hours of public exploit details becoming available.
Vendors
Products
Atlassian CloudAtlassian said impacted Atlassian Cloud products have been patched, adding that fixes are available for the following products -Bamboo Data CenterCenter, Confluence Data Center, Jira Service Management Data Center, Jira Software Data Center, Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye.Bitbucket Data Centeraccess flaw, tracked as CVE-2026-21589 (CVSS score: 9.3) affects multiple products, including Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software Data Center, BambooConfluence Data Centeras CVE-2026-21589 (CVSS score: 9.3) affects multiple products, including Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software Data Center, Bamboo Data Center, Crowd DataCrowd Data CenterData Center, Jira Service Management Data Center, Jira Software Data Center, Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye.CrucibleJira Service Management Data Center, Jira Software Data Center, Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye.FisheyeManagement Data Center, Jira Software Data Center, Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye.Jira Service Management Data Center9.3) affects multiple products, including Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software Data Center, Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye.Jira Software Data Centerincluding Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software Data Center, Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye.