
Brotli Flaw Affects Node.js, Bun, Python Packages and Envoy; RCE Shown on One Node.js Build
Summary
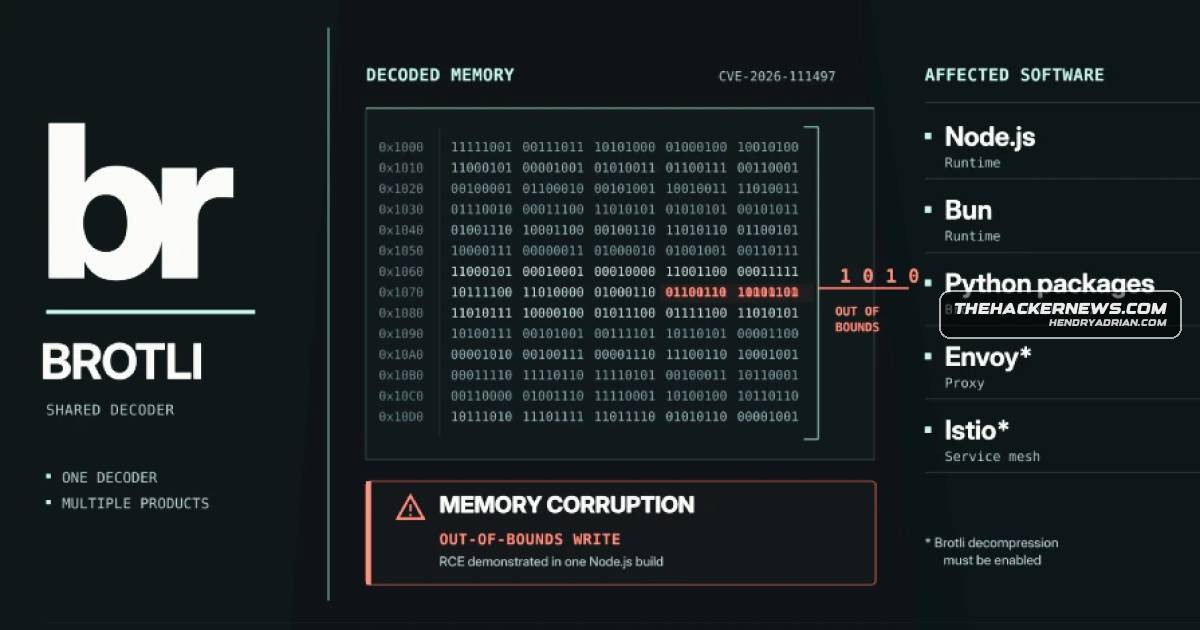
CVE-2026-111497 is a Brotli decoder memory-corruption flaw affecting multiple runtimes, packages, and proxies. Code execution was demonstrated on one unpatched Node.js build; no real-world exploitation has been reported.
Key points
- Crafted Brotli data can overwrite memory past a buffer boundary, potentially causing a crash, memory leak, or attacker-controlled code execution.
- Imperva demonstrated code execution on an unpatched Node.js 24.22.0 build for Linux ARM64. The exploit was not tested on other builds and has not been released.
- Bun, Python's Brotli and brotlicffi packages, and Envoy are among the affected software; Envoy and Istio are exposed only when Brotli decompression is enabled.
- Exposure requires decoding Brotli data controlled by someone else. Python HTTP clients may decode Brotli responses automatically when either affected package is installed.
- Fixes have shipped product by product because each program includes its own copy of the decoder. Update the affected runtime or library, then restart services and rebuild container images.
- Where updates are not possible, stop decoding untrusted Brotli. Removing br from Accept-Encoding alone does not prevent a server from sending Brotli.
- No real-world exploitation has been reported; CISA's October 23 assessment listed exploitation as none.
Article Details
- Vulnerability Types
- Memory corruption from an out-of-bounds write when processing crafted Brotli-compressed data
- Severity
- Google rated it 9.2 (critical) on CVSS 4.0; Node.js rated it high; Red Hat rated it 8.1 (important).
- Affected Versions
- Node.js 24.22.0 (Linux on ARM64)
- Exploitation Status
- not_reported
- Exploit Availability
- claimed_or_private
- Patch Status
- partial
- Workarounds
- Stop decoding untrusted Brotli data or disable Brotli decompression where possible.
- For Node.js, no workaround has been published; updating the runtime is the only fix.
CVE
People
Vendors
Products
BrotliA memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, the Python Brotli and brotlicffi packages, and Envoy proxies set up to decompress Brotli.brotlicffiA memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, the Python Brotli and brotlicffi packages, and Envoy proxies set up to decompress Brotli.BunA memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, the Python Brotli and brotlicffi packages, and Envoy proxies set up to decompress Brotli.EnvoyA memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, the Python Brotli and brotlicffi packages, and Envoy proxies set up to decompress Brotli.IstioEnvoy and Istio are affected only when Brotli decompression is enabled, for example, through an Envoy filter. Where it is off, the flaw cannot be reached.Node.jsImperva researchers have shown that code can run on one unpatched Node.js build. The same has not been demonstrated on the other software, and no real-world attacks have been reported.Python BrotliA memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, the Python Brotli and brotlicffi packages, and Envoy proxies set up to decompress Brotli.