cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Report

Collection of cybersecurity reports, surveys, research papers, market studies, and industry intelligence.

725 articles

Security Report · censys.com

Censys Report Highlights Internet Exposure Blind Spots in AI, ICS and Legacy Software

Censys’ 2026 report finds growing exposure of AI-related tools, persistent ICS and legacy software exposure, and widespread use of non-standard service ports—visibility gaps that can hinder security programs.

Oct 14, 2026
Security Report · infostealers.com

2026 Infostealer Index Ranks 34 Threat Intelligence Vendors

A summary of the 2026 Hudson Rock Infostealer Index ranks 34 vendors across nine criteria. Hudson Rock leads with 96.2 points, followed by Flare and SpyCloud; the article says infostealer specialists generally outperform broad CTI platforms.

Oct 14, 2026
Security Report · cyfirma.com

CYFIRMA Report Maps Cyber Threats Facing India and SAARC Telecom Sector

CYFIRMA’s April–September 2026 assessment describes telecom risks across India and SAARC, including exposed infrastructure, credential compromise, ransomware, data claims and APT threats. It recommends stronger vulnerability, identity and network defenses.

Oct 14, 2026
Security Report · varonis.com

IBM 2026 Breach Report Finds AI Attacks Rising and Access Controls Lacking

IBM's 2026 breach-cost study, based on 602 organizations, reports a $4.99 million average breach cost. AI-driven attacks rose 56%, while 92% of AI-related breaches involved no proper AI access controls.

Oct 14, 2026
Security Report · darkreading.com

Survey Reports Physical Threats by Ransomware Groups, but Claims Remain Unverified

Semperis's 2026 survey found that some organizations reported physical threats and intimidation tied to ransomware, but the claims were unverified. Dark Reading found no documented case of violence carried out for a ransomware attack.

Oct 14, 2026
Security Report · acronis.com

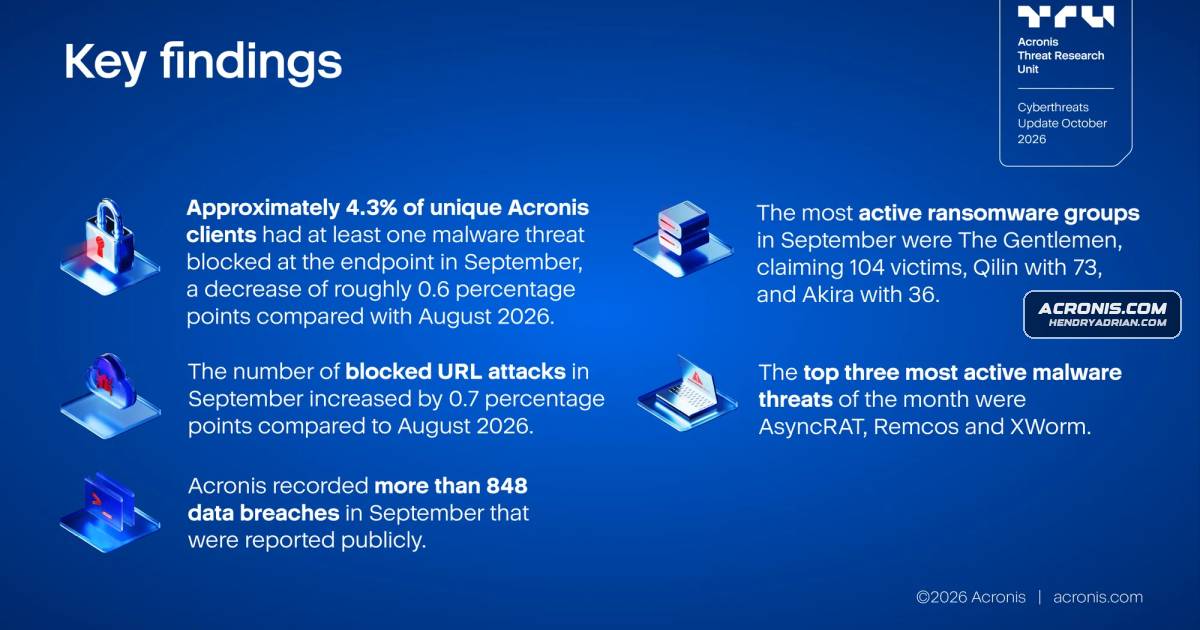
Acronis September 2026 Threat Report Finds BlueMoon Zero-Day Kit Used by Four Espionage Groups

Acronis’s September 2026 report says four espionage groups used the BlueMoon kit, which chained three Chrome and Windows zero-days. Endpoint malware detections fell to 4.3%, while URL-based threats rose in most focus countries.

Oct 13, 2026
Security Report · recordedfuture.com

Recorded Future Reports 94 High-Impact Vulnerabilities in September 2026, Including 80 Actively Exploited

Recorded Future identified 94 high-impact vulnerabilities in September 2026; 80 were actively exploited or weaponized. The report highlights zero-days, AI-assisted campaigns, and exploitation leading to credential theft, backdoors, data theft, and ransomware.

Oct 13, 2026
Security Report · cyfirma.com

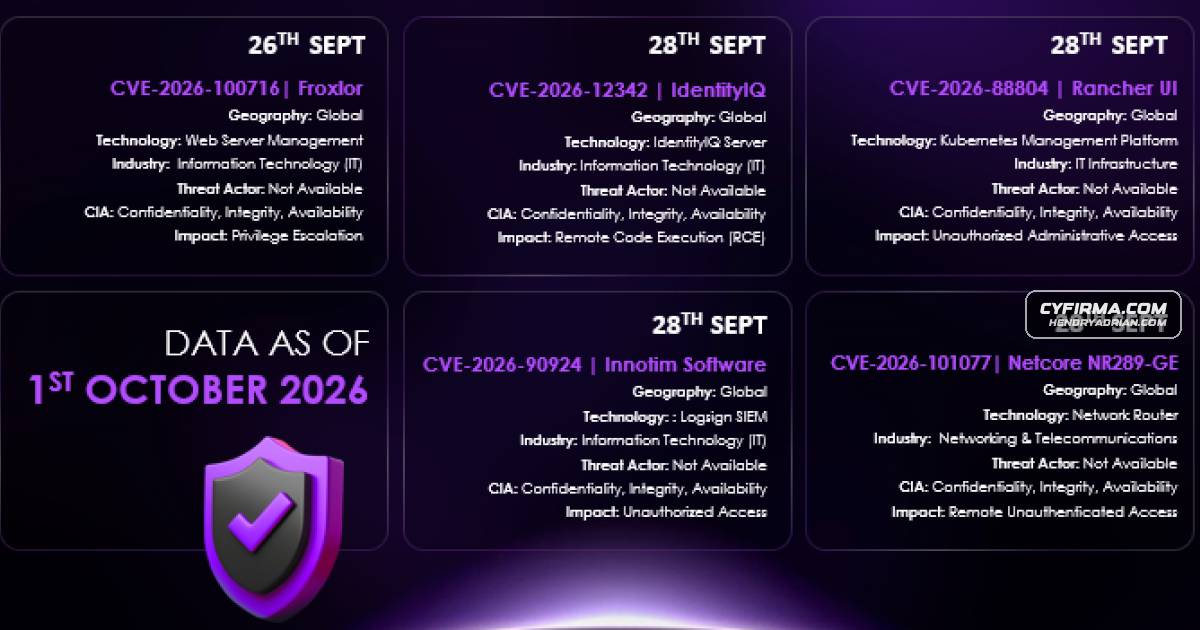
CYFIRMA Flags Five Critical Vulnerabilities in Fortnightly Exploit Radar

CYFIRMA's fortnightly roundup lists five critical vulnerabilities affecting Froxlor, IdentityIQ, Rancher, Logsign SIEM, and Netcore NR289-GE, with affected versions, fixes or workarounds, and remediation priorities.

Oct 12, 2026
Security Report · cyfirma.com

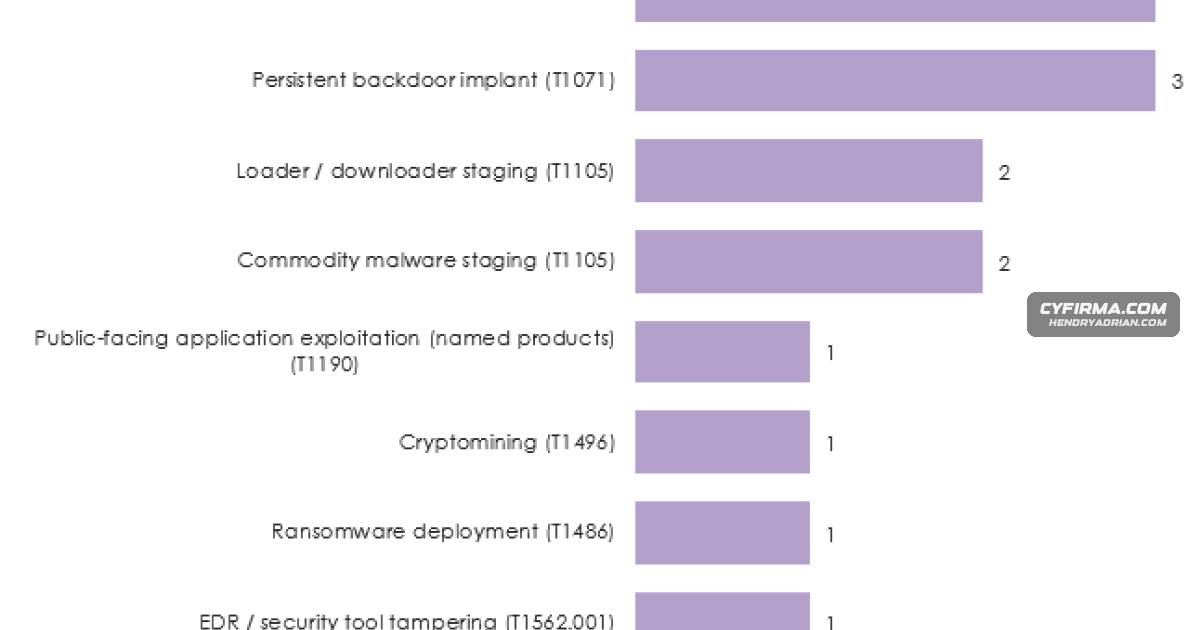
CYFIRMA Q3 2026 Report Tracks 48 APT Campaigns, Persistent Backdoors and Edge-Device Exploitation

CYFIRMA’s Q3 2026 report tracks 48 campaigns linked to four threat-actor nexuses, highlighting persistent backdoors, edge-device exploitation, overlapping attribution, and recommended patching and access controls.

Oct 12, 2026
Security Report · cyfirma.com

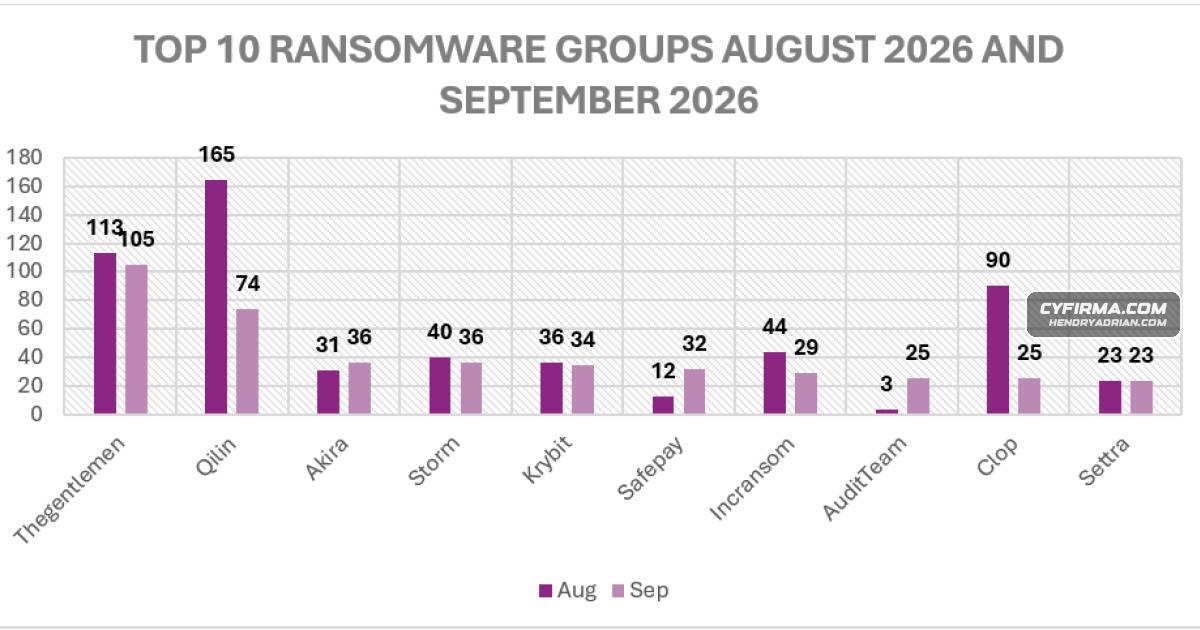
Ransomware Disclosures Fell to 862 in September as Affiliates Continued Evolving Their Tactics

CYFIRMA recorded 862 ransomware victim postings in September, down 26.3% from August. Its monthly report highlights shared affiliate toolchains, RMM and tunnel abuse, cloud data theft, BYOVD, and attacks on recovery and cloud systems.

Oct 12, 2026
Security Report · asec.ahnlab.com

AhnLab Reports September 2026 Threat Trends in the Financial Sector

AhnLab’s September 2026 review highlights phishing and downloader activity, Telegram-based theft of financial-sector credentials, and dark-web data-leak and ransomware claims involving financial organizations.

Oct 11, 2026
Security Report · asec.ahnlab.com

AhnLab’s September 2026 Ransomware Report Details Group Activity and Victim Trends

AhnLab’s September 2026 report summarizes ransomware activity, including 470 incidents attributed to the top 10 groups, affected sectors and regions, new groups, and several officially announced disruptions in Japan.

Oct 11, 2026
Security Report · cyfirma.com

CYFIRMA Report Finds Sustained Cyber Threats Across Government and Civic Organizations

CYFIRMA’s Q2 2026 government and civic report finds broad, sustained threats, including 55 APT campaign updates, 78 reported incidents, rising RCE vulnerability mentions, persistent dark-web chatter, and 142 ransomware victims.

Oct 11, 2026
Security Report · cyfirma.com

CYFIRMA Report Warns of Ransomware and Supply-Chain Risks for South Asian Manufacturing

CYFIRMA’s assessment of India and SAARC manufacturing through September 15, 2026, highlights ransomware, identity compromise, vendor access, and IT/OT exposure, and recommends stronger segmentation, access controls, and resilience.

Oct 10, 2026
Security Report · cyfirma.com

CYFIRMA Report: Persistent Espionage and Identity Attacks Target India’s Government and Defence Sector

CYFIRMA’s January–August 2026 assessment says India’s government and defence sector faced persistent cyber threats, led by nation-state espionage and identity compromise, with ransomware, supply-chain risks and AI-assisted activity also highlighted.

Oct 10, 2026
Security Report · cert-agid.gov.it

CERT-AGID Reports 178 Malicious Campaigns Targeting Italy in the Week of Oct. 3–9

CERT-AGID tracked 178 malicious campaigns affecting Italy during Oct. 3–9 and shared 1,233 indicators of compromise with accredited entities. Phishing, malware delivery, and WhatsApp account-takeover scams were among the reported threats.

Oct 9, 2026
Security Report · cyfirma.com

CYFIRMA Update Says Malware-Free, Identity-Led Intrusions Are on Track to Become the Norm

CYFIRMA's mid-year update reports that 82% of 2025 detections were malware-free and eCrime breakout averaged 29 minutes. It expects identity- and session-based intrusions without persistence to remain a dominant pattern.

Oct 9, 2026
Security Report · cyfirma.com

CYFIRMA Report Maps Cyber Threats in Australia and New Zealand

CYFIRMA’s regional report finds identity-based access is a leading ANZ attack pattern, details ransomware and sector trends, and recommends stronger authentication, supplier security, and vulnerability patching.

Oct 9, 2026
Security Report · cyfirma.com

CYFIRMA Report Finds Rising Ransomware and APT Activity Targeting Real Estate and Construction

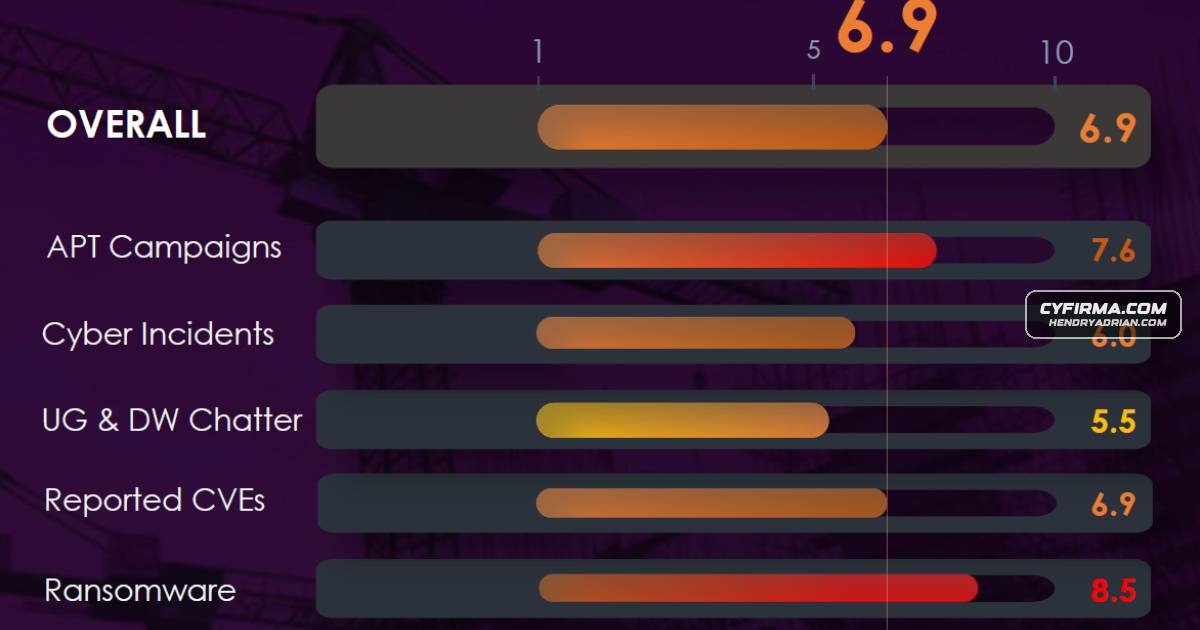
CYFIRMA’s Q2 2026 industry report says ransomware victim listings for real estate and construction rose 42.9% quarter over quarter to 290, while APT campaign activity and exposure to remote-code-execution vulnerabilities also featured prominently.

Oct 8, 2026
Security Report · sonatype.com

Sonatype Q3 2026 Index Finds Open-Source Malware Extending Supply-Chain Compromises

Sonatype counted 149,329 malicious open-source packages in Q3 2026. Its index highlights droppers and secrets theft, including Mini Shai-Hulud's credential-enabled package propagation, and urges defenders to investigate impacts beyond dependency cleanup.

Oct 8, 2026
Security Report · recordedfuture.com

Japan’s Active Cyber Defense Framework Expands Reporting and Threat-Disruption Powers

Japan’s Active Cyber Defense framework introduces mandatory reporting for designated critical infrastructure operators on October 1, 2026. Communications-analysis powers follow in 2027; the report assesses implementation, oversight, threat activity, and operational gaps

Oct 8, 2026
Security Report · thehackernews.com

Five Years of CISO Data Show Cyber Risk Moving Into Everyday Workflows

Proofpoint’s five-year CISO findings show rising concern about AI and human risk, persistent data loss, and greater board alignment alongside growing expectations—shifting security priorities toward protecting data and access within everyday workflows.

Oct 7, 2026
Security Report · cyfirma.com

CYFIRMA Report Highlights Elevated Cyber Risks Facing the Education Sector

CYFIRMA’s report finds elevated education-sector cyber risks, including state-sponsored campaigns, credential theft, rising vulnerability disclosures and 85 ransomware victims in the latest 90-day period.

Oct 7, 2026
Security Report · lookout.com

Lookout’s Q3 2025 Mobile Threat Report Highlights Persistent Phishing and Browser Vulnerability Risks

Lookout reports persistent mobile phishing exposure in Q3 2025, higher encounter rates on iOS than Android, and continued risk from unpatched browser vulnerabilities across mobile devices and apps.

Oct 7, 2026
PreviousPage 15 of 31 Next
© 2026 cyber.hendryadrian.com