CYFIRMA Report Maps Cyber Threats in Australia and New Zealand
Summary
CYFIRMA’s regional report finds identity-based access is a leading ANZ attack pattern, details ransomware and sector trends, and recommends stronger authentication, supplier security, and vulnerability patching.
Key points
- The report identifies credential-based access—including credential stuffing, infostealer data, and initial-access-broker sales—as a recurring pattern across sectors.
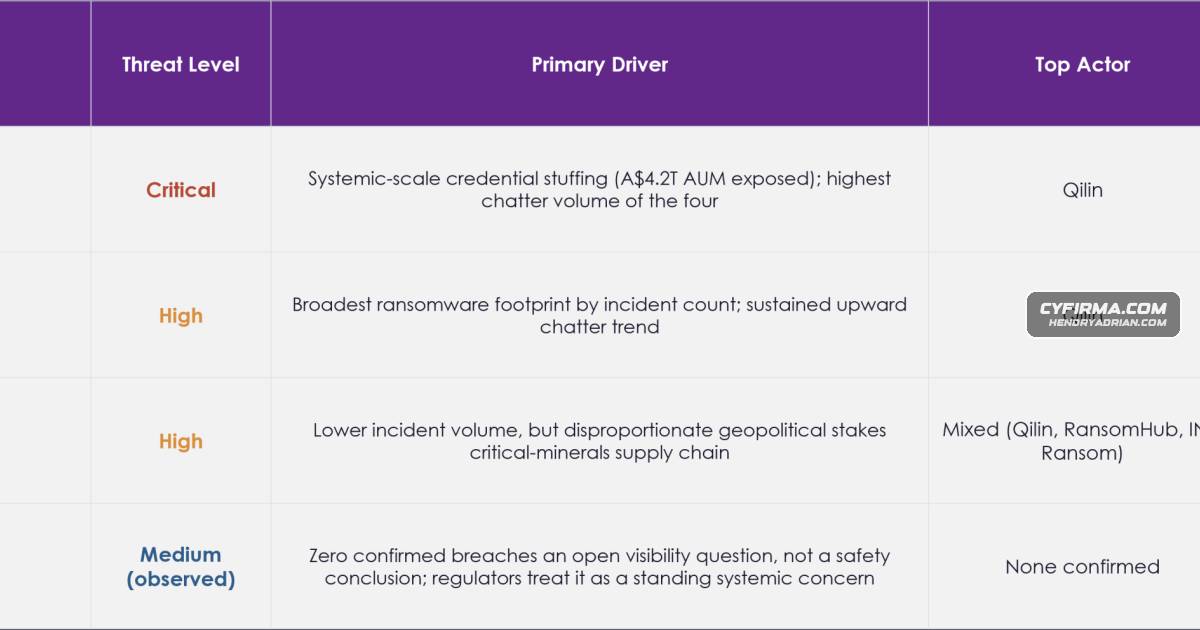
- It tracks 248 ANZ ransomware leak-site listings; these are activity claims, not confirmed breaches. Qilin had the broadest reported reach across sectors.
- The report records 28 named incidents across mining, manufacturing, and financial services, and no confirmed named deposit-taking bank victims in its tracked records.
- A credential-stuffing wave affected five superannuation funds in April 2025, with differing reported outcomes; the report attributes those differences to authentication maturity.
- The report cites Australian exploitation of vulnerabilities including CVE-2023-20198, CVE-2025-59287, and CVE-2026-41940, based on ASD/ACSC advisories.
- It highlights contractor and supplier compromise as a route into mining and manufacturing, and recommends phishing-resistant MFA, third-party risk controls, and OT asset inventory and segmentation.
Article Details
- Publisher
- CYFIRMA
- Scope
- Cyber threats affecting Australia and New Zealand, with sector assessments of Mining, Banking, Manufacturing, and Financial Services.
- Sample Size
- 248 tracked ransomware leak-site listings; 568 tracked dark-web mentions.
- Key Statistics
- The report tracks 28 named incidents: Mining 6, Manufacturing 13, Financial Services 9, and Banking 0 confirmed. The incident record includes unconfirmed leak-site claims.
- Qilin accounted for 34 ANZ leak-site listings and appeared across three of the four core sectors. Listing counts are not confirmed breaches, and the collection methodology was not independently audited.
- Financial Services recorded 82 dark-web mentions during February–July 2026, the highest volume among the four core sectors.
- ASD/ACSC responded to more than 1,200 incidents during FY24-25, an 11% year-on-year increase; 13% affected critical infrastructure.
- Of 245 vulnerabilities added to CISA KEV in 2025, 24 were known to be exploited by ransomware groups.
- Recommendations
- Mandate phishing-resistant MFA across customer- and member-facing portals and deploy credential-stuffing detection as a baseline control.
- Extend third-party risk assessments to equipment, engineering, logistics, IT, technology, and telecom suppliers.
- Require forensic verification of leak-site claims before treating listings as confirmed breaches.
- Align incident-response planning with regulator-modelled scenarios, including cyber-triggered liquidity disruption.
- Adopt AS IEC 62443 OT security controls, maintain an OT asset inventory, and segment IT and OT environments.
MITRE ATT&CK
T1078 · Valid AccountsThe report identifies compromised credentials and credential-based access as recurring intrusion mechanisms.T1110.004 · Credential StuffingCredential stuffing was the reported technique behind the April 2025 superannuation incidents.T1190 · Exploit Public-Facing ApplicationThe report describes exploitation of internet-facing perimeter systems and identifies Australian exploitation of Cisco IOS XE and cPanel & WHM vulnerabilities.T1498 · Network Denial of ServiceThe report links an April mining-related chatter spike to hacktivism and DDoS mentions; it does not provide procedure-level details.T1505.003 · Web ShellThe BADCANDY web-shell activity reportedly compromised Australian Cisco IOS XE devices.T1566 · PhishingPhishing is identified as an entry mechanism for ransomware-as-a-service activity against manufacturing.
CVE
Threat Actors
AkiraReported manufacturing claims include Consonic, Watkins Steel, and an unnamed process engineering firm; the report also attributes a financial-services claim to Akira.AnubisAttributed one ANZ manufacturing claim.ClopAttributed one ANZ manufacturing claim.DeadlockAttributed a 2026 mining-sector claim. The report treats this attribution as lower confidence because the actor was not seen elsewhere in vendor reporting.DragonForceAttributed single claims in ANZ manufacturing and financial services.fulcrumsecAttributed a 2026 mining-sector claim. The report treats this attribution as lower confidence because the actor was not seen elsewhere in vendor reporting.GhostEmperorExplicitly identified by the report as an alias of Salt Typhoon, alongside Operator Panda and RedMike.INC RansomReported to have claimed ANZ victims in mining, manufacturing, and financial services; claims are not necessarily confirmed breaches.LynxReported to have claimed a named, in-scope ANZ mining or mineral-exploration victim.Operator PandaExplicitly identified by the report as an alias of Salt Typhoon, alongside GhostEmperor and RedMike.QilinThe report attributes 34 ANZ leak-site listings to Qilin, including claims against Mining, Manufacturing, and Financial Services. Listings are not confirmed breaches.RansomHubReported to have claimed a named, in-scope ANZ mining or mineral-exploration victim.RedMikeExplicitly identified by the report as an alias of Salt Typhoon, alongside GhostEmperor and Operator Panda.Salt TyphoonDescribed as PRC-linked, with aliases GhostEmperor, Operator Panda, and RedMike. A cited joint advisory reported backbone and edge-router compromise and explicitly named Australia and New Zealand.SarcomaAttributed one ANZ manufacturing claim.Space BearsAttributed one ANZ financial-services claim.The GentlemenThe report dates its first ANZ listing to March 2026 and attributes one manufacturing claim to the group.Volt TyphoonDescribed as PRC state-sponsored and pre-positioning in critical-infrastructure IT environments. The report says a joint warning explicitly named Australia and New Zealand as affected.
Malware
BADCANDYBADCANDY web-shell campaign ~400 Australian devices compromised since Jul 2025, 150 in October 2025 alone (ASD advisory)Carbanakinternal threat monitoring identified malware indicators associated with financially motivated activity (Carbanak); these indicators are generic threat-monitoring data, not ANZ-specific, and are not reproduced in raw
Vendors
Products
Countries
AustraliaCyber Threat Landscape – Australia and New ZealandChinaAustralia holds globally significant rare-earth and critical-mineral reserves, placing the sector inside a live geopolitical contest China controls over 90% of global REE processing capacity.New ZealandCyber Threat Landscape – Australia and New Zealand
Industries
BankingBanking is the most striking finding by absence: zero named ANZ deposit-taking bank victims across a large, long-running body of tracked records.communicationsPRC state-sponsored; pre-positions in IT environments underpinning communications, energy, transport, water.EnergyPRC state-sponsored; pre-positions in IT environments underpinning communications, energy, transport, water.Financial Servicessurface across the sectors covered here credential stuffing is the clearest confirmed example (Financial Services, April 2025), and the broader pattern of access-driven rather than exploitation-driven compromiseGovernmentJoint Five Eyes advisory, August 2025, confirmed backbone/edge router compromise since 2021+ across telecom, government, transport, lodging, military sectors — Australia and New Zealand explicitly named.lodgingJoint Five Eyes advisory, August 2025, confirmed backbone/edge router compromise since 2021+ across telecom, government, transport, lodging, military sectors — Australia and New Zealand explicitly named.ManufacturingManufacturing (13), Financial Services (9)MilitaryJoint Five Eyes advisory, August 2025, confirmed backbone/edge router compromise since 2021+ across telecom, government, transport, lodging, military sectors — Australia and New Zealand explicitly named.MiningMining sits uniquely at the intersection of financially motivated ransomware and state-aligned strategic interest, given Australia’s position in the global critical-minerals supply chain.RetailPublic research identifies BFSI as the second-most-targeted sector for compromised-access sales in the tracked initial-access-broker economy, behind only retail.TelecommunicationsJoint Five Eyes advisory, August 2025, confirmed backbone/edge router compromise since 2021+ across telecom, government, transport, lodging, military sectors — Australia and New Zealand explicitly named.TransportationPRC state-sponsored; pre-positions in IT environments underpinning communications, energy, transport, water.waterPRC state-sponsored; pre-positions in IT environments underpinning communications, energy, transport, water.