CYFIRMA Flags Five Critical Vulnerabilities in Fortnightly Exploit Radar
Summary
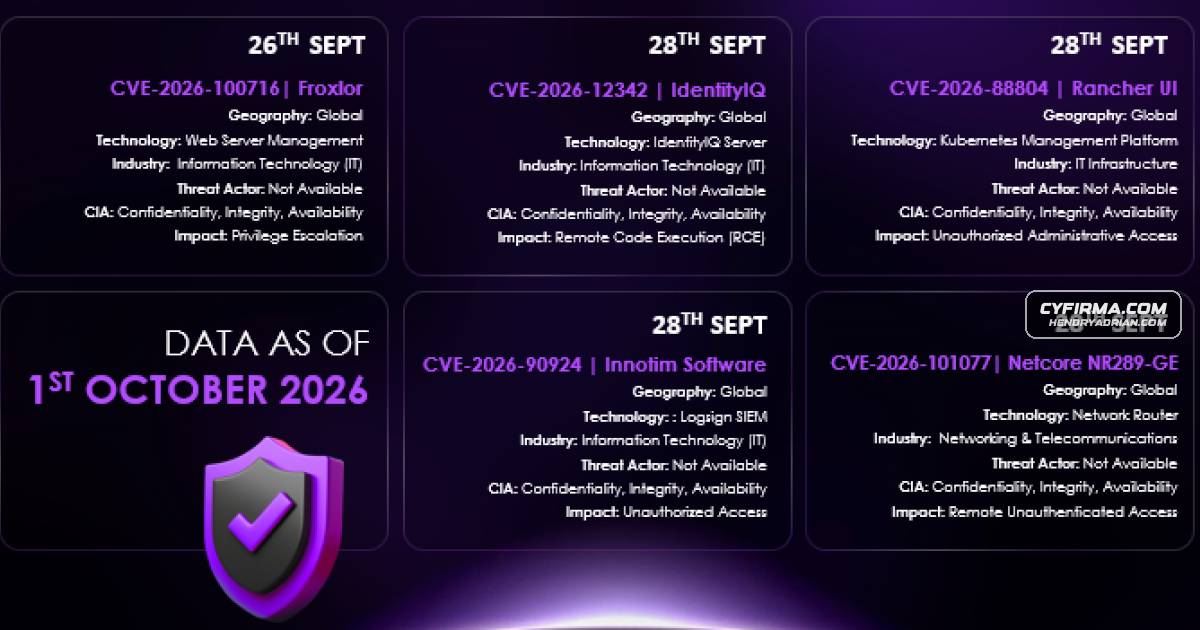
CYFIRMA's fortnightly roundup lists five critical vulnerabilities affecting Froxlor, IdentityIQ, Rancher, Logsign SIEM, and Netcore NR289-GE, with affected versions, fixes or workarounds, and remediation priorities.
Key points
- The roundup reports a 47.02% increase in observed vulnerabilities compared with the previous two weeks and identifies Linux, macOS, and Chrome among the most affected technologies.
- Five vulnerabilities are rated critical: CVE-2026-100716 in Froxlor, CVE-2026-12342 in IdentityIQ, CVE-2026-88804 in Rancher, CVE-2026-90924 in Logsign SIEM, and CVE-2026-101077 in Netcore NR289-GE.
- Fixed versions are listed for Froxlor, IdentityIQ, Rancher, and Logsign SIEM; no vendor-fixed release is identified for the affected NR289-GE firmware.
- CYFIRMA prioritizes the NR289-GE issue as an emergency and the other four as immediate remediation items, citing exploitability and potential impact.
- Recommended actions include upgrading to fixed releases, restricting management interfaces and APIs to trusted networks, changing default credentials, and isolating or replacing devices without a fix.
- The roundup says deployment counts and external exposure are not confirmed by public evidence and advises validating affected assets and exposure in customer environments.
Article Details
- Publisher
- Cyfirma Research
- Report Period
- Fortnightly; published 2026-10-08
- Scope
- Vulnerabilities observed during the fortnight, including affected products, versions, fixes, mitigations, and customer prioritization.
- Sample Size
- 5 vulnerabilities
- Key Statistics
- Vulnerabilities increased 47.02% compared with the previous two weeks.
- The report covers 5 vulnerabilities, all placed in the Critical/P1 remediation queue.
- Recommendations
- Identify affected products and versions, then apply vendor patches or upgrade to fixed versions.
- Restrict management interfaces and APIs to trusted networks, and limit Internet exposure.
- Change default or known/common credentials and enable MFA where supported.
- Monitor relevant authentication logs, system activity, and configuration changes for suspicious activity.
- Isolate or replace affected Netcore NR289-GE devices if no vendor fix becomes available.