cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3799 articles

Security News · thehackernews.com

Fortinet, Ivanti and SAP Patch Critical Vulnerabilities Across Multiple Products

Fortinet, Ivanti, and SAP released patches for critical vulnerabilities affecting FortiSandbox, Ivanti Sentry, and SAP platforms. The article reports no evidence of in-the-wild exploitation.
Jun 10, 2026
Security News · cyberscoop.com

OpenAI Says Likely China-Linked Campaigns Used ChatGPT to Target U.S. Debates

OpenAI says two likely China-linked influence clusters used ChatGPT to create anti-data-center and anti-tariff content while posing as Americans online. The campaigns showed little meaningful engagement, and OpenAI did not attribute them directly to China’s government.

Jun 10, 2026
Security News · bleepingcomputer.com

ShinyHunters Claim PeopleSoft Data Theft From More Than 100 Organizations

ShinyHunters claim they stole data from 300 Oracle PeopleSoft instances across more than 100 organizations. Nottingham University acknowledged a cybersecurity incident; a researcher also found exposed campaign tooling and scripts.

Jun 10, 2026
Security News · bleepingcomputer.com

GitHub to Require Approval for npm Scripts and Non-Registry Dependencies

npm v12 will require explicit approval for dependency install scripts, Git dependencies, and remote URL sources. GitHub recommends npm 11.16.0 or newer so developers can review warnings before upgrading.

Jun 10, 2026
Security News · cyberscoop.com

CISA Orders Federal Agencies to Prioritize Urgent Vulnerability Patching

CISA’s BOD 26-04 directs federal agencies to prioritize vulnerabilities using four urgency criteria, with fixes due in three days for flaws meeting all four. Agencies must update remediation processes, with broader compliance due within 180 days.

Jun 10, 2026
Security News · cybersecuritypulse.net

Claude Opus Surfaces Longstanding Zcash Flaw in a Week of Security News

A weekly security roundup reports that Claude Opus helped uncover a longstanding Zcash Orchard flaw, alongside updates on AI safeguards, security triage and monitoring tools, cloud-security research, and security-company funding.

Jun 10, 2026
Security News · securityweek.com

Infostealers Turn Millions of Devices Into Credential Theft Machines

Flashpoint reports more than 11.1 million devices infected with infostealers in 2025 and over 3.3 billion credentials and other identity data circulating in illicit markets. Vidar led infections in early 2026, the article says.

Jun 10, 2026
Security News · securityweek.com

Cyera Raises $600 Million at $12 Billion Valuation

Data security firm Cyera raised $600 million in a round led by Evolution Equity Partners, reaching a $12 billion valuation. The company says its platform helps organizations discover and secure data, including data accessible to AI.

Jun 10, 2026
Security News · bleepingcomputer.com

Microsoft details Windows 11 24H2 and 25H2 update installation failures

Microsoft says some upgraded Windows 11 24H2 and 25H2 devices may fail to install June 2026 cumulative updates with errors 0x80073712 or 0x800f0993. Recommended steps include restarting, removing the affected package with DISM, or an in-place upgrade.

Jun 10, 2026
Security News · securityweek.com

Aryon Security Raises $29 Million in Series A Funding

Cloud security startup Aryon Security raised $29 million in a Series A round led by Brightmind Partners. The company says its platform scans for cloud misconfigurations and enforces organization-defined security policies.

Jun 10, 2026
Security News · stepsecurity.io

StepSecurity Adds API for Compromised Open-Source Components

StepSecurity announced an API that returns compromised open-source components tied to a threat incident, including package versions, severity and verification status, for use in incident response, SIEM workflows and dependency checks.

Jun 10, 2026
Security News · zscaler.com

ThreatLabz Report Tracks Phishing and Initial-Access Trends

Zscaler's ThreatLabz 2026 report examines phishing and initial access, including reconnaissance, credential validation, phishing infrastructure, and session compromise, drawing on telemetry from Zscaler's cloud.

Jun 10, 2026
Security News · trendmicro.com

Pwn2Own Berlin 2026 Exposes Security Weaknesses Across AI Tools

Pwn2Own Berlin contestants found vulnerabilities in AI coding tools, databases, inference software, and Nvidia’s Container Toolkit. The article highlights exposed services, host-access risks, shared weaknesses in coding agents, and LLMs’ growing role in vulnerability-f0

Jun 10, 2026
Security News · bleepingcomputer.com

Varonis Tests Find OpenClaw AI Agent Could Leak Simulated Credentials and CRM Data

Varonis tested an OpenClaw email agent with four phishing simulations. It sent simulated credentials and CRM data externally when urgent requests bypassed identity checks, but blocked a malicious OAuth app. Researchers recommend tighter access limits and human approval.

Jun 9, 2026
Security News · cyberscoop.com

Microsoft Patch Tuesday Fixes Record 206 Vulnerabilities

Microsoft’s latest Patch Tuesday fixed 206 vulnerabilities, its largest monthly batch on record. Three were publicly known but not exploited at release; a separate May 19 update patched an actively exploited Microsoft Defender zero-day.

Jun 9, 2026
Security News · bleepingcomputer.com

Microsoft Releases June 2026 Windows 11 Patch Tuesday Updates

Microsoft released KB5094126 and KB5093998 for Windows 11 versions 25H2/24H2 and 23H2, including June 2026 Patch Tuesday security fixes and other feature and reliability improvements. Microsoft reports no known new issues.

Jun 9, 2026
Security News · bleepingcomputer.com

Microsoft’s June 2026 Patch Tuesday Fixes 200 Flaws, Including Three Publicly Disclosed Zero-Days

Microsoft’s June 2026 Patch Tuesday fixes 200 flaws, including three publicly disclosed zero-days with no known in-the-wild exploitation; updates include an HTTP/2 DoS mitigation and a BitLocker bypass fix.

Jun 9, 2026
Security News · bleepingcomputer.com

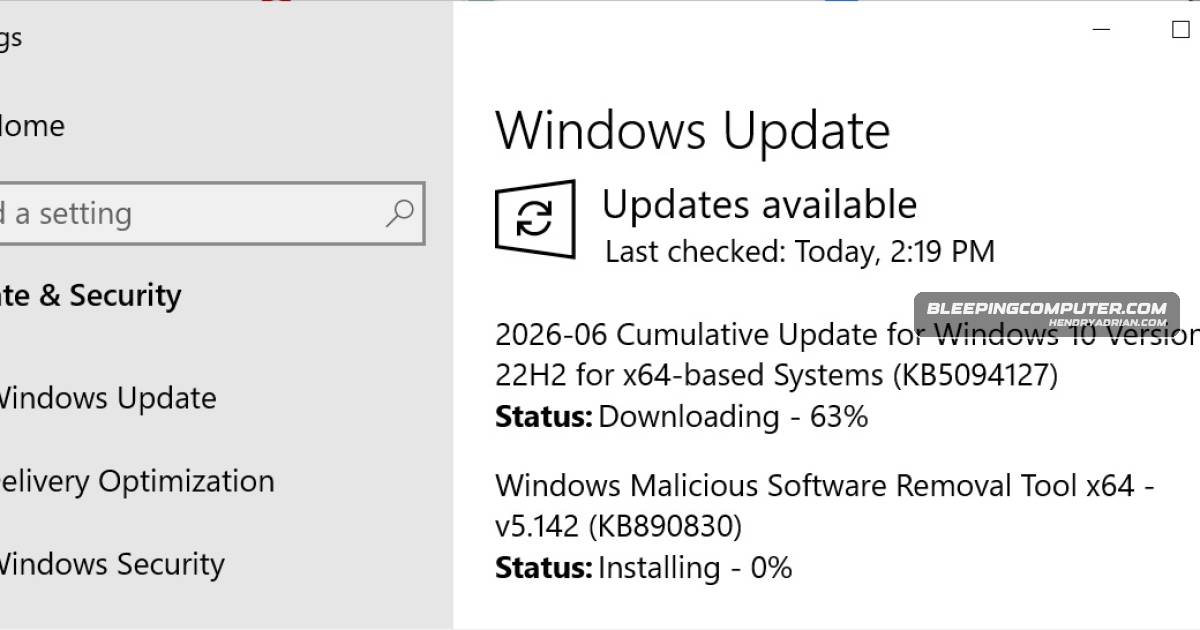
Microsoft Releases Windows 10 KB5094127 Security Update

Microsoft released Windows 10 KB5094127 with June 2026 Patch Tuesday fixes and Secure Boot certificate rollout monitoring. Microsoft also describes a BitLocker recovery issue affecting some configurations and a temporary workaround.

Jun 9, 2026
Security News · securityweek.com

Microsoft’s June 2026 Patch Tuesday Fixes About 200 Vulnerabilities

Microsoft’s June 2026 updates fix about 200 vulnerabilities, including three publicly disclosed flaws. None appears exploited in the wild; nearly 40 issues are rated critical.

Jun 9, 2026
Security News · securityweek.com

Adobe Patches 123 Vulnerabilities Across 11 Products

Adobe fixed 123 vulnerabilities across 11 products, including critical code-execution flaws in Campaign Classic and ColdFusion. Adobe says it is unaware of in-the-wild exploitation; only those two products received priority rating 1.

Jun 9, 2026
Security News · cyberscoop.com

CISA Plans Risk-Based Prioritization for Vulnerabilities and Critical Infrastructure

CISA plans to prioritize vulnerabilities by factors including asset exposure, exploitability and known exploited status, while issuing a binding directive for federal agencies and giving critical infrastructure owners more specific protection guidance.

Jun 9, 2026
Security News · cyberscoop.com

Anthropic Releases Guarded Claude Fable 5 Model

Anthropic says Claude Fable 5 routes cybersecurity and biology queries to Claude Opus 4.8, adds safeguards, and passed testing that found no known universal jailbreaks. The company acknowledges some benign requests may be blocked.

Jun 9, 2026
Security News · securityweek.com

Anthropic Adds Cybersecurity Safeguards to Claude Fable 5 and Expands Mythos 5 Access

Anthropic says Claude Fable 5 falls back to Claude Opus 4.8 for cybersecurity and biology tasks. The company also reported red-team testing and is upgrading trusted Project Glasswing users to Mythos 5.

Jun 9, 2026
Security News · securityweek.com

Atsign Launches AI Architect to Add Security Controls to AI-Built Apps

Atsign says its AI Architect product uses a custom MCP server, cryptographic identities and policy controls to guide AI coding agents in building applications. The company claims its approach keeps credentials and resources hidden from attackers.

Jun 9, 2026
PreviousPage 92 of 159 Next
© 2026 cyber.hendryadrian.com