
StepSecurity Adds API for Compromised Open-Source Components
Summary
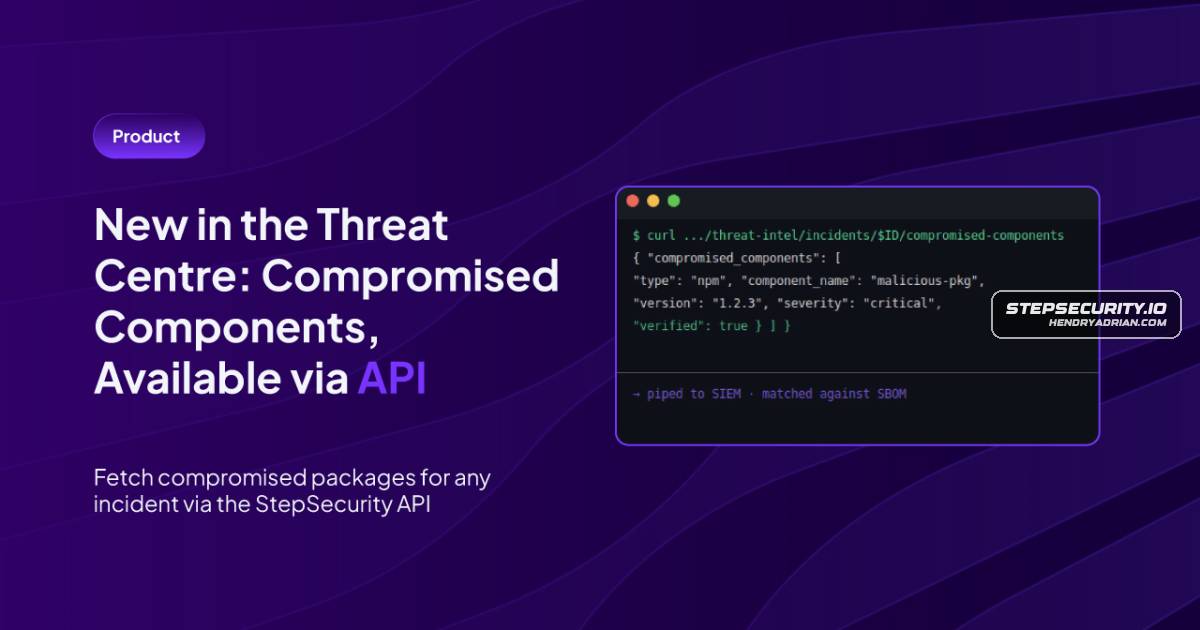
StepSecurity announced an API that returns compromised open-source components tied to a threat incident, including package versions, severity and verification status, for use in incident response, SIEM workflows and dependency checks.
Key points
- The endpoint returns compromised components for a specified incident, including ecosystem, package name, affected version, severity, verification status and a threat description.
- Teams can use the incident identifier from a Threat-Intelligence detection event to retrieve the component data programmatically.
- StepSecurity says the structured data can feed incident-response automation, SIEM enrichment and checks against an organization's SBOM or lockfiles.
- The API complements StepSecurity's existing dashboard, notifications, pull-request checks and Secure Registry controls.
- The Threat Center and endpoint are available to StepSecurity Enterprise customers.
Article Details
- Event Type
- StepSecurity announced an API endpoint that provides structured access to compromised open-source software components associated with a threat incident.
- Impact
- The endpoint returns component ecosystem, name, affected version, severity, verification status, and threat description, enabling customers to automate incident response, enrich SIEM workflows, and check exposure against dependency inventories. It is available to StepSecurity Enterprise customers.
Vendors
Products
NPM Package Compromised Updates CheckPull request checks like the NPM Package Compromised Updates Check already block your developers from pulling in versions of packages known to be compromised, right at the pull request.StepSecurity Secure RegistryThe Secure Registry enforces your controls at install time. It sits between your developers, CI runners, and the public registries, evaluating every install request against your configured controls, whether the installThreat CenterThe Threat Center is where all of that intelligence comes together: a real-time feed of active incidents, historical records, affected packages, and recommended remediation, all in one view. Threat Intelligencea package being compromised and that compromise being exploited keeps shrinking. StepSecurity Threat Intelligence was built for exactly this: it detects active supply chain compromises within minutes using the