cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3793 articles

Security News · bleepingcomputer.com

SOCRadar Links FortiBleed Campaign to INC and Lynx Ransomware

SOCRadar says artifacts link FortiBleed, a Fortinet credential-theft operation, to INC and Lynx ransomware negotiation panels. Researchers report targeting over 430,000 firewalls and suspect an undisclosed Nextcloud zero-day was used.
Jul 1, 2026
Security News · chainalysis.com

OFAC Adds 134 Crypto Wallets to ISIS-K Sanctions Designation

OFAC added 134 cryptocurrency wallets to its ISIS-K designation; Tether froze balances on 131 TRON addresses. In a separate action, OFAC sanctioned people and companies linked to PCC’s crypto-enabled laundering.

Jul 1, 2026
Security News · bleepingcomputer.com

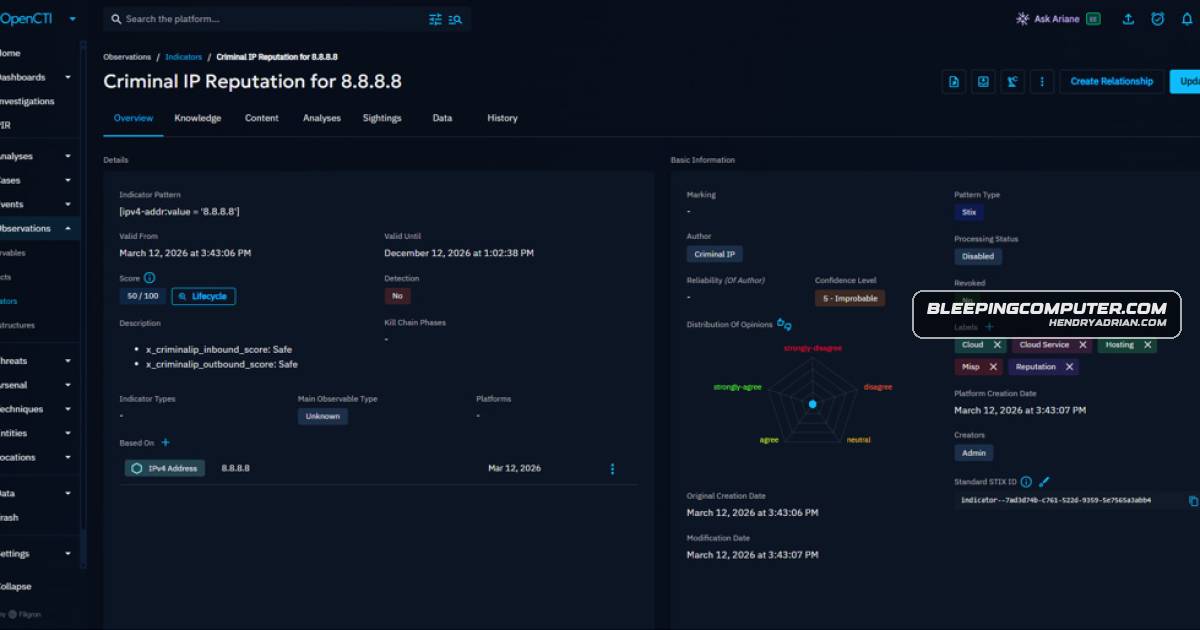
Criminal IP Integration Adds Threat Intelligence Enrichment to OpenCTI

Criminal IP says its OpenCTI connector enriches IPs, domains, and URLs with risk scores, infrastructure links, CVE data, behavioral signals, and phishing analysis for investigation and triage.

Jul 1, 2026
Security News · bleepingcomputer.com

Microsoft 365 Password-Spraying Campaign Compromised 78 Accounts

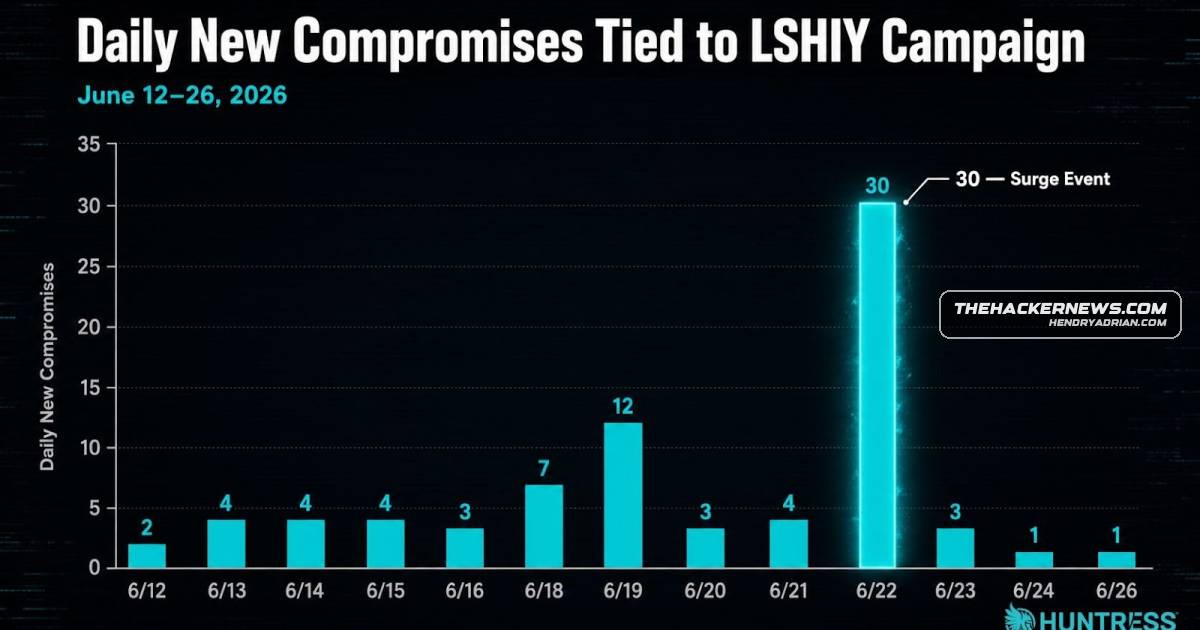
Huntress says a two-week password-spraying campaign generated over 81 million Microsoft 365 login attempts and compromised 78 accounts across 64 organizations, exploiting exposed credentials and Conditional Access gaps around ROPC.

Jul 1, 2026
Security News · thehackernews.com

Scattered Spider Suspect Extradited to U.S. to Face Hacking Charges

Peter Stokes, 19, was extradited from Finland to face U.S. hacking, conspiracy and fraud charges tied to alleged Scattered Spider intrusions. Prosecutors say one 2025 attack sought $8 million in cryptocurrency; Stokes is presumed innocent.

Jul 1, 2026
Security News · securityweek.com

Microsoft Adds Teams Controls to Identify and Approve External Bots

Microsoft announced a Teams admin policy that detects external bots, identifies them in the meeting lobby, and requires organizer approval before admission. Admins can assign the policy to users or groups, and Microsoft is retiring CAPTCHA verification.

Jul 1, 2026
Security News · cyberscoop.com

U.S. Lifts Export Controls on Anthropic’s Fable 5 and Mythos 5 After Guardrail Agreement

Anthropic says Fable 5 and Mythos 5 are again publicly available after agreeing with the Commerce Department to add safeguards targeting jailbreaks. The decision follows an Amazon report and debate over AI policy and routine cyberdefense use.

Jul 1, 2026
Security News · cyberscoop.com

Cisco Talos Identifies ARToken Phishing Platform With BEC Features

Cisco Talos identified ARToken, an affiliate platform linked to EvilTokens that targets Microsoft 365 accounts and can bypass MFA. Its BEC features include inbox rule manipulation, shared access links and a seven-layer anti-analysis system.

Jul 1, 2026
Security News · forcepoint.com

Forcepoint Identifies World Cup 2026 Scams Targeting Crypto Wallets, Ticket Buyers and FIFA Lottery Seekers

Forcepoint X-Labs identified three World Cup 2026 scams: a Stake.com-impersonating wallet drainer, a SeatGeek typosquatted ticket site, and FIFA lottery emails seeking personal data and potentially enabling advance-fee fraud.

Jul 1, 2026
Security News · darkowl.com

Cybersecurity Roundup: Tchap Breach, Phishing Campaigns and Threat Actor Arrest

This roundup covers a breach of France’s Tchap messaging service, phishing and ransomware-group activity, an arrest in Spain over government data leaks, a website malware campaign, botnet expansion, and a spear-phishing campaign targeting Afghan officials.

Jul 1, 2026
Security News · bleepingcomputer.com

Microsoft Targets 2029 for Post-Quantum Cryptography Transition in Critical Services

Microsoft says it will move critical products and services to post-quantum cryptography by 2029, citing a shifting quantum-risk horizon and urging organizations to prepare. It did not specify what advances prompted the acceleration.

Jul 1, 2026
Security News · bleepingcomputer.com

BioShocking Prompt Injection Tricked Six AI Browser Agents in LayerX Test

LayerX says its BioShocking proof of concept tricked six AI browser agents into treating sensitive actions as a game. The researchers say ChatGPT Atlas received the only effective fix; the PoC did not perform malicious actions.

Jul 1, 2026
Security News · thehackernews.com

Huntress Says Azure CLI Password-Spray Campaign Compromised 78 Accounts

Huntress reports that a password-spray campaign made over 81 million Azure CLI login attempts from June 12–26, 2026, compromising 78 accounts across 64 organizations. Attackers used ROPC; Huntress recommends broader MFA enforcement.

Jul 1, 2026
Security News · thehackernews.com

U.S. Lifts Export Controls, Restoring Anthropic’s Claude Fable 5

Anthropic restored Claude Fable 5 worldwide after the U.S. lifted export controls. The company says a new classifier blocks a reported jailbreak technique in over 99% of attempts; Mythos 5 remains limited to selected U.S. critical-infrastructure users.

Jul 1, 2026
Security News · cert-agid.gov.it

CERT-AGID Warns of Health Card Replacement Phishing Campaigns in Italy

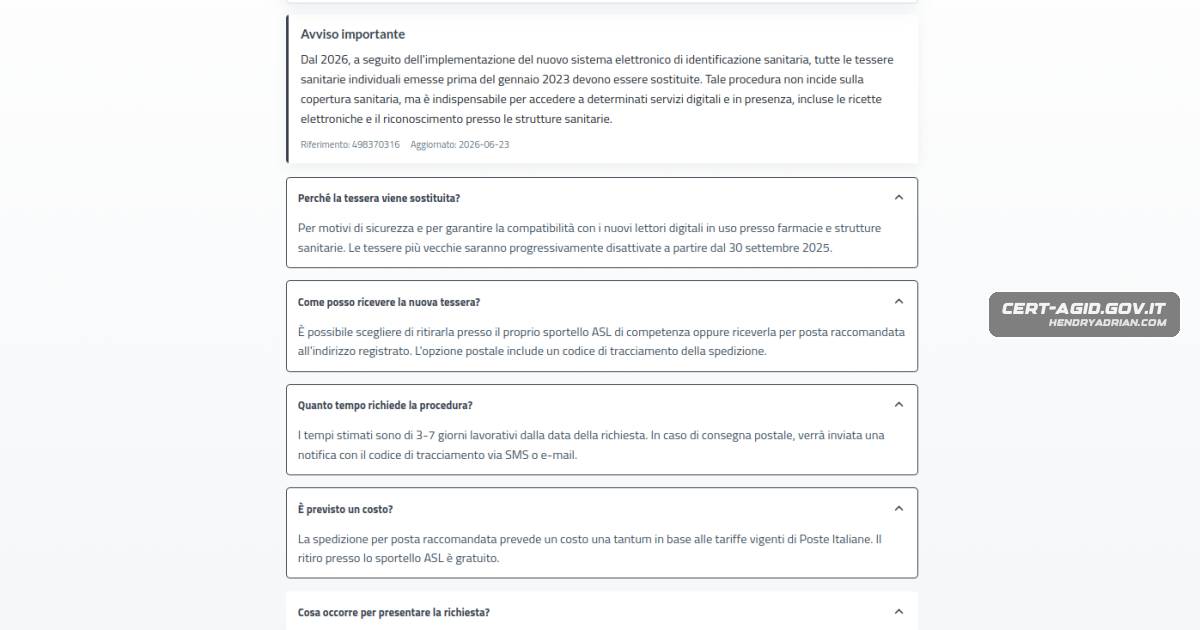
CERT-AGID reports active campaigns impersonating Italy’s Ministry of Health to steal personal and payment data through fake health card replacement notices and staged forms. It requested domain takedowns and shared indicators with accredited entities.

Jul 1, 2026
Security News · securityweek.com

Google Updates Chrome 150 Patch Count to 433 Vulnerabilities

Google revised Chrome 150’s patch count from 382 to 433 vulnerabilities. The initial report listed 15 critical and 67 high-severity flaws; Google’s advisory did not report in-the-wild exploitation of the flaws.

Jul 1, 2026
Security News · cyberscoop.com

Vought Says Administration Will Work on Rebuilding CISA After Major Staffing Cuts

Russell Vought said the administration is willing to work with DHS Secretary Markwayne Mullin on CISA staffing. The agency has lost more than 1,000 of roughly 3,400 staff; nearly 200 job offers are expected amid proposed fiscal 2027 cuts.

Jul 1, 2026
Security News · therecord.media

CIA Restructures Cyber and Technology Operations, Speeds Tech Adoption

CIA Director John Ratcliffe outlined agency changes including elevating its Center for Cyber Intelligence, refocusing its digital organization on cybersecurity and infrastructure, and cutting technology adoption time from nearly three years to about six months.

Jul 1, 2026
Security News · enisa.europa.eu

ENISA Opens Survey for 2027 NIS360 Cybersecurity Assessment

ENISA has opened data collection for its 2027 NIS360 assessment of cybersecurity maturity and criticality in high-criticality sectors. The survey closes on 30 October 2026.

Jul 1, 2026
Security News · thehackernews.com

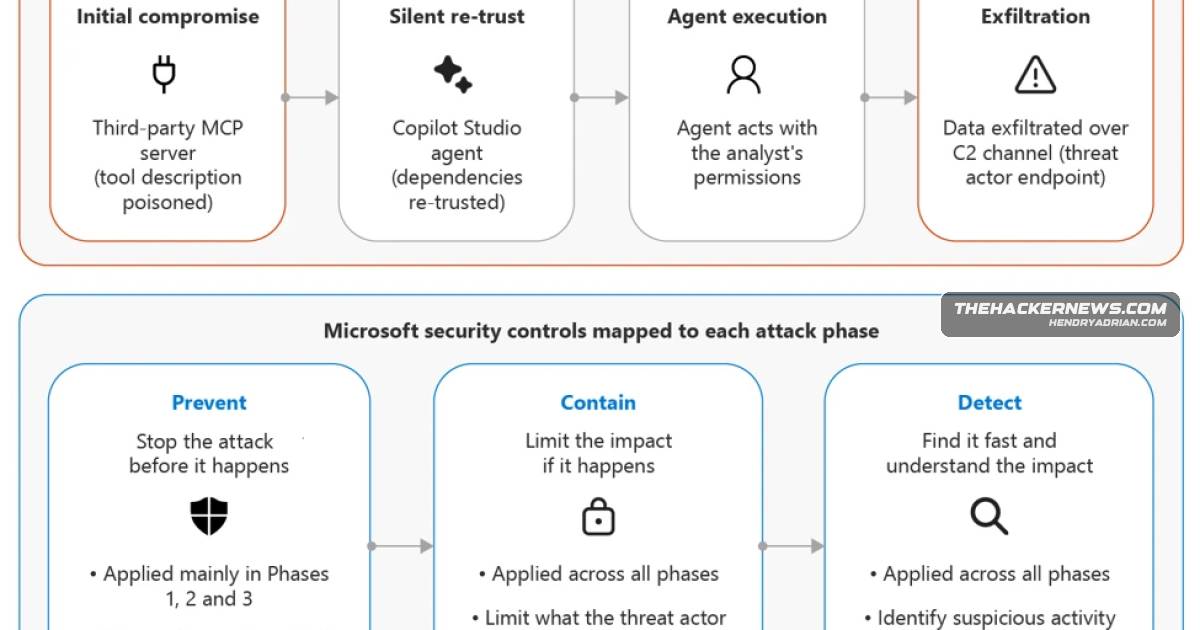
Microsoft Warns Poisoned MCP Tool Descriptions Can Steer AI Agents to Exfiltrate Data

Microsoft warns that attackers can alter MCP tool descriptions to steer connected AI agents into collecting and sending company data. It recommends reviewing tool changes, restricting access and requiring approval for risky actions.

Jun 30, 2026
Security News · wiz.io

Wiz Adds Image-Migration Features to Help Teams Harden Containers Against AI-Era Threats

Wiz says WizOS hardened container images reduce CVEs and image size, and announces tools to prioritize migrations and guide fixes through AI coding agents. Secure Architecture Opportunities is in public preview; related features are generally available.

Jun 30, 2026
Security News · bleepingcomputer.com

Fake Perplexity Chrome Extension Intercepted Searches and Collected Browsing Data

Microsoft researchers found a fake Perplexity Chrome extension routing searches through attacker infrastructure and collecting browsing activity. They found no evidence it stole credentials and advised users to remove it and rotate critical passwords.

Jun 30, 2026
Security News · cyberscoop.com

DHS to Replace CIPAC With ANCHOR-CI Critical Infrastructure Cyber Council

DHS plans to replace CIPAC with CISA-managed ANCHOR-CI, a forum for government and critical-infrastructure stakeholders to discuss cyber threats and resilience. DHS says meetings will be exempt from the Federal Advisory Committee Act.

Jun 30, 2026
Security News · bleepingcomputer.com

Microsoft Adds Teams Policy Requiring Approval for External Bots

Microsoft added a Teams admin policy that detects potential external bots, places them in the meeting lobby, and requires organizer approval before they can join—even when other participants can bypass the lobby.

Jun 30, 2026
PreviousPage 82 of 159 Next
© 2026 cyber.hendryadrian.com