
Huntress Says Azure CLI Password-Spray Campaign Compromised 78 Accounts
Summary
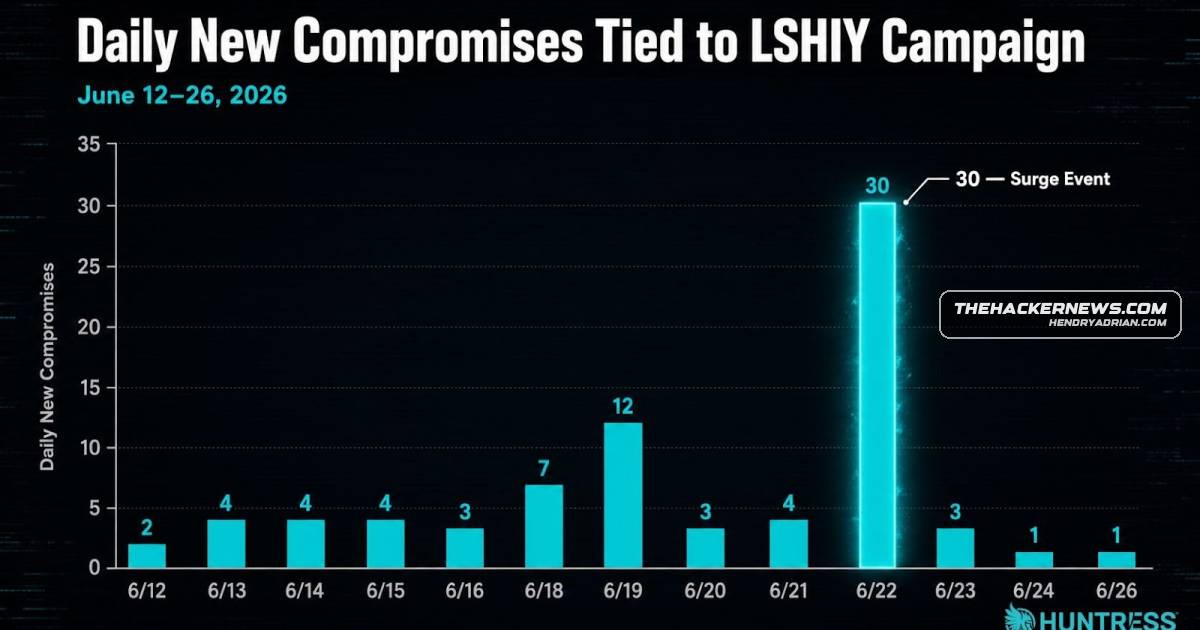
Huntress reports that a password-spray campaign made over 81 million Azure CLI login attempts from June 12–26, 2026, compromising 78 accounts across 64 organizations. Attackers used ROPC; Huntress recommends broader MFA enforcement.
Key points
- Huntress reported more than 81 million login attempts between June 12 and June 26, 2026, with at least 78 accounts compromised across 64 organizations.
- The campaign targeted Azure CLI logins using the deprecated Resource Owner Password Credentials (ROPC) flow, which Huntress said could bypass misconfigured Conditional Access protections.
- Huntress said the activity relied on previously breached, reused username and password combinations.
- Most reported password-spray activity came from an IPv6 range controlled by LSHIY LLC; the article does not identify the threat actor by name.
- Eight affected businesses reportedly had no MFA policy. Other policy gaps included limiting MFA to selected apps, user groups, or locations.
- Huntress recommends requiring MFA across all users, cloud apps, and client app types, restricting Azure CLI for non-admin users, and prioritizing response based on credential validity.
Article Details
- Event Type
- Automated password-spray campaign targeting Microsoft Azure CLI through the deprecated ROPC flow.
- Impact
- Huntress reported more than 81 million login attempts between June 12 and June 26, 2026, resulting in at least 78 compromised Microsoft accounts across 64 organizations. The ROPC flow enabled the attackers to bypass some misconfigured Conditional Access policies, including policies that did not enforce MFA for Azure CLI logins.
MITRE ATT&CK
Vendors
Products
Azure CLIResearchers uncovered a massive automated password spray campaign against Microsoft Azure CLI that used the deprecated ROPC flow to bypass Conditional Access policies and compromise 78 Microsoft accounts across 64Conditional Accesspassword spray campaign against Microsoft Azure CLI that used the deprecated ROPC flow to bypass Conditional Access policies and compromise 78 Microsoft accounts across 64 organizations.