
Criminal IP Integration Adds Threat Intelligence Enrichment to OpenCTI
Summary
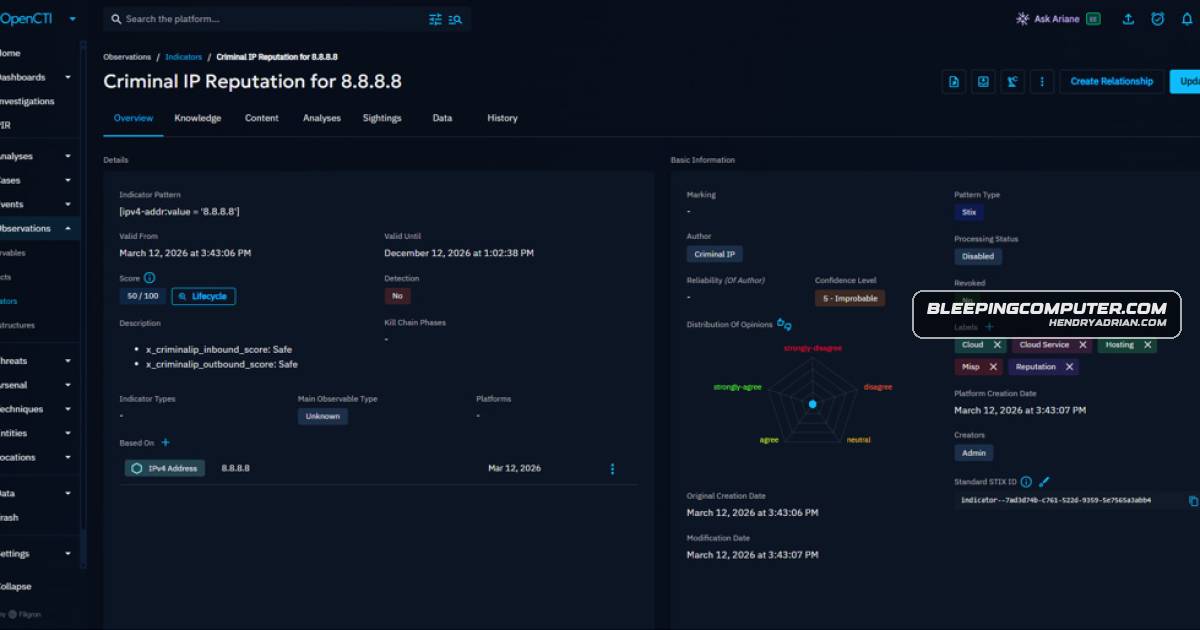
Criminal IP says its OpenCTI connector enriches IPs, domains, and URLs with risk scores, infrastructure links, CVE data, behavioral signals, and phishing analysis for investigation and triage.
Key points
- The sponsored article says the connector automatically enriches OpenCTI indicators with Criminal IP intelligence.
- Enrichment is represented as entities and relationships in OpenCTI's knowledge graph, supporting infrastructure pivots.
- The integration provides inbound and outbound risk scores, along with labels for characteristics such as VPN, proxy, and Tor use.
- It can link observed services to known CVEs to help assess potential attack surface.
- For domains and URLs, Criminal IP says its analysis identifies phishing activity, credential harvesting, suspicious files, and impersonation.
Article Details
- Event Type
- Sponsored announcement of a Criminal IP integration with OpenCTI.
- Impact
- The integration enriches IP addresses, domains, and URLs in OpenCTI with Criminal IP reputation scores, infrastructure relationships, vulnerability data, behavioral signals, and phishing analysis. The article describes capabilities for investigation, threat hunting, SOC triage, and prioritization; it reports no specific incident or confirmed impact.
Vendors
Products
Criminal IPCriminal IP integration with OpenCTI enriches IP addresses, domains, and URLs with contextual intelligence such as reputation scores, infrastructure data, vulnerability details, and phishing analysis.OpenCTICriminal IP integration with OpenCTI enriches IP addresses, domains, and URLs with contextual intelligence such as reputation scores, infrastructure data, vulnerability details, and phishing analysis.