cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security News

Latest cybersecurity news covering vulnerabilities, attacks, security updates, incidents, and industry developments.

3621 articles

Security News · securityweek.com

Senators Propose Water Cybersecurity Bill as Water Watch Center Launches

The proposed Water Cyber Shield Act would expand EPA oversight and fund water-system security. The Water Watch Center will provide managed detection and response to small utilities and develop AI-driven defenses.
Aug 11, 2026
Security News · bleepingcomputer.com

Mozilla Rotates Firefox and Thunderbird Signing Key After Exposure

Mozilla rotated and revoked a signing key after an unencrypted copy was committed to a private GitHub repository. It found no evidence of unauthorized access and advises some Linux and manual signature-verification users to update their trust data.

Aug 11, 2026
Security News · securityweek.com

Corma Emerges From Stealth With $60 Million for Defensive Cybersecurity AI

Corma announced $60 million in seed funding for an AI model and agents designed for defensive cybersecurity. The company says its system analyzes security telemetry and can detect and neutralize threats, including multi-stage intrusions.

Aug 11, 2026
Security News · bleepingcomputer.com

U.S. and South Korea Warn of Gunra Ransomware Targeting Government, Critical Infrastructure

A joint U.S. and South Korean advisory warns that Gunra targets government and critical infrastructure, exploits Fortinet flaws and other access weaknesses, and has expanded to Linux and a RaaS model. Defenders are urged to patch, segment networks and keep offline data.

Aug 11, 2026
Security News · bleepingcomputer.com

Microsoft: Storm-1175 Deploys New StormEncryptor Ransomware, Likely Exploiting N-central

Microsoft says Storm-1175, previously linked to Medusa, is deploying StormEncryptor and likely exploited CVE-2026-18577 in N-central. N-able released a hotfix; the ransomware encrypts files and threatens to leak stolen data.

Aug 11, 2026
Security News · securityweek.com

Mozilla Replaces Firefox Signing Key After Accidental Exposure

Mozilla replaced a GPG signing subkey after an unencrypted copy was accidentally committed to a private GitHub repository. Mozilla said its audit found no evidence of unauthorized access; some users must import the replacement key.

Aug 11, 2026
Security News · bleepingcomputer.com

OpenAI launches GPT 5.6 Cyber for approved security partners

OpenAI says GPT 5.6 Cyber will support vulnerability research, testing, incident response, and remediation through approved partners and security vendors. Access is limited, with safeguards including scoped engagements, monitoring, and human oversight.

Aug 11, 2026
Security News · cyberscoop.com

OpenAI Expands Daybreak Cybersecurity Program With Red-Team Model and 16 Partners

OpenAI expanded Daybreak with models for defensive security and red-teaming, and announced 16 provider partnerships. In a company-devised evaluation, it said GPT-5.6-Cyber completed 95% of complex hacking tasks versus 1.5% for Sol.

Aug 11, 2026
Security News · stepsecurity.io

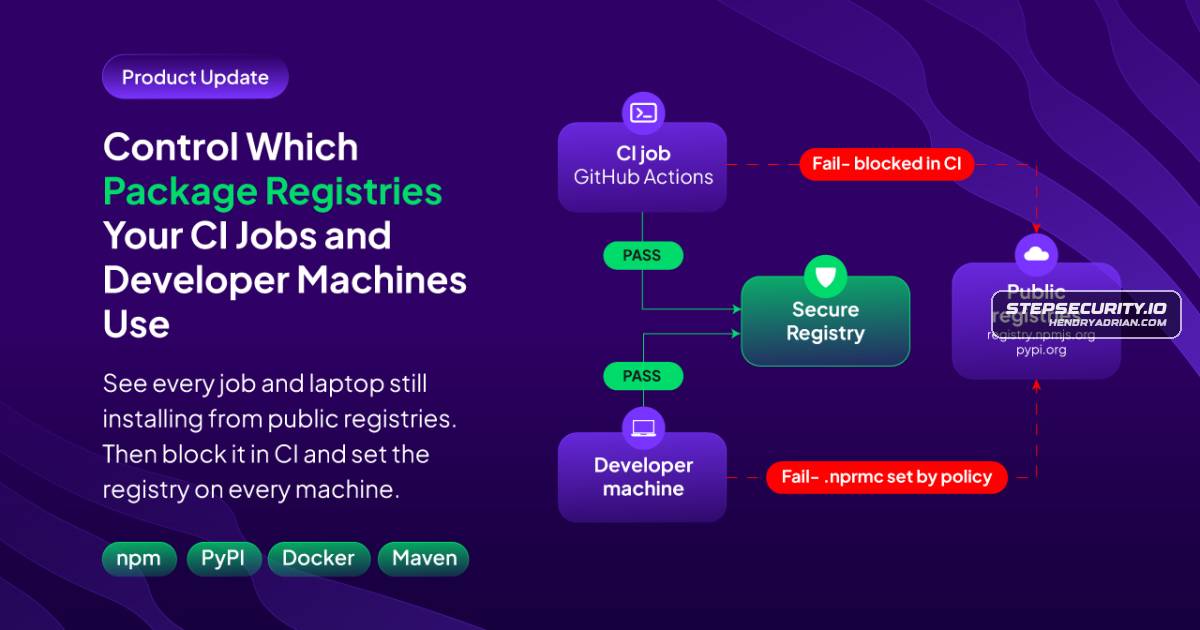
StepSecurity Details Controls for Routing CI and Developer Installs Through Private Registries

StepSecurity describes controls that detect public-registry requests from CI jobs and inspect developer-machine package settings, plus egress blocking, centralized configuration and registry policies to reduce exposure to compromised packages.

Aug 11, 2026
Security News · zscaler.com

Midnight Blizzard-Linked Campaign Abuses Hotel Wi-Fi Portals to Steal Microsoft 365 Credentials

Microsoft attributes CaptiveCrunch to Storm-2945, a Midnight Blizzard sub-cluster. The campaign manipulates hospitality Wi-Fi captive portals to redirect victims to Microsoft 365 credential theft, device-code phishing, and malware; it has also expanded to Android.

Aug 11, 2026
Security News · therecord.media

FBI and South Korea Warn Gunra Ransomware Is Targeting Critical Infrastructure

U.S. and South Korean authorities say Gunra has exploited two Fortinet flaws to access organizations, steal and encrypt data, and extort victims. Their advisory describes global targeting and a Linux-variant weakness that may enable file recovery.

Aug 10, 2026
Security News · thehackernews.com

Weekly Cybersecurity Recap: Metabase Zero-Day, Router Backdoors and MCP Supply-Chain Attacks

The weekly recap covers Metabase’s actively exploited unauthenticated SQL injection, research on Spectre v2 and webmail attacks, router backdoors, Shai-Hulud’s spread through the MCP Registry, and ongoing threat-group campaigns.

Aug 10, 2026
Security News · thehackernews.com

Microsoft Says China-Linked Storm-1175 Deploys New StormEncryptor Ransomware

Microsoft says China-linked Storm-1175 has switched from Medusa to StormEncryptor and may be exploiting an N-central flaw. The group uses remote-management and discovery tools before rapidly exfiltrating data and deploying ransomware.

Aug 10, 2026
Security News · cyberscoop.com

U.S. and South Korean Agencies Warn of Gunra Ransomware Expansion

A joint U.S. and South Korean advisory says Gunra is expanding its ransomware-as-a-service operation, recruiting penetration testers as initial access brokers and targeting government and critical infrastructure organizations worldwide.

Aug 10, 2026
Security News · cyberscoop.com

NATO Cyber Security Centre and AISLE Join ENISA’s CVE Numbering Authorities

NATO’s Cyber Security Centre can assign CVE IDs to eligible flaws across the NATO enterprise, while AISLE’s authority covers flaws in its own products. Their addition brings ENISA’s Root to 20 numbering authorities amid changes to vulnerability tracking.

Aug 10, 2026
Security News · cyberscoop.com

UK Man Linked to The Com Sentenced for Abusing 117 Girls

Justin Swaddle was sentenced to two years in prison after pleading guilty to child sexual abuse offenses and blackmail. The U.K. National Crime Agency identified 117 female victims, aged 13 to 17, and linked him to The Com.

Aug 10, 2026
Security News · securityweek.com

OpenAI Flags Upcoming Astra Model for Critical Cybersecurity Risk

OpenAI reportedly assessed its unreleased Astra model as potentially reaching its critical cybersecurity-risk tier and paused projects lacking safeguards, including isolated testing, network restrictions and monitoring.

Aug 10, 2026
Security News · bleepingcomputer.com

The Com Member Sentenced to Two Years for Blackmail and Sextortion

Justin Swaddle was sentenced to two years in prison for blackmail and sextortion targeting nearly 120 people worldwide. The UK National Crime Agency identified 117 female victims aged 13 to 17.

Aug 10, 2026
Security News · securityweek.com

Stealthium Targets Security Blind Spots in AI Accelerators and Neo-Clouds

Stealthium says its customer-side agent analyzes neo-cloud telemetry for signs of compromise in AI accelerator environments, where conventional security tools may lack visibility. The approach is intended to detect risks such as cross-tenant leakage.

Aug 10, 2026
Security News · huntress.com

FBI Disrupted 88,000 Exchange Web Shells and Arrested Alleged HAFNIUM Co-Conspirator

A 2021 Microsoft Exchange campaign attributed to HAFNIUM compromised 88,000 servers. The FBI remotely removed web shells under a warrant, while alleged co-conspirator Xu Zewei was later arrested and extradited; the FBI also described broader infrastructure takedowns.

Aug 10, 2026
Security News · keplernewsletter.substack.com

BSI Issues CRA Guidance as Courts and Reports Address Privacy and AI Security

A roundup covers Germany’s CRA and SBOM guidance, Czech and Hungarian data-protection decisions, and reports on AI governance, privacy, agentic-system risks, and security.

Aug 9, 2026
Security News · x.com

Microsoft Reports Storm-1175 Using StormEncryptor in Possible N-able Flaw Exploitation

Microsoft reports that Storm-1175 is deploying StormEncryptor, which appends .encrypted to files. Exploitation of N-able CVE-2026-18577 is suspected but unconfirmed; Microsoft recommends patching and monitoring for associated tools.

Aug 9, 2026
Security News · therecord.media

Senate Confirms Adam Cassady as U.S. Cyber and Digital Policy Ambassador

The Senate confirmed Adam Cassady as U.S. ambassador for cyber and digital policy in a 51-47 vote. His remit follows a State Department reorganization that split the cyber policy bureau and cut staff.

Aug 8, 2026
Security News · therecord.media

NRWA and DEF CON Franklin Launch Cybersecurity Program for Small Water Utilities

The NRWA and DEF CON Franklin launched the Water Watch Center to support small U.S. water utilities. Five providers will share threat and patch intelligence, and organizers are developing digital replicas to test defensive approaches.

Aug 8, 2026
PreviousPage 63 of 151 Next
© 2026 cyber.hendryadrian.com